hack the box tier1 Crocodile
HTB WP -Crocodile
task1:
1 | What Nmap scanning switch employs the use of default scripts during a scan? |
回答:
1 | -sC 之前说过,它等同于 --script=default。在实际使用中,大家也经常把 -sC 和用于探测版本的 -sV 组合在一起,写作 -sCV |
task2:
1 | What service version is found to be running on port 21? |
探测版本用-sV参数
1 | nmap -sV 10.129.98.248 -p 21 |
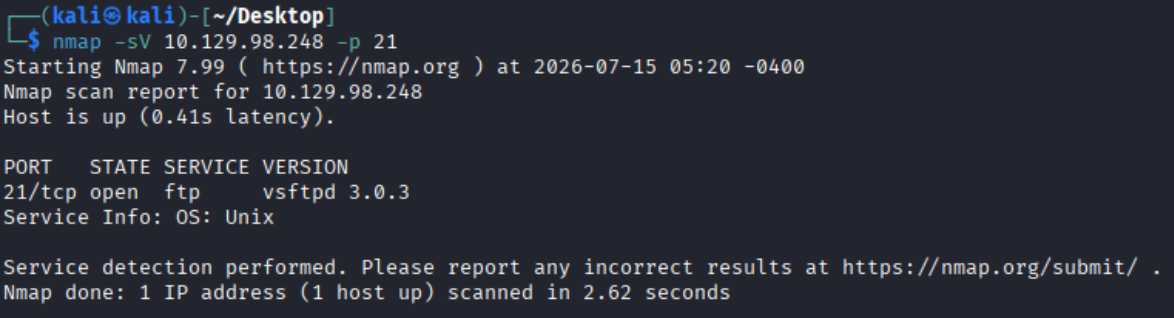
没有-p也是可以的,答案是:
1 | vsftpd 3.0.3 |
task3:
1 | What FTP code is returned to us for the "Anonymous FTP login allowed" message? |
回答:
之前好像tier0就有一样的问题是230,这个你登录上ftp服务也能看到。
1 | 230 |
task4:
1 | After connecting to the FTP server using the ftp client, what username do we provide when prompted to log in anonymously? |
回答:
1 | anonymous(tier0里面说过) |
task5:
1 | After connecting to the FTP server anonymously, what command can we use to download the files we find on the FTP server? |
回答:
1 | get(之前tier0也说过) |
task6:
1 | What is one of the higher-privilege sounding usernames in 'allowed.userlist' that we download from the FTP server? |
这需要我们连上服务 看看了:
1 | ftp 10.129.1.15(后面写wp的时候换靶机了) |
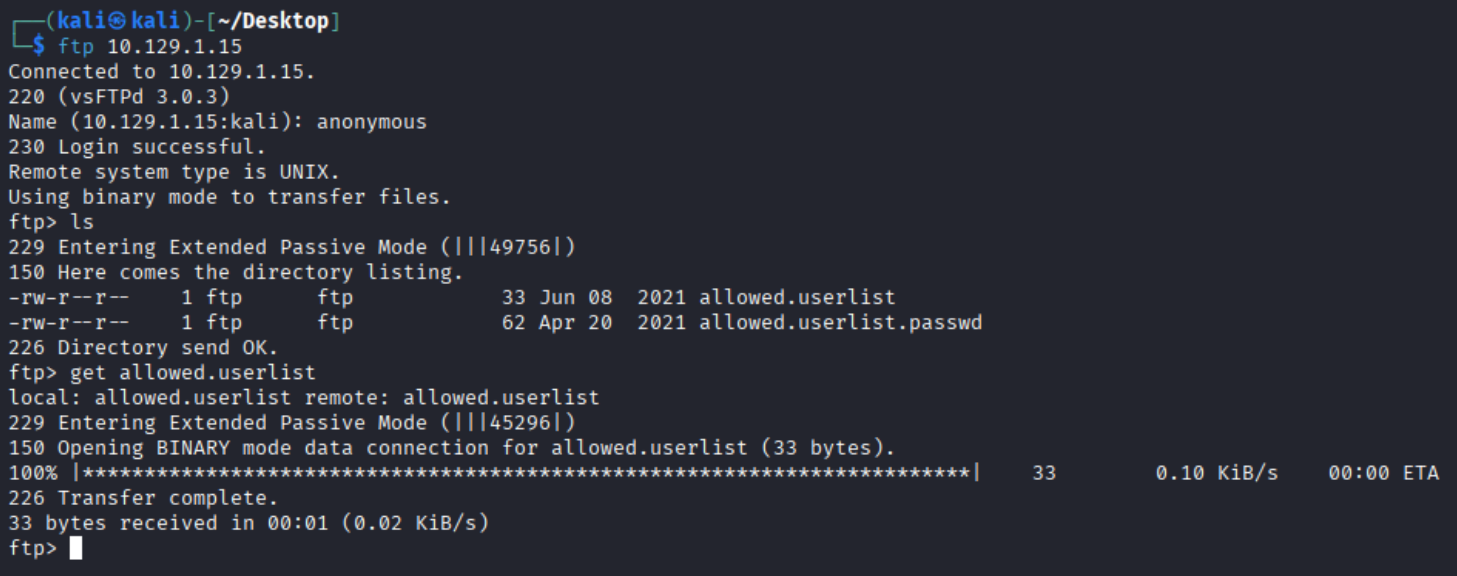
用anonymous用户空密码登录,找到文件get下来。
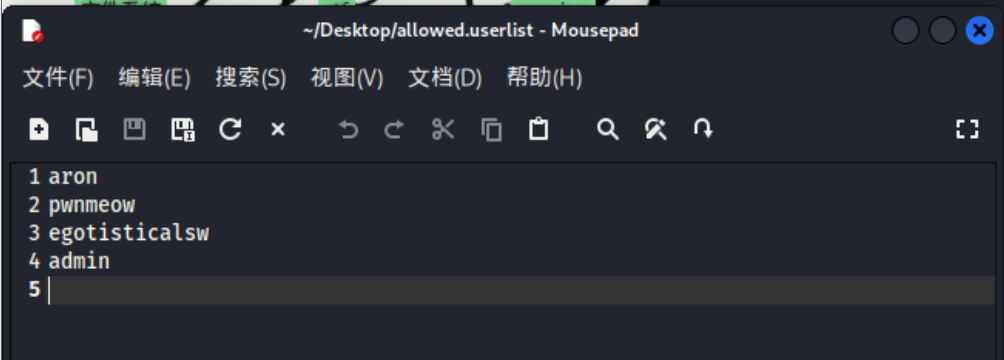
听起来权限较高的,一看就是admin:
1 | admin |
task7:
1 | What version of Apache HTTP Server is running on the target host? |
针对的是主机,那就nmap扫一下有哪些端口:
1 | nmap -sV 10.129.1.15 |
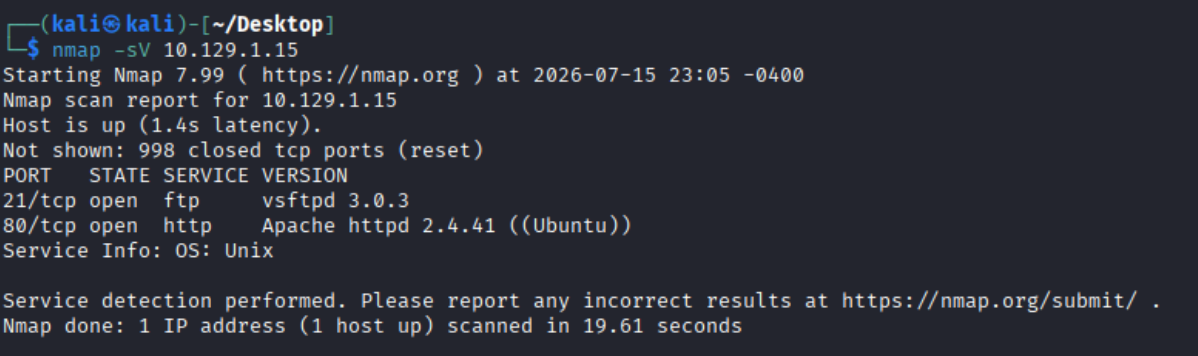
可以看到80端口开了http服务,版本是:
1 | Apache httpd 2.4.41 |
task8:
1 | What switch can we use with Gobuster to specify we are looking for specific filetypes? |
回答:
1 | -x |
task9:
1 | Which PHP file can we identify with directory brute force that will provide the opportunity to authenticate to the web service? |
其实目录暴力破解可以用dirsearch:
1 | dirsearch -u 10.129.1.15 |
开扫:
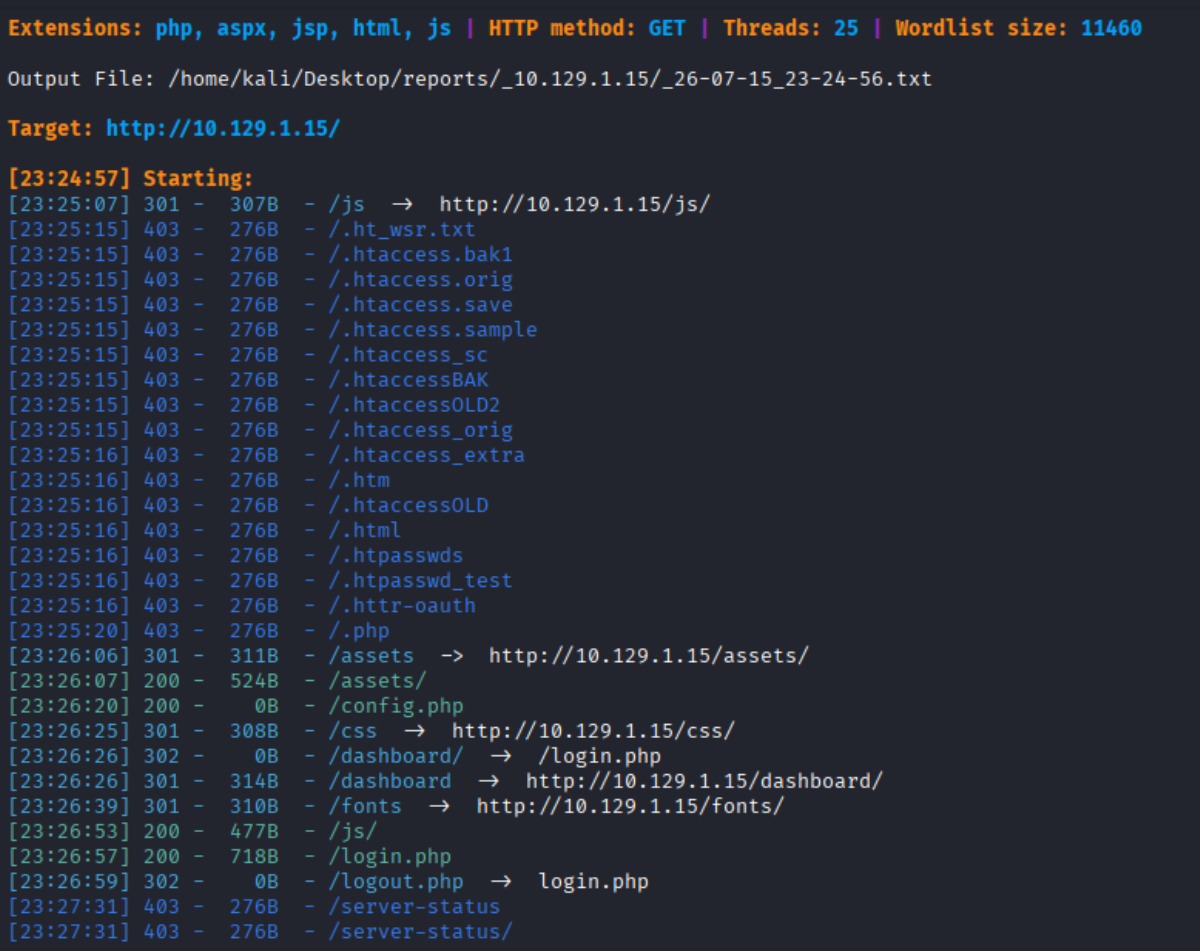
身份验证登录是:
1 | login.php |
task10:
1 | Submit the flag located in the webpage. |
找flag,得先登进去,怎么登呢,我们注意到:
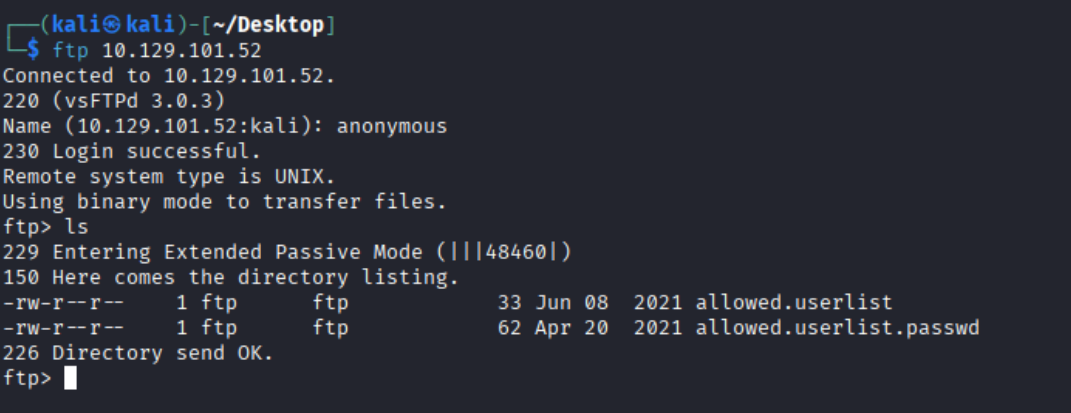
文件有userlist和他的password,都get下来:
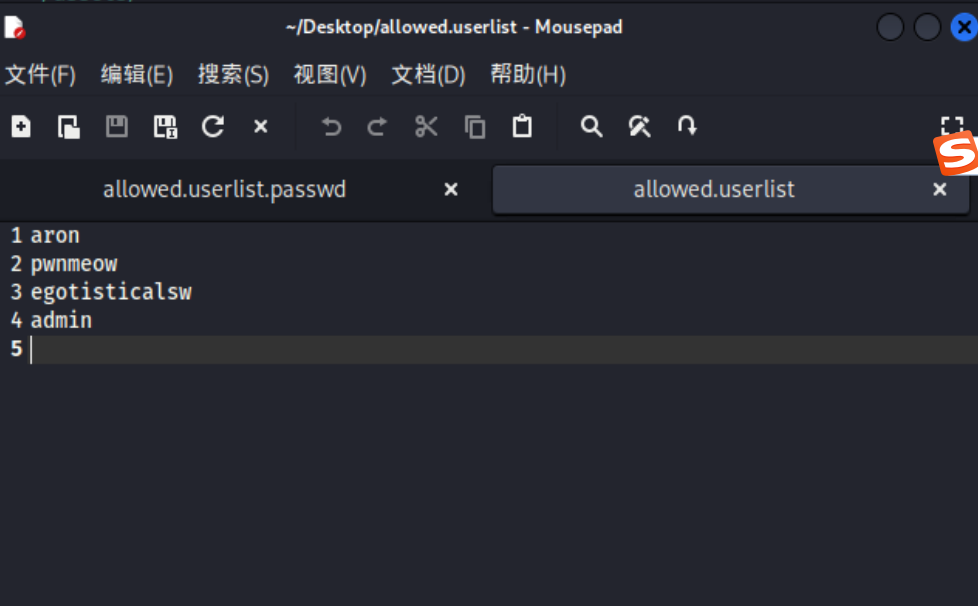
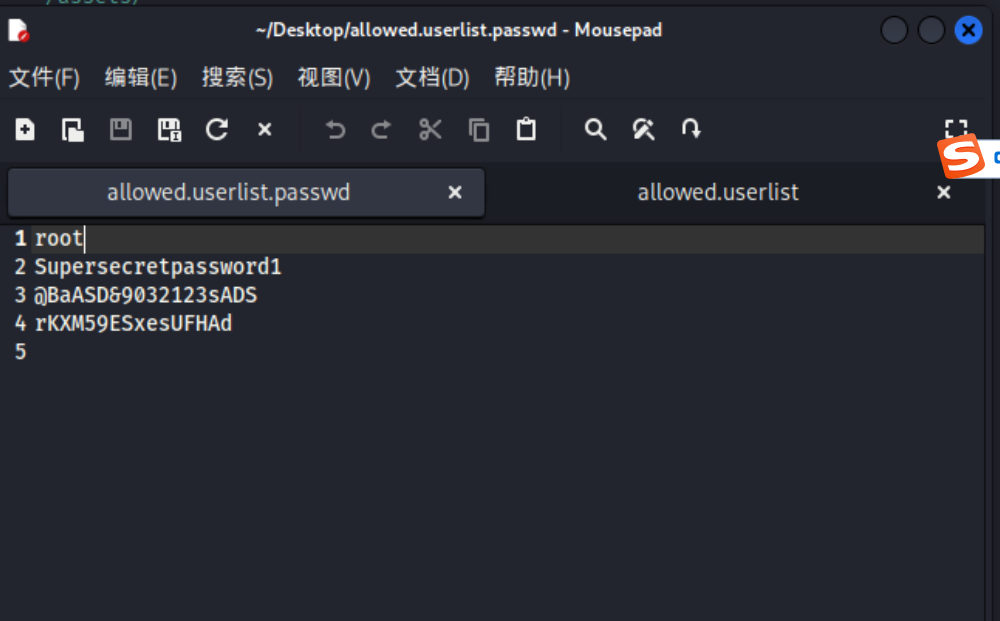
admin对应的密码是rKXM59ESxesUFHAd
在浏览器里打开http://10.129.101.52/login.php(又换靶机了,嘿嘿)
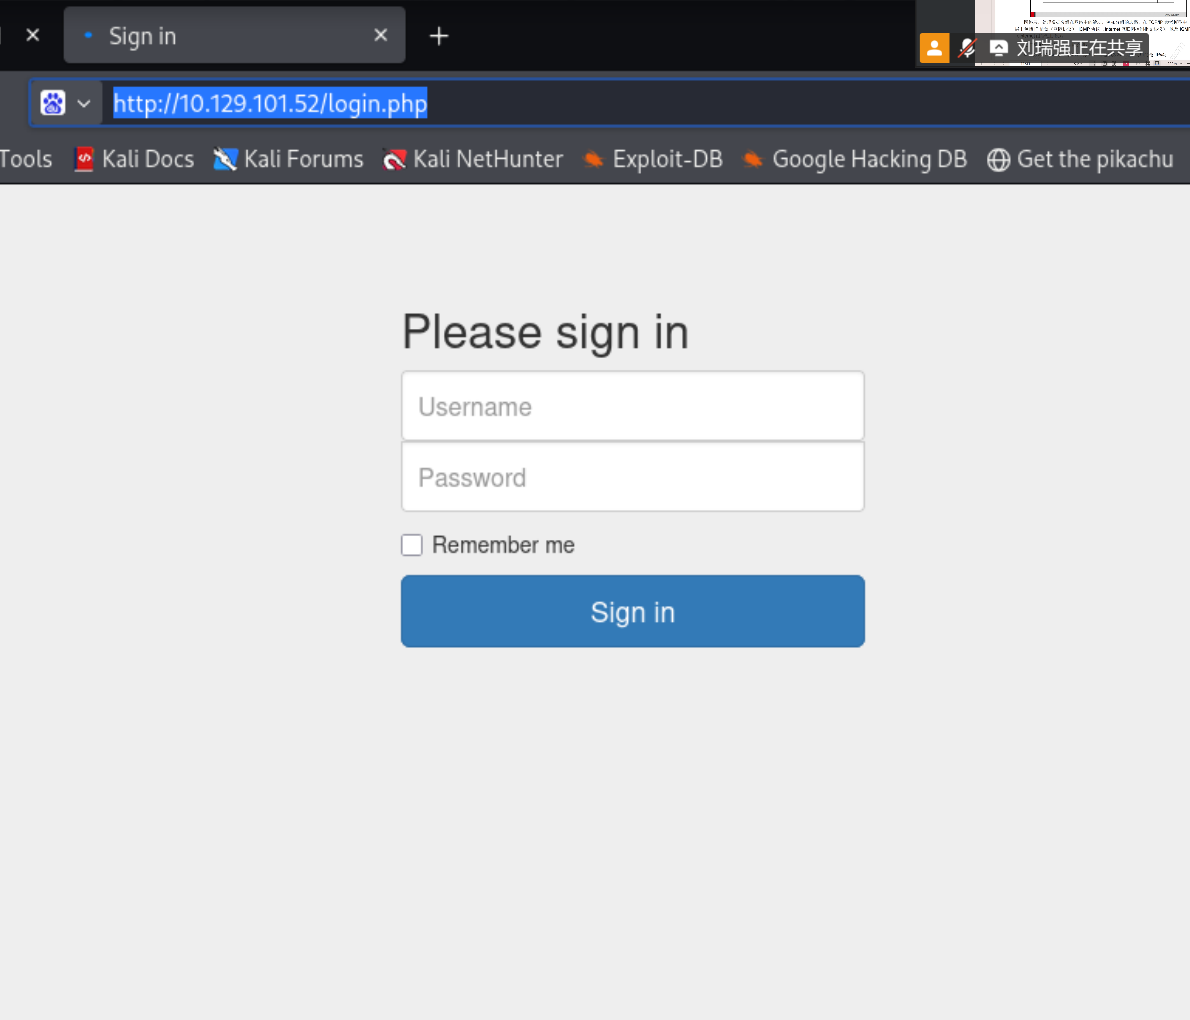
把账号密码输进去,进到仪表盘,拿到flag:
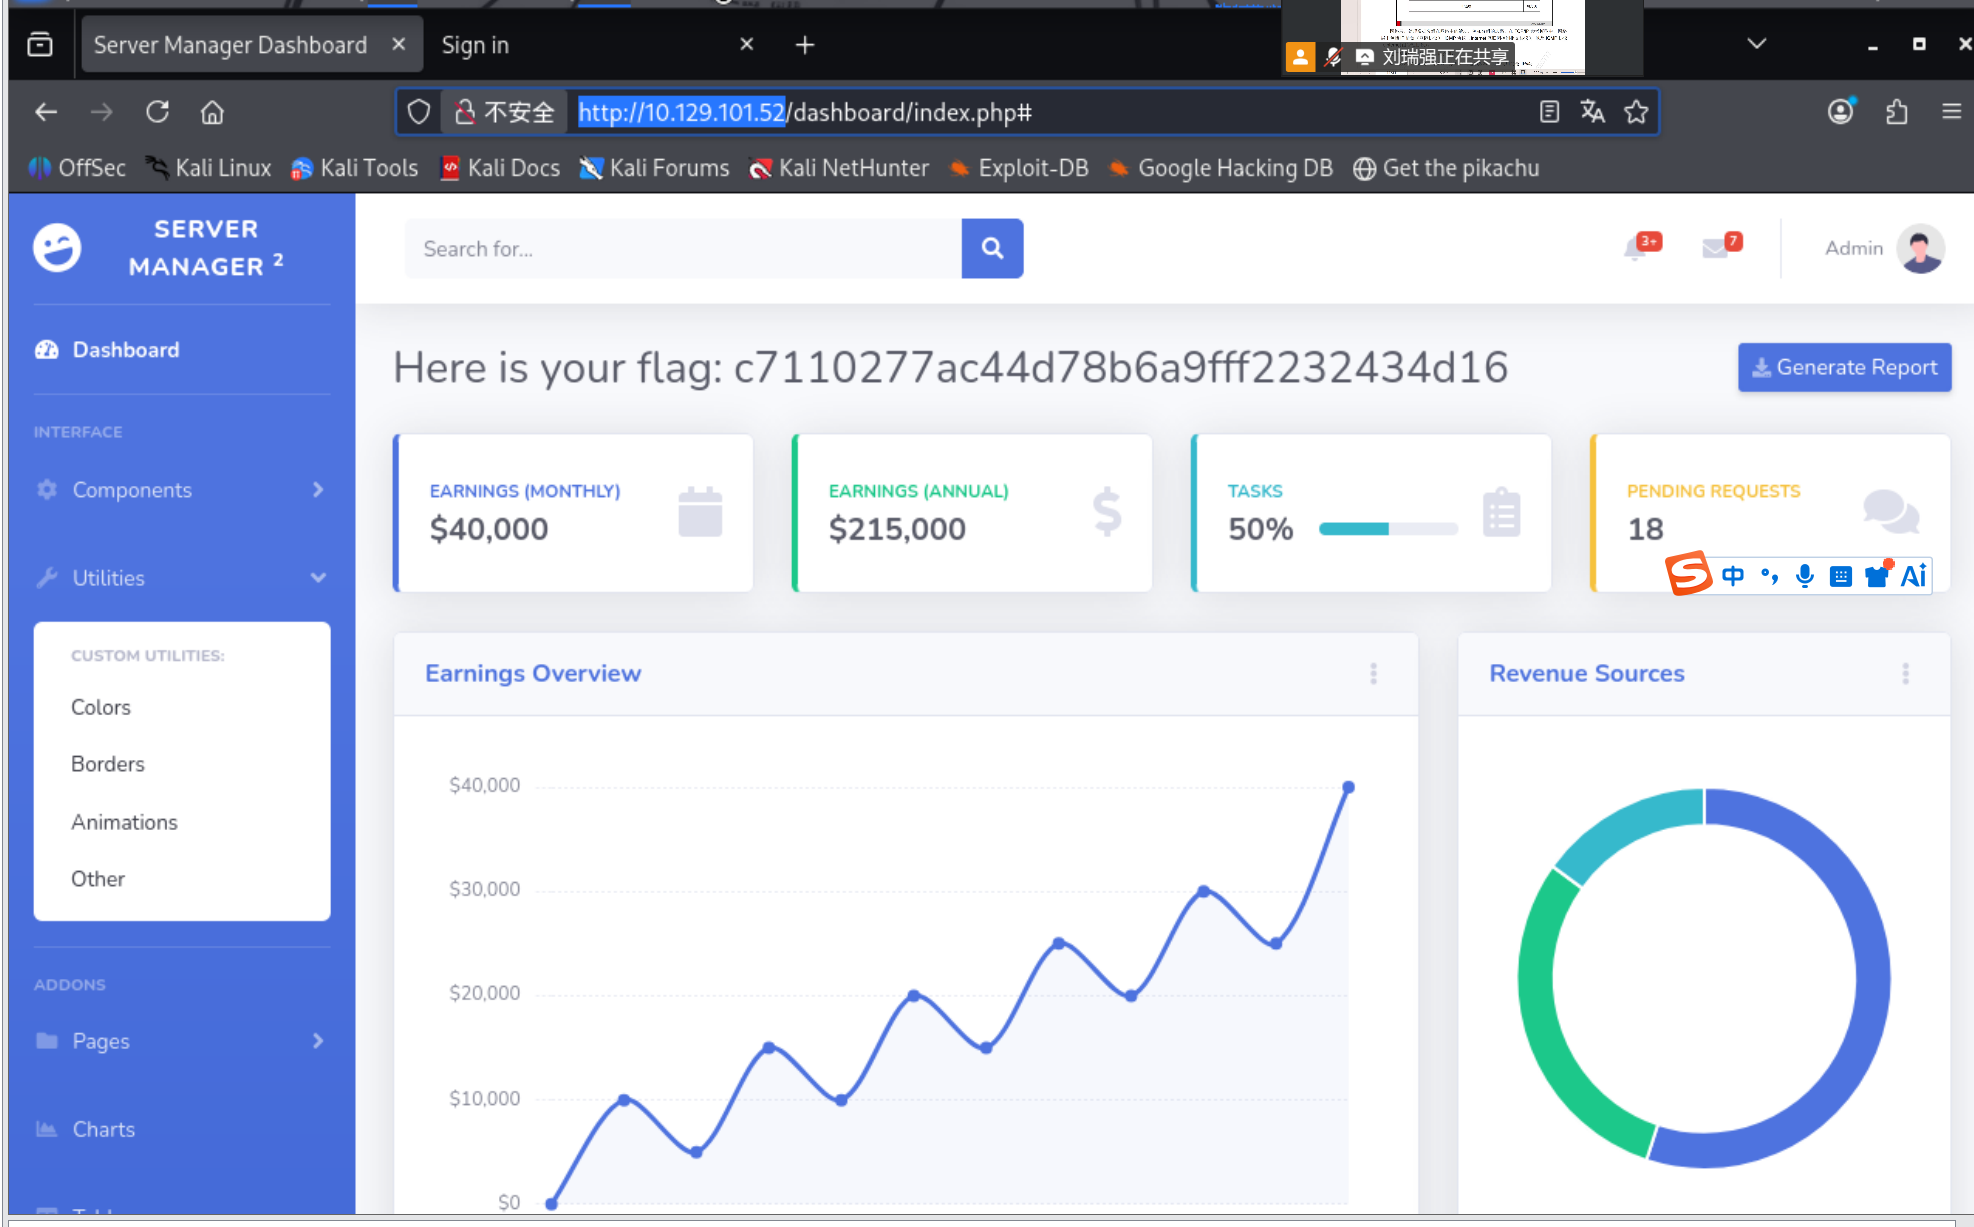
flag:
1 | c7110277ac44d78b6a9fff2232434d16 |
本博客所有文章除特别声明外,均采用 CC BY-NC-SA 4.0 许可协议。转载请注明来源 joke的小世界!
相关推荐
2026-08-15
hack the box tier1 Three
HTB WP -Threetask 112How many TCP ports are open?有多少个TCP端口是开放的? 这个需要用nmap扫一下端口: 12nmap -sV 10.129.121.197nmap -F 10.129.121.197(或者你想快一点,用fast参数) 但是两者对于端口的详细程度是不一样的。 回答: 12 task 212What is the domain of the email address provided in the "Contact" section of the website?该网站“联系我们”(或“联系方式”)部分提供的电子邮箱地址的域名是什么? 因为这个IP开了http端口,所以我们直接访问一下IP: 我们点contact(联系我们),email给了个域名: 1thetoppers.htb task 312In the absence of a DNS server, which Linux file can we use to resolve hostnames to IP...
2026-08-15
hack the box tier1 Appointment
HTB WP -Appointmenttask1:12What does the acronym SQL stand for?SQL 这个缩写代表什么意思? 回答: 1Structured Query Language task2:12What is one of the most common type of SQL vulnerabilities?最常见的 SQL 漏洞类型之一是什么? 回答: 1SQL Injection,就是SQL注入,攻击者通过在输入框中恶意输入 SQL 代码,来骗过数据库服务器,从而窃取、篡改数据,甚至直接控制整个系统。 task3:12What is the 2021 OWASP Top 10 classification for this vulnerability?这种漏洞在 2021 版 OWASP Top 10 中的分类是什么? 回答: 1A03:2021-Injection task4:12What does Nmap report as the service and version that are running on p...
2026-08-15
hack the box tier1 Responder
HTB WP -Respondertask1:12When visiting the web service using the IP address, what is the domain that we are being redirected to?当使用 IP 地址访问该 Web 服务时,我们被重定向到了哪个域名? 回答: 我们访问一下这个网站: 110.129.118.189 1unika.htb 就是被重定向到的域名。 task2:12Which scripting language is being used on the server to generate webpages?服务器上正在使用哪种脚本语言来生成网页? nmap扫一下: 12nmap -sV 10.129.118.189或者nmap -p- --min-rate 1000 -sV 10.129.118.189 12345675985 端口(WinRM 服务)Windows 远程管理(WinRM) 是 Windows 的原生远程管理协议,它基于简单对象访问协议(SOAP)与远程计算机...
2026-08-15
hack the box tier0 Meow
HTB WP -Meow前面有些引导题。 task1:12In cybersecurity, isolated environments—like Pwnbox or the vulnerable target machines—are often VMs. What does VM stand for?在网络安全领域,隔离环境(如 Pwnbox 或漏洞靶机)通常都是虚拟机。VM 是什么的缩写? 回答: 12Virtual Machine(虚拟机)虚拟机,一种通过软件模拟出的、具备完整硬件系统功能的计算机系统。 task2:12What tool do we use to interact with the operating system in order to issue commands via the command line, such as the one to start our VPN connection? It's also known as a console or shell.我们使用什么工具与操作系统交互,以便通过命令行发出命令,例如启动 ...
2026-08-15
hack the box tier0 Redeemer
HTB WP -Redeemertask1:12Which TCP port is open on the machine?机器上哪个 TCP 端口是开放的? 开扫: 1nmap -sV 10.129.91.201 可惜这1000个端口没扫到(这里不是网络问题,既然能扫1000个端口说明已经连上了) 那就只能扩大端口范围了: 1nmap -p- 10.129.91.201 其中: -p-:表示扫描全部 TCP 端口,也就是 1-65535,等价于 -p1-65535。 但是效果很慢。 可以尝试等,或者换种更快的。 决定换一个: 1nmap -Pn -sS -T4 --min-rate 100 -p- 10.129.91.207 12345其中:-Pn(可选):跳过主机发现(不先 ping),直接假设目标在线。-sS(可选):SYN 半开放扫描,只发起握手不完成,速度快。-T4:扫描速度模板,T0~T5:T3 默认,T4 较快,T5 很激进。--min-rate 100:最低发包速率,每秒至少发送 100 个探测包。 发包频率尽量小点,不然给容器扫炸了。...
2026-08-15
hack the box tier1 Sequel
HTB WP -Sequeltask1:12During our scan, which port do we find serving MySQL?在我们的扫描中,我们发现哪个端口正在运行 MySQL 服务? 回答: 那就nmap扫一下端口: 只有这一个,看它的service:tcpwrapped。 12服务:tcpwrapped(通常这个端口默认对应的服务是 MySQL,虽然在 Nmap 扫描中它的服务标识显示为 tcpwrapped,说明连接在建立后被立即关闭或受到了某种保护/限制,但 3306 确实是经典的 MySQL 默认服务端口)所以答案是3306 task2:12What community-developed MySQL version is the target running?目标运行的是哪个社区开发的 MySQL 版本? 回答: 1你需要直接尝试连接该数据库。由于这是一个新手关卡(Starting Point),它默认允许空密码无密登录。这个版本用nmap探测不到 用 mysql连接: 123mysql -h IP -P 端口 -u 用户名 -p...
评论